- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Identity and Trust?
11 November @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hello guys,
How to prevent the user on the LAN internal network from connecting to the SSL VPN/Client itself. We come across this case, where the user should only be able to access an SSL VPN/Client when they are internal, not when they are internal.
I wouldn't want users to access our own SSL/Client VPN from the internal network.
Congrats,
Cristian Rosa
Yep - it is rather old and called Location Awareness:
SmartDashboard - go to Policy menu - click on Global Properties... - expand Remote Access - click on Endpoint Connect - in the Connectivity Settings section, refer to Network Location Awareness field - select Yes - click on Configure... button - enjoy the options...
Im not real sure what you are trying to achieve here. You dont want user thats internal to be able to access VPN client??
240 / 5,000
You can restrict it, but there is no need to do this from internal.
And how would I do?
Can you help me ?
Congrats,
Cristian Rosa
Dont you have the ability to select the interface its accesible from?
i got that on several things if you open the gateway properties
I don't know how to inform. I searched but couldn't find where to configure it.
Honestly, I never heard of a way to do this specifically from the firewall object itself or even global properties. There might be some way possible via gw file trac_client_1.ttm, but not 100% sure how. Maybe someone else will chime in and confirm for you. Personally, there would need to be some sort of mechanism that would recognize user being internal that would prevent them from even being able to connect, unless they come from external source.
Lets see if someone else may have an idea, Im also interested to see the suggestions/advice or if its even possible.
Yep - it is rather old and called Location Awareness:
SmartDashboard - go to Policy menu - click on Global Properties... - expand Remote Access - click on Endpoint Connect - in the Connectivity Settings section, refer to Network Location Awareness field - select Yes - click on Configure... button - enjoy the options...
Ah, yes, good point, totally forgot about that.
Hello Abrecht,
Your help resolved my case.
Thanks a lot...
Cristian Rosa
CCSA
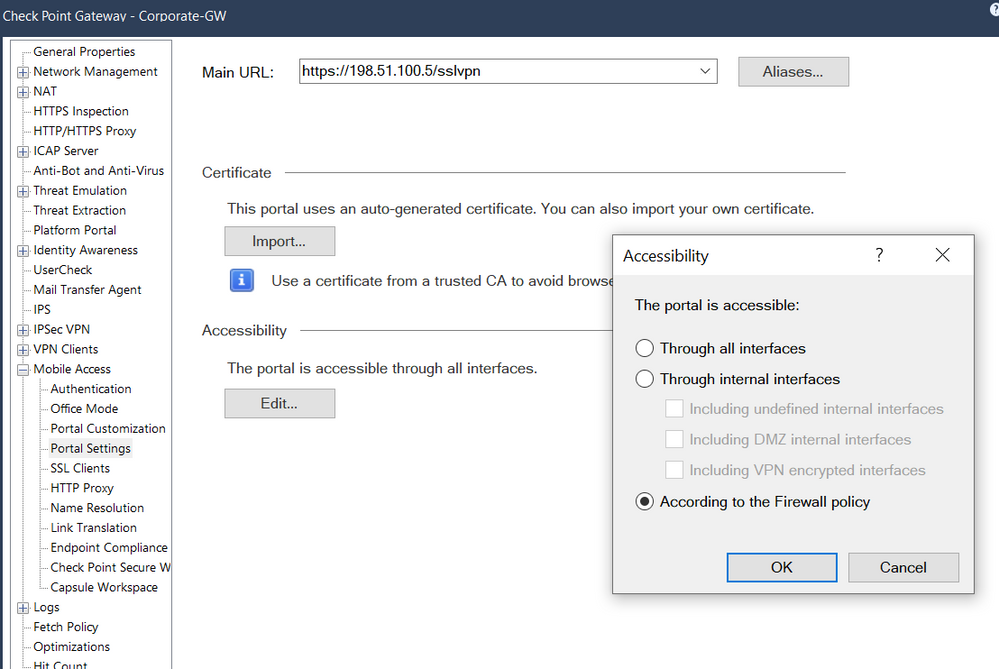
@Cristian_Rosa you can disable the implied rule for MOB access if you switch your gateway object configuration "Accessibility" to "According to the Firewall policy"
With these setting you have to define access rules for access to the MobileAccessPortal like this one
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
Tue 10 Nov 2026 @ 06:00 PM (IST)
Under the Hood: Introducing Check Point Cloud Firewall as a ServiceTue 10 Nov 2026 @ 08:00 PM (IST)
Check Point Mobile Security | Extending Zero Trust with NetskopeThu 12 Nov 2026 @ 11:00 AM (EST)
Tips and Tricks 2026 #15: Check Point MDR and Incident ResponseTue 10 Nov 2026 @ 06:00 PM (IST)
Under the Hood: Introducing Check Point Cloud Firewall as a ServiceTue 10 Nov 2026 @ 08:00 PM (IST)
Check Point Mobile Security | Extending Zero Trust with NetskopeThu 12 Nov 2026 @ 11:00 AM (EST)
Tips and Tricks 2026 #15: Check Point MDR and Incident ResponseTue 17 Nov 2026 @ 08:30 AM (EST)
Bogota Breakfast & Hack: IA bajo control y ataques en vivo con Workspace SecurityAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION