- Products
- Learn
- Local User Groups
- Partners
- More
What’s New in Identity and Trust?
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hello Experts.
I am trying to perform inbound HTTPS inspection; I do not have any private key password assigned to the certificate (wildcard certificate). While trying to import the internal server certificate for the inbound rules, I cannot import the certificate without providing the password.
Is there a way to skip/bypass the private key password section? It shows an error when I try to skip the password section.
*Note: When I provide the export password of the certificate in the private key password section, it accepts and imports the certificate.
Thanks in advance!!
Regards,
Digo.
Hello @Digo11 ,
Not sure if you were kidding when you asked for "a way to skip/bypass the private key " 🙂.
From CKP HTTPS Inspection documentation, we have the below paragraph explaining what is need:
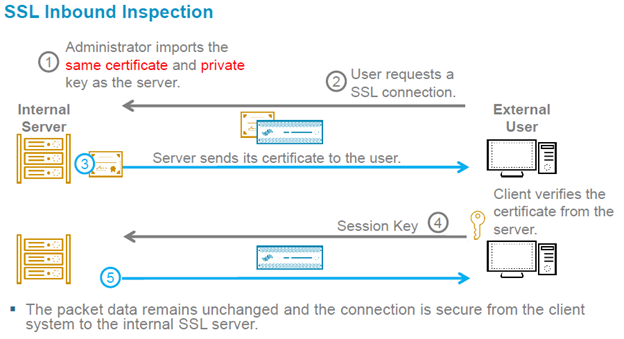
| When a client from outside the organization initiates an HTTPS connection to an internal server, the Security Gateway intercepts the traffic. The Security Gateway inspects the inbound traffic and creates a new HTTPS connection from the gateway to the internal server. To allow HTTPS Inspection, the Security Gateway must use the original server certificate and private key. The Security Gateway uses this certificate and the private key for SSL connections to the internal servers. |
Inbound HTTPS ConnectionsInbound connections are HTTPS connections that arrive from an external client and connect to a server in the DMZ or the internal network. Inbound connection flow
|
Now on your problem, you can't, because when we do INBOUND HTTP Inspection , meaning we decrypt traffic that comes from outside to our DMZ servers, the CKP HAS TO Present itself as the "original server", therefore, in order to do that, the server SSL certificate and the private key, needs to be installed to he can substitute itself into the communication.
As example:
Hopefully is clearer for you now.
Ty,
Hello @Digo11 ,
Not sure if you were kidding when you asked for "a way to skip/bypass the private key " 🙂.
From CKP HTTPS Inspection documentation, we have the below paragraph explaining what is need:
| When a client from outside the organization initiates an HTTPS connection to an internal server, the Security Gateway intercepts the traffic. The Security Gateway inspects the inbound traffic and creates a new HTTPS connection from the gateway to the internal server. To allow HTTPS Inspection, the Security Gateway must use the original server certificate and private key. The Security Gateway uses this certificate and the private key for SSL connections to the internal servers. |
Inbound HTTPS ConnectionsInbound connections are HTTPS connections that arrive from an external client and connect to a server in the DMZ or the internal network. Inbound connection flow
|
Now on your problem, you can't, because when we do INBOUND HTTP Inspection , meaning we decrypt traffic that comes from outside to our DMZ servers, the CKP HAS TO Present itself as the "original server", therefore, in order to do that, the server SSL certificate and the private key, needs to be installed to he can substitute itself into the communication.
As example:
Hopefully is clearer for you now.
Ty,
Hi Sorin_Gogean,
Good day!!
Thanks a lot for explaining the connection flow. Somehow, I was able to import the certificate by entering the "export" password that I had created at the time of exporting the certificate. I had to convert the certificate to .P12 format as it was originally in .PEM format.
I used the certificate for inbound inspection and the traffic is getting inspected as seen in the logs. I will check further and post here if assistance is required.
Thanks!!
Good job! 👍
Glad it helped @Digo11 😊
What @Sorin_G gave pretty much explains it all. Sadly, there is NO way to skip private key portion, thats the whole point actually of this process, otherwise, it would not be secure.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 9 | |
| 9 | |
| 7 | |
| 6 | |
| 6 | |
| 6 | |
| 4 | |
| 3 | |
| 3 | |
| 3 |
Tue 17 Nov 2026 @ 08:30 AM (EST)
Bogota Breakfast & Hack: IA bajo control y ataques en vivo con Workspace SecurityTue 17 Nov 2026 @ 05:00 PM (CET)
AI Security Masters: Security in the Pace of AI: From Threat to Force MultiplierTue 17 Nov 2026 @ 11:00 AM (EST)
Under the Hood: Check Point SASE | Troubleshooting Like a ProTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaTue 17 Nov 2026 @ 05:00 PM (CET)
AI Security Masters: Security in the Pace of AI: From Threat to Force MultiplierTue 17 Nov 2026 @ 11:00 AM (EST)
Under the Hood: Check Point SASE | Troubleshooting Like a ProTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseTue 17 Nov 2026 @ 08:30 AM (EST)
Bogota Breakfast & Hack: IA bajo control y ataques en vivo con Workspace SecurityAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION