- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Currently our Guestnet (for Wifi) cannot stops people from accessing “naughty” HTTPS websites because the checkpoint can’t decrypt the outbound HTTPS traffic from non-corporate devices.
Is there any way to get around this problem? As manually forcing guest users to install our Checkpoint certificate is not feasible / not enforceable, what other options do we have? (reading my mind out aloud, if we upgrade our GWs to R80.20, will SNI fix / bypass this issue so the URL inspection / categorization can be used?)
Cheers,
Hunt
Adding to what PhoneBoy wrote you can also refer to sk163594 - What's new in HTTPS Inspection starting from R80.20:
"Starting in R80.20 and R80.30 latest Jumbo Hotfix Accumulators, HTTPS Inspection offers important new features in the domains of security and usability.
To take advantage of these new capabilities, upgrade to R80.20 Jumbo Hotfix Accumulator Take 118 (and higher), or R80.30 Jumbo Hotfix Accumulator Take 111 (and higher)."
Hunt_Lee,
you're right, as @PhoneBoy mentioned SNI with URL-Filter is your solution without HTTPS-inspection.
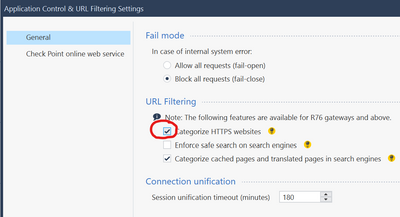
Don't forget to enable "categorize HTTPS websites"
Wolfgang
Hi all,
If i install a public CA certificate (e.g. Verisign, GoDaddy) onto my CheckPoint, and change all the outbound rules to used this new certificate for outbound traffic.
Would then my guest users traffic be able to be inspected by CheckPoint? Or would they still need to install this CA certificate manually by themselves (which is not enforceable).
Cheers,
Hunt
Yes, that's possible. If you use an SUB-CA issued from a root CA which is trusted by your client devices everything would be fine.
Any certificate issued from a trusted CA or trusted sub CA will be trusted on you clients. All depends on the trusted root CAs on your clients. You can use the defaults from Windows, Linux, MACs, Android, IOS etc. already installed on your clients or you can install your own. But with your own you have to touch these devices.
Wolfgang.
Hi all,
If i have a *.mycompany.com.au certificate issued by Digicert, can i use this certificate as wouldn't the public users trusted the cert issued by a CA like Digicert?
Cheers,
Hunt
Hunt,
I very much apologize for misunderstanding my writing. Yes, the guys here are really right, you can't by such SUB-CA.
I have one customer they did this, but they are the owner of one of these Root-CAs.
As @PhoneBoy and @Maarten_Sjouw mentioned you have to follow their suggestions and implement your owned Sub-CA.
Wolfgang
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 10 | |
| 9 | |
| 7 | |
| 6 | |
| 6 | |
| 6 | |
| 4 | |
| 3 | |
| 3 | |
| 3 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaThu 26 Nov 2026 @ 10:00 AM (CET)
The Cloud Architects Series: Cloud Security State in 2026 – Lessons Learned and a Look AheadWed 02 Dec 2026 @ 02:00 PM (CET)
E-Mail-Agent-Hijacking: E-Mail-Sicherheit im Zeitalter der KI neu überdenkenWed 02 Dec 2026 @ 02:00 PM (GMT)
Why Email Agent Hijacking Marks the End of Post-Delivery Email SecurityWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 02:00 PM (CET)
E-Mail-Agent-Hijacking: E-Mail-Sicherheit im Zeitalter der KI neu überdenkenWed 02 Dec 2026 @ 02:00 PM (GMT)
Why Email Agent Hijacking Marks the End of Post-Delivery Email SecurityWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseWed 02 Dec 2026 @ 11:00 AM (PST)
Why Email Agent Hijacking Marks the End of Post-Delivery Email SecurityAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION