- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Identity and Trust?
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hello,
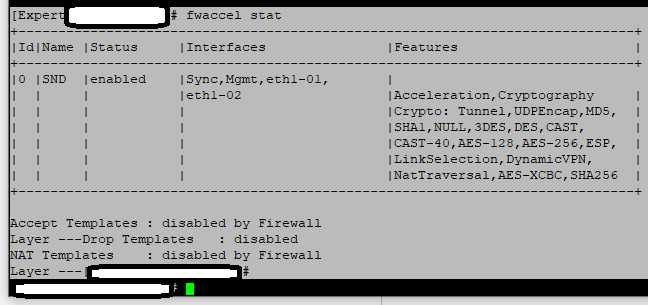
Is there are alternative way to identify exactly what is causing Accept Templates to be disabled. The output from the "fwaccel stat" has a output display issue and does not show me the information.
fwaccel stat
All I can see is "Layer ---", there is a missing carriage return and then "Drop Templates".
Many thanks,
Michael
Strange, it looks like fwaccel stat is not displaying its output correctly. Please provide the output of fwaccel templates -s and fwaccel templates -S, as I suspect Accept templating is actually working.
Ah here we go, your policy layer name must be longer than 32 characters. Shorten it and the fwaccel stat output will start working correctly:
Which version do you use ? Afaik, this is the only way to display these layers. Even looks like an issue for TAC to me...
Is the firewall being managed by MDSM/Provider-1, and if so are there global rules being inserted at the top of the policy? Also please provide the output of enabled_blades.
Hello,
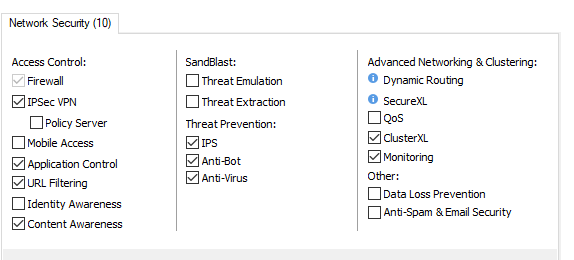
The cluster is not managed as part of a MDM environment, so there are not global rules. the following blades are activated:
Blades
Regards,
Michael
Try temporarily disabling Anti-bot, reinstall policy, then check Accept templating status again.
Are you using any of those in the policy: dhcp-request' / 'dhcp-reply' / 'dhcpv6-request' / 'dhcpv6-reply' / 'dhcpv6-relay?
If yes, look here: https://supportcenter.checkpoint.com/supportcenter/portal?eventSubmit_doGoviewsolutiondetails=&solut...
Strange, it looks like fwaccel stat is not displaying its output correctly. Please provide the output of fwaccel templates -s and fwaccel templates -S, as I suspect Accept templating is actually working.
Ah here we go, your policy layer name must be longer than 32 characters. Shorten it and the fwaccel stat output will start working correctly:
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 10 | |
| 9 | |
| 8 | |
| 7 | |
| 7 | |
| 6 | |
| 4 | |
| 4 | |
| 3 | |
| 3 |
Thu 12 Nov 2026 @ 11:00 AM (EST)
Tips and Tricks 2026 #15: Check Point MDR and Incident ResponseTue 17 Nov 2026 @ 08:30 AM (EST)
Bogota Breakfast & Hack: IA bajo control y ataques en vivo con Workspace SecurityTue 17 Nov 2026 @ 05:00 PM (CET)
AI Security Masters: Security in the Pace of AI: From Threat to Force MultiplierTue 17 Nov 2026 @ 11:00 AM (EST)
Under the Hood: Check Point SASE | Troubleshooting Like a ProThu 12 Nov 2026 @ 11:00 AM (EST)
Tips and Tricks 2026 #15: Check Point MDR and Incident ResponseTue 17 Nov 2026 @ 05:00 PM (CET)
AI Security Masters: Security in the Pace of AI: From Threat to Force MultiplierTue 17 Nov 2026 @ 11:00 AM (EST)
Under the Hood: Check Point SASE | Troubleshooting Like a ProTue 17 Nov 2026 @ 08:30 AM (EST)
Bogota Breakfast & Hack: IA bajo control y ataques en vivo con Workspace SecurityAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION