- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Agentic Network Orchestration
21 October @ 5pm CET / 11am EDT
AI Security Masters
LGTM: Bypassing an LLM Build Gate
When Prompt Injection Fails
Scaling Check Point Automation with Arodonata
CheckMates Go:
Fun Ding
Hey guys,
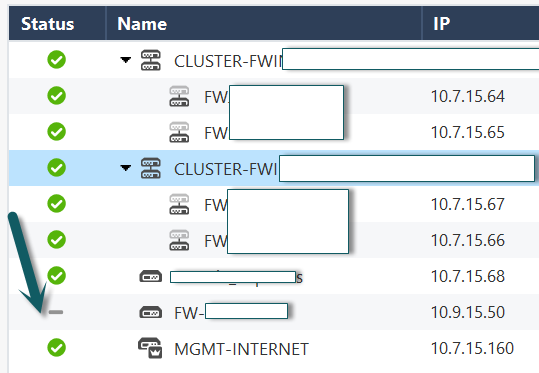
I know there were posts about this before and could be cosmetic, but not sure if there is an easy fox for it or not. There is new gateway we connected for the customer and status shows as "-" in smart console, while all else is green, its all on R81.10 jumbo 66.
Tried rebooting gateway, management, updated contracts file, verified licenses with TAC, so waiting for them to provide next steps.
Anyone have an idea why this would happen? I get its probably cosmetic, but I find it odd that all other gateways show green. License status also shows as "n/a".
Tx as always
Issue fixed by reverting to policy before object was created and then creating the object with exact same name.
sk112058 ?
no joy
sk164013 - easy to try...
did that last night, no luck
SIC is working ?
yes sir and policy too
Running commands on GW in Dashboard works ?
yes sir, no issues, in dashboard or ssh, works fine 100%
I see the same issue. Do you have management in HA ? In my case, the active management showed no status, while the standby (connected only as Read Only) showed all green ! I tried to switch active domain to be standby and standby to be active and that did the trick. After management failover all is looking good. It is just a cosmetic issue, but yeah, strange...
oh, and forgot to mention that this "no status" is seen only on gateways which were created AFTER the upgrade to R81.10.
This is very likely cosmetic.
May require a TAC case to get to the bottom of.
Issue fixed by reverting to policy before object was created and then creating the object with exact same name.
Bro,
I have exactly the same problem.
The new equipment is already in production, and has "hooked" its policy package.
Is it feasible to delete the FW-Ch object from the SmartConsole, without affecting the services of this equipment ????
When you delete the object you have to send to install policies?
Greetings.
Once you delete the object, you have to recreate it and install the policy again.
Andy
Hmm - does that mean you had kept firewall hostname and objects created with hostname in dashboard were different?
In our case, we gave it exact same hostname.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 23 | |
| 12 | |
| 12 | |
| 6 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 3 |
Fri 09 Oct 2026 @ 10:00 AM (CEST)
CheckMates Live Netherlands - Sessie 49: Maak kennis met Check Point R82.20Tue 13 Oct 2026 @ 06:00 PM (IDT)
AI Security Masters: LGTM: Bypassing an LLM Build Gate When Prompt Injection FailsThu 15 Oct 2026 @ 05:00 PM (CEST)
What If Email Security Ran Your Security Awareness Program?Tue 20 Oct 2026 @ 04:00 PM (CEST)
EMEA: Beyond the Basics: Designing Identity Awareness for Large-Scale EnvironmentsFri 09 Oct 2026 @ 10:00 AM (CEST)
CheckMates Live Netherlands - Sessie 49: Maak kennis met Check Point R82.20Thu 15 Oct 2026 @ 05:00 PM (CEST)
What If Email Security Ran Your Security Awareness Program?Tue 20 Oct 2026 @ 04:00 PM (CEST)
EMEA: Beyond the Basics: Designing Identity Awareness for Large-Scale EnvironmentsTue 20 Oct 2026 @ 03:00 PM (EDT)
AMER: Beyond the Basics: Designing Identity Awareness for Large-Scale EnvironmentsThu 29 Oct 2026 @ 11:00 AM (PDT)
Irvine, CA: Secure the Network, the App, and the Workforce: A Hybrid Mesh & SASE BriefingAbout CheckMates
Learn Check Point
Advanced Learning
YOU DESERVE THE BEST SECURITY