

- Products
- Learn
- Local User Groups
- Partners
- More

Scaling Check Point Automation with Arodonata
7 October @ 5pm CET / 11am EDT
What's New in Check Point SASE
The State of Ransomware Q2 2026:
This Quarter's Trends, and Their Impact on Your Defenses
AI Security Masters
Implementing the AI Security Trifecta
CheckMates Go:
Half is Not Enough
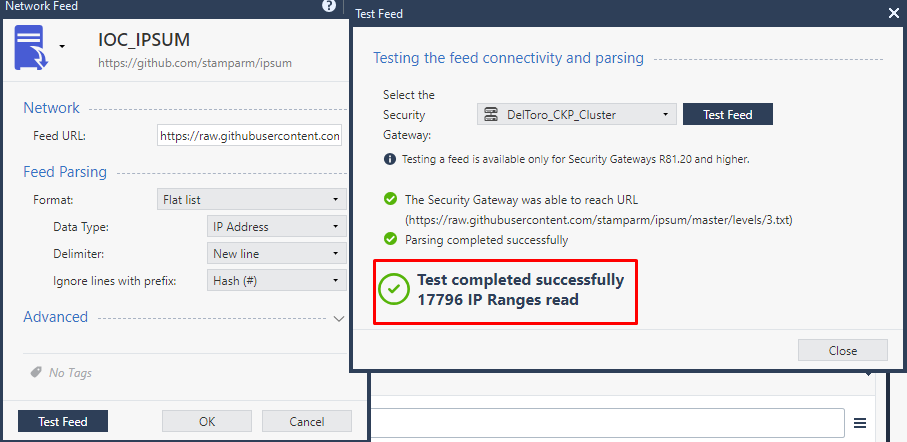
Hello mates, I usually use the following open source project:
https://github.com/stamparm/ipsum
It sumarice malicious IP between different lists. It create lists based on the ocurrence of the IP and categorice en levels.
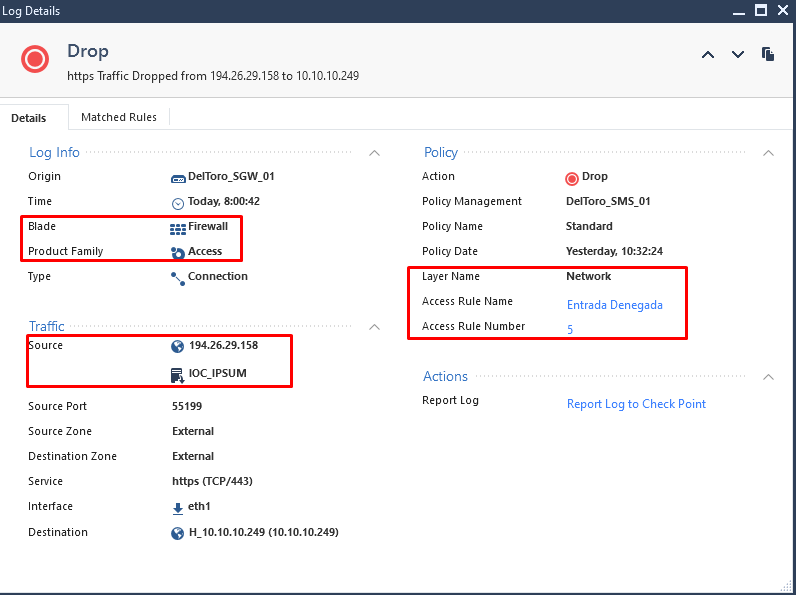
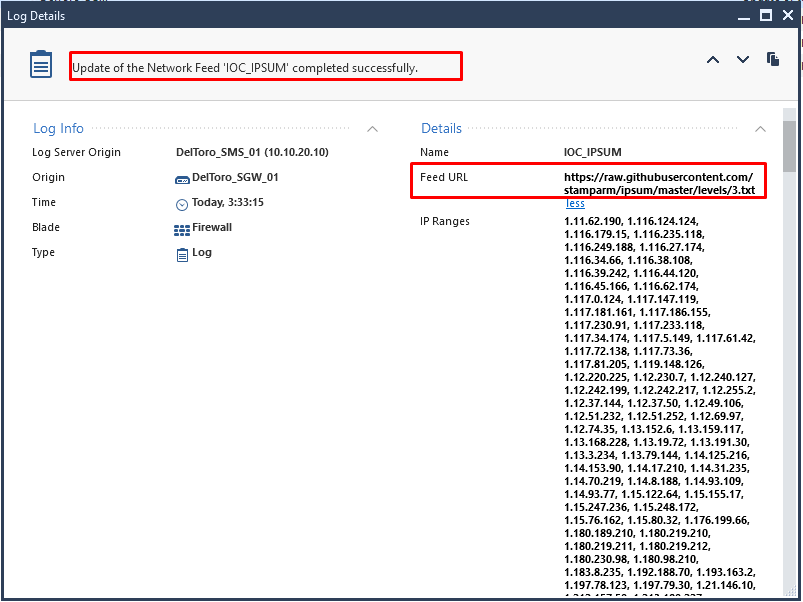
I have configured this IOC in my lab and it's working fine. The level 3 list has over 17K malicious IPs. From R81.20, the way of using network feeds in the access control policy, for me it is more granular.

Best regards! 😉
About CheckMates
Learn Check Point
Advanced Learning

YOU DESERVE THE BEST SECURITY


