- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Good afternoon, I would like to know if it is possible to check the status of a vpn. For example, I would like to be checking how many times in a month a site-to-site tunnel was down. To be able to make a report.
In the logs it is possible to see the errors, but it is almost impossible to look at all the logs for this period of time that I need to analyze.
Can someone help me?
Problem is the SA lifetimes dictate how long a tunnel is allowed to be up before being torn down to change keys, so just looking at key exchange messages does not mean an outage actually occurred. In addition most VPNs are brought up on demand when interesting traffic needs to use them, and if there is no traffic the tunnel can time out and appear "down" until some more interesting traffic arrives.
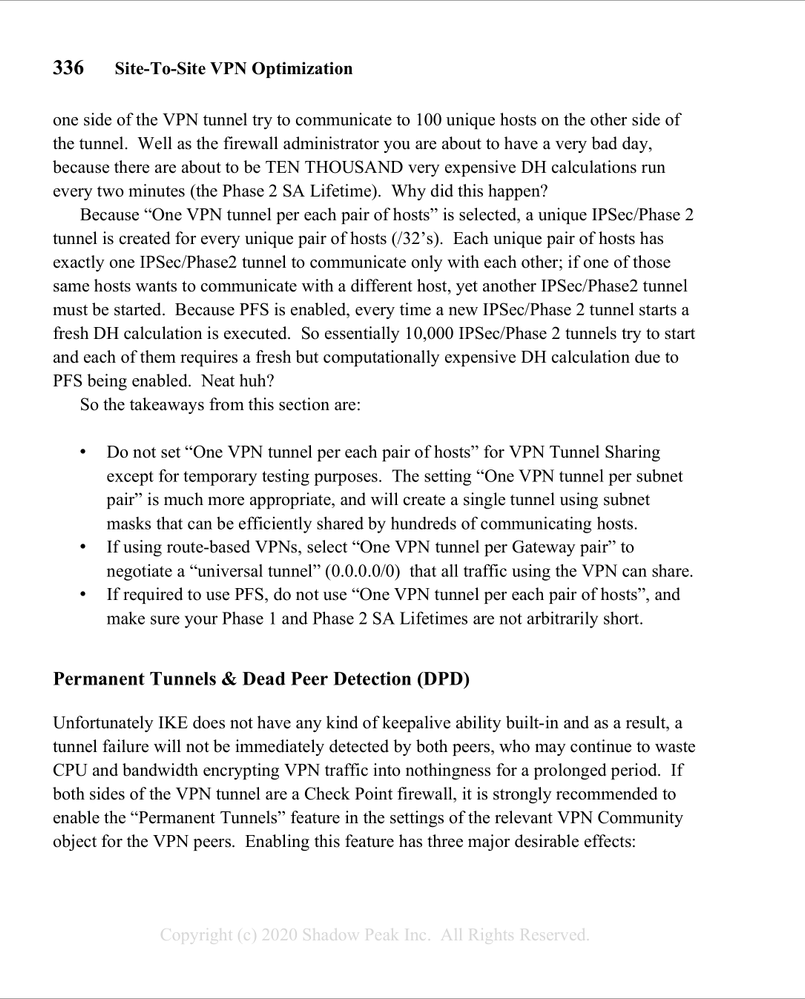
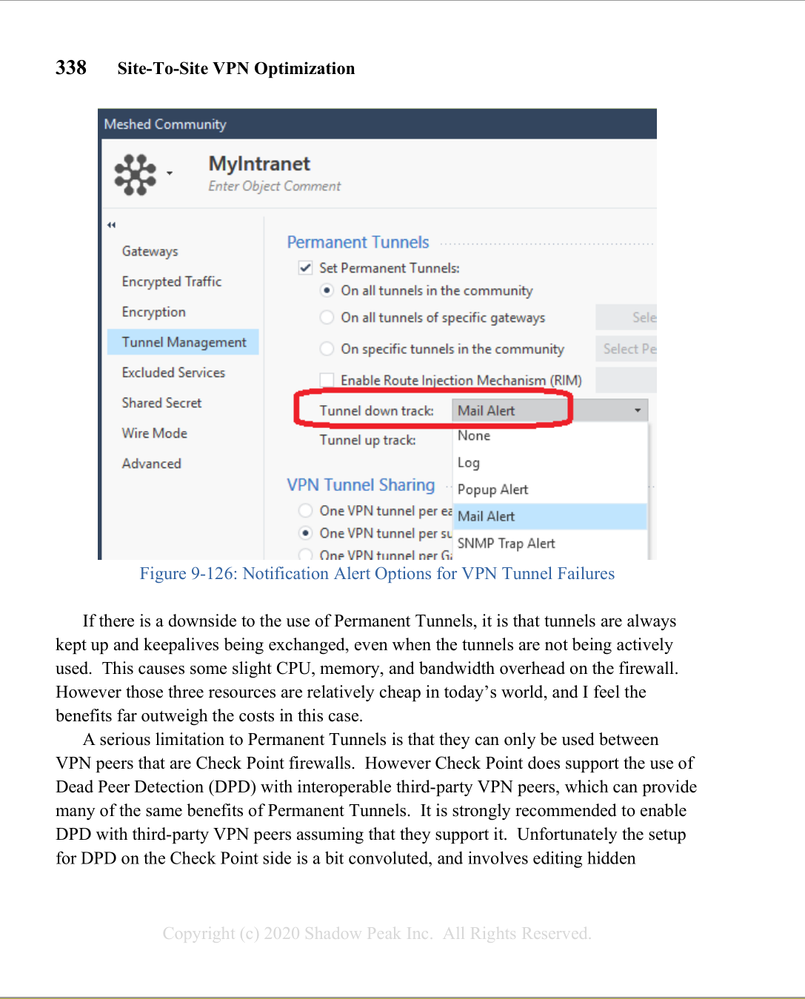
Only way I can think of to do this is via Permanent Tunnels which by default only work between Check Point gateways, but can be made to work with other vendor's firewalls by setting Dead Peer Detection (DPD) mode. Assuming you set both "tunnel up" and "tunnel down" alerts you could measure the time between tunnel down and tunnel up alerts to determine total outage time, although it can take between 20-30 seconds to detect that a tunnel has fallen down and cannot get back up. The default lifesign interval is 10 seconds with 3 failures causing a "tunnel down" condition, but these timers could be shortened I suppose. Here is the coverage for Permanent Tunnels from my book:
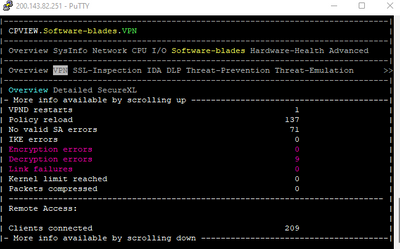
Thanks for your response. Let me go into more detail about my case. My client is experiencing connectivity issues on their VPN. In this case, I wanted to be able to tell you which of these errors are happening in a report. But because it's an SMB I don't have access to errors via CPView.
Of course it is possible to see in the logs when a tennel or a link is down, but because it is a lot of logs as it has already been clear. I wanted to know if there is a more practical way to check these errors, as well as in CPView.
Thanks for listening.
On SMB options are missing to Monitor VPN status, so all you can do is ping thru the GW from a internal client and record that...
In fact, what I need is to collect evidence of how many times the tunnel was unavailable within 30 days.
We had some unavailability and a client asked me how many times it was unavailable and what caused this unavailability.
Could you give me any ideas on how to put together a report on this or how to gather this evidence?
thanks.
Agree with Gunter here, your best option on SMB is some kind of third-party monitoring system that continuously sends traffic through the VPN tunnel every so often and records the availability statistics you need.
thank you very much for everyone's attention
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 3 | |
| 3 | |
| 3 | |
| 2 | |
| 1 | |
| 1 | |
| 1 | |
| 1 | |
| 1 | |
| 1 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION