- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hello, Everyone!
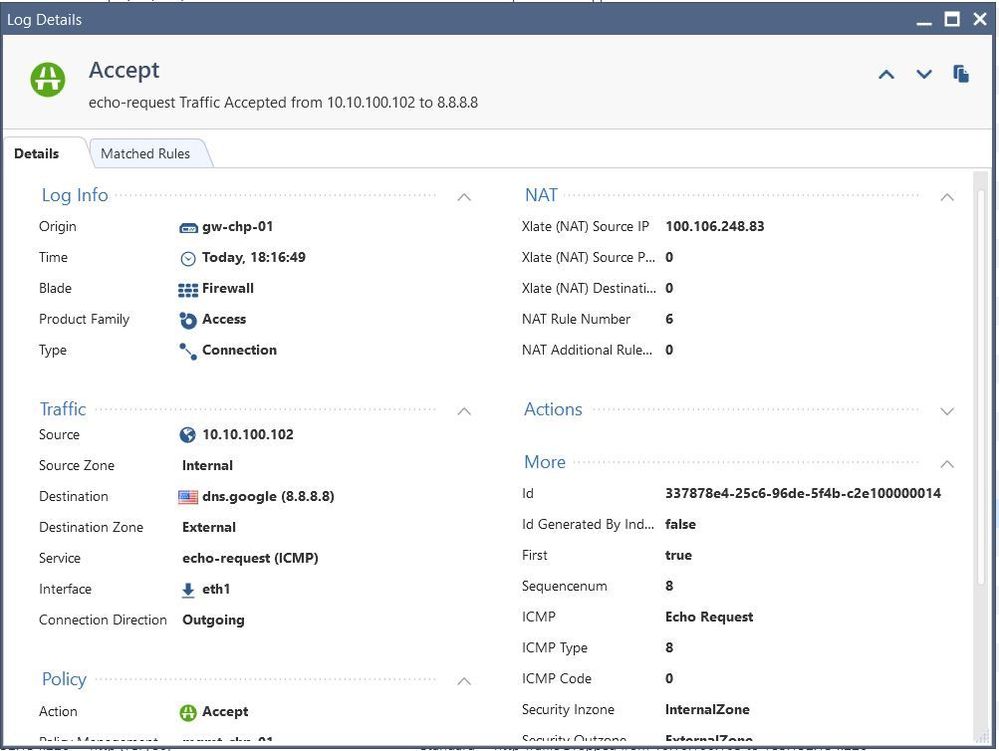
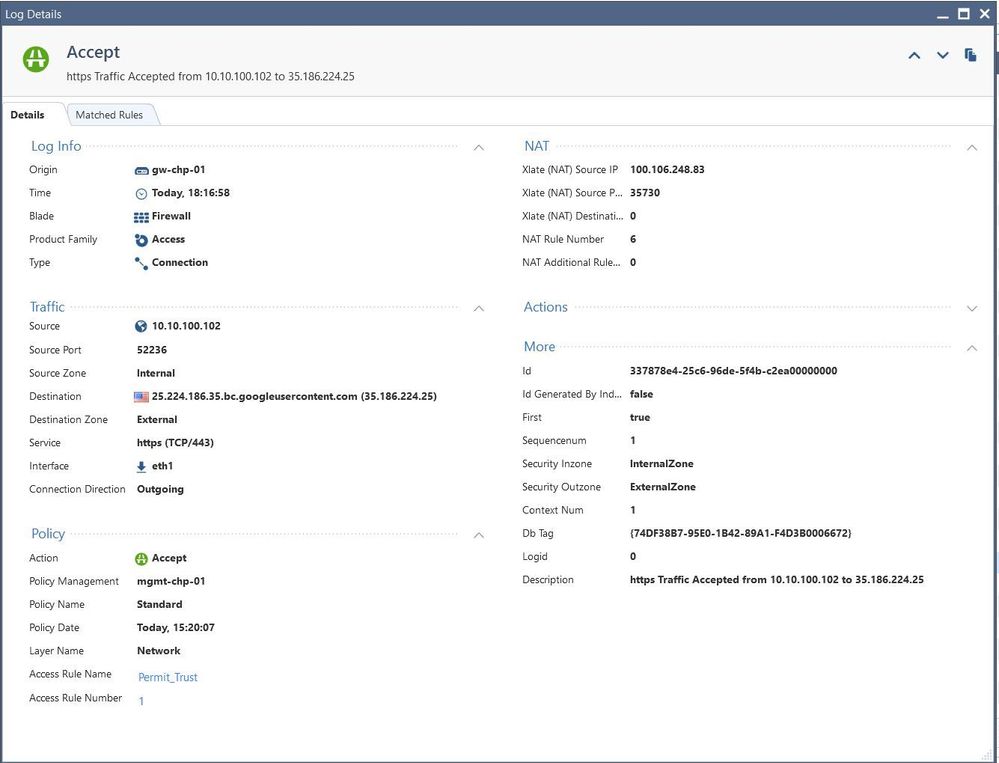
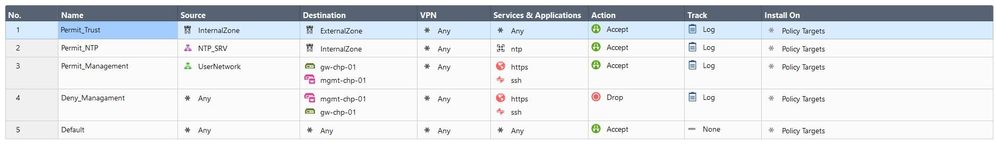
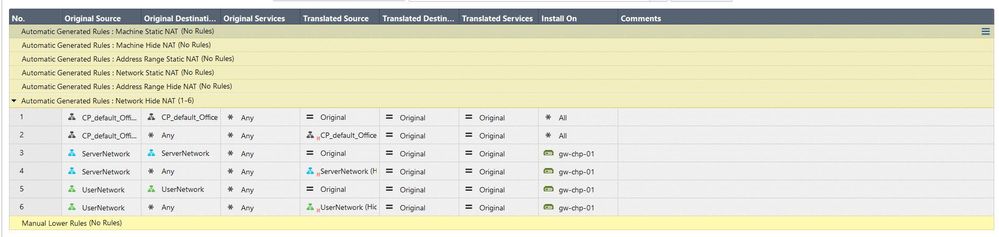
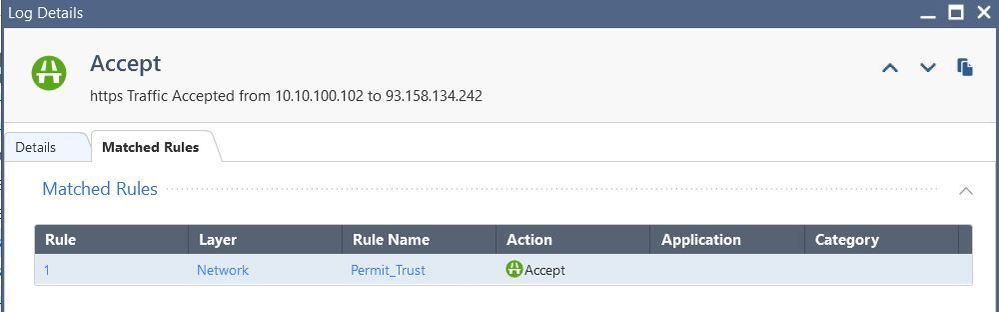
I have an issue with Check Point Security Gateway R80.10. Clients cannot access Internet resources (for example http/https web-pages), though they can ping External IPs and DNS (8.8.8.8 and google.com). I have default access policy as accept all, threat prevention policy is disabled, Automatic NAT. Looking for help to resolve this issue. For http/https traffic log shows accept, check screenshots below, thanks in advance.
If ping works but nothing else, it usually means other traffic is being denied by your APCL/URLF layer. Ping is not an application (and need only match a rule in the Network/Firewall policy layer) but practically everything else including DNS is. Click the Matched Rules tab on your log card.
Beyond that run fw ctl zdebug drop and try to pass some traffic. If you don't see a drop in that output it is a routing (or possibly NAT) issue of some kind.
If ping works but nothing else, it usually means other traffic is being denied by your APCL/URLF layer. Ping is not an application (and need only match a rule in the Network/Firewall policy layer) but practically everything else including DNS is. Click the Matched Rules tab on your log card.
Beyond that run fw ctl zdebug drop and try to pass some traffic. If you don't see a drop in that output it is a routing (or possibly NAT) issue of some kind.
Or a little bit more important they cannot do DNS... try to ping www.google.com and see if it resolves.
Thanks for Reply.
As I mentioned earlier, icmp available by IP and DNS, so this is not a problem.
Thanks for Reply, Timothy
I issued command fw ctl zdebug drop and there drops fom one address subnet I don't have:
;[cpu_3];[fw4_0];fw_log_drop_ex: Packet proto=6 178.34.109.191:10400 -> 173.194.73.95:443 dropped by cphwd_offload_connkey Reason: VPN and/or NAT traffic between accelerated and non-accelerated interfaces or between non-accelerated interfaces is not allowed;
;[cpu_3];[fw4_0];fw_log_drop_ex: Packet proto=6 178.34.109.191:10401 -> 108.177.14.101:443 dropped by cphwd_offload_connkey Reason: VPN and/or NAT traffic between accelerated and non-accelerated interfaces or between non-accelerated interfaces is not allowed;
;[cpu_3];[fw4_0];fw_log_drop_ex: Packet proto=6 178.34.109.191:10399 -> 162.159.129.233:443 dropped by cphwd_offload_connkey Reason: VPN and/or NAT traffic between accelerated and non-accelerated interfaces or between non-accelerated interfaces is not allowed;
;[cpu_3];[fw4_0];fw_log_drop_ex: Packet proto=6 178.34.109.191:10400 -> 173.194.73.95:443 dropped by cphwd_offload_connkey Reason: VPN and/or NAT traffic between accelerated and non-accelerated interfaces or between non-accelerated interfaces is not allowed;
;[cpu_3];[fw4_0];fw_log_drop_ex: Packet proto=6 178.34.109.191:10402 -> 35.186.224.47:443 dropped by cphwd_offload_connkey Reason: VPN and/or NAT traffic between accelerated and non-accelerated interfaces or between non-accelerated interfaces is not allowed;
;[cpu_3];[fw4_0];fw_log_drop_ex: Packet proto=6 178.34.109.191:10396 -> 173.194.73.95:443 dropped by cphwd_offload_connkey Reason: VPN and/or NAT traffic between accelerated and non-accelerated interfaces or between non-accelerated interfaces is not allowed;
Defaulting all kernel debugging options
Here tab matched rules
Okay, I found solution. I have PPPoE and Checkpoint has something called SecureXL wich is in conflict, I disabled and everything is working now.
In R80.20+, disabling SecureXL isn’t required.
More specifically, SecureXL will automatically not accelerate PPPoE interfaces without requiring you to disable SecureXL entirely.
In fact, you cannot completely disable SXL in R80.20+ anymore
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 7 | |
| 7 | |
| 6 | |
| 6 | |
| 4 | |
| 3 | |
| 3 | |
| 3 | |
| 3 | |
| 3 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaThu 26 Nov 2026 @ 10:00 AM (CET)
The Cloud Architects Series: Cloud Security State in 2026 – Lessons Learned and a Look AheadWed 02 Dec 2026 @ 02:00 PM (CET)
E-Mail-Agent-Hijacking: E-Mail-Sicherheit im Zeitalter der KI neu überdenkenWed 02 Dec 2026 @ 02:00 PM (GMT)
Why Email Agent Hijacking Marks the End of Post-Delivery Email SecurityWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 02:00 PM (CET)
E-Mail-Agent-Hijacking: E-Mail-Sicherheit im Zeitalter der KI neu überdenkenWed 02 Dec 2026 @ 02:00 PM (GMT)
Why Email Agent Hijacking Marks the End of Post-Delivery Email SecurityWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseWed 02 Dec 2026 @ 11:00 AM (PST)
Why Email Agent Hijacking Marks the End of Post-Delivery Email SecurityAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION