- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Agentic Network Orchestration
21 October @ 5pm CET / 11am EDT
AI Security Masters
LGTM: Bypassing an LLM Build Gate
When Prompt Injection Fails
Scaling Check Point Automation with Arodonata
CheckMates Go:
Fun Ding
I'm trying to block Psiphon 3
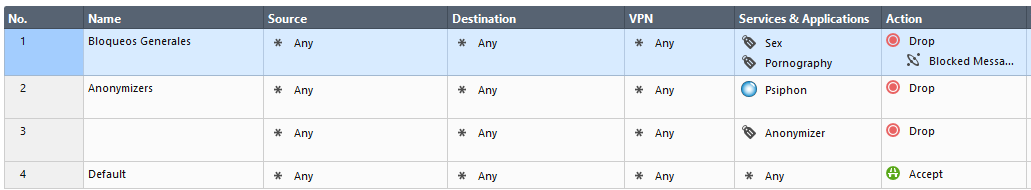
I have blocked the single application, the category: anonymizers.

I have enabled the HTTPS Inspection for all the categories

The logs shows Psiphon is blocked but it's still working
Has anyone successfully blocked Psiphon 3 ???
Psiphon, like many anonymizes, evolves specifically to avoid detection.
As a result, from time to time, the application signature needs to be updated.
I recommended engaging with the TAC and providing some packet captures so we can take a look.
I really did block Psiphon3 with this configuration:
a) Enable HTTP Inspection in all categories
b) Block categories: Anonymizers, Unknown traffic
c) Block SSH in Firewall Layer (I had to allow ssh to my specific destinations)
The problem is: A few applications are not identified by Check Point, so they are blocked beacuse of the "unknown traffic" category drop
Hi Ricardo,
Full HTTPS inspection and blocking SSH protocol is indeed crucial for successful blocking of the Psiphon client.
Did you try to enforcing it without blocking 'Unknown Traffic' and failed to do so?
As Dameon stated above you may contact us via TAC and send us captures of the specific unblocked traffic, in the meanwhile we'll work on trying to reproduce the issue in our lab as well.
In case you are interested in adding new detection for apps which are currently not detected ("Unknown Traffic") you may submit a request via the following form and request a new application:
Thanks,
Idan
Hi Idan,
I did try without blocking "unknown traffic" category, but Psiphon is not blocked. So, in my case it was necessary.
still i have same problem. 1 year continue working with TAC. but they didnot solve my problem. Psiphon very fast getting new updates.
You are correct Psiphon is quickly getting new updates, therefore the best way is to find the culprit. alert when there is a multiple ssh connection from same source. Fortunately, I have SIEM to do that.
I am also facing same issue, though i have blocked open SSH & unknown traffic also.
Finally able to block the psiphon with the help of tac.
The procedure is :
-install the latest hotfix in both gateway and management (may or may not be required)
- Enable https inspection and generate the self sign certificate.
- generate self-signed certificate and install it on all PC of the network (Would be easy if Active Directory is in use)
- Make a Policy for https inspection with "https" and "http_and_https_proxy" with ACtion=Inspection
- Add url and application policy to block the category "support file sharing".
Note: the psiphon is block for only devices in which we install the self-sign certificate.
Thanks,
Sagar Manandhar
Does not work without HTTPS Inspection?? What happens on BYOD scenarios??
I have a customer with a WiFi deployment for Students where each one has his own tablet to access shared resources and for Internet Access, according to policy all Media Sharing and Media Streams are blocked, but still bypassed with Psiphon because I can't deploy a certificate for those devices.
Any ideas of a workaround?
Regards.
Like I said previously:
Psiphon, like many anonymizes, evolves specifically to avoid detection.
As a result, from time to time, the application signature needs to be updated.
I recommended engaging with the TAC and providing some packet captures so we can take a look.
Contact Support | Check Point Software
Obviously HTTPS Inspection is not always possible but is also effective as well.
Want to provide some update on this as the latest version of Psiphon has been updated to support QUIC.
In order to effectively block Psiphon, the following is needed:
But if we block QUIC protocol, will it impact any google services traffic i.e. google search, google mail, YouTube etc.
I have not encountered any Google Service that also isn't available over traditional HTTP/HTTPS.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 52 | |
| 20 | |
| 19 | |
| 12 | |
| 10 | |
| 8 | |
| 8 | |
| 6 | |
| 6 | |
| 5 |
Fri 09 Oct 2026 @ 10:00 AM (CEST)
CheckMates Live Netherlands - Sessie 49: Maak kennis met Check Point R82.20Tue 13 Oct 2026 @ 06:00 PM (IDT)
AI Security Masters: LGTM: Bypassing an LLM Build Gate When Prompt Injection FailsThu 15 Oct 2026 @ 05:00 PM (CEST)
What If Email Security Ran Your Security Awareness Program?Fri 09 Oct 2026 @ 10:00 AM (CEST)
CheckMates Live Netherlands - Sessie 49: Maak kennis met Check Point R82.20Thu 15 Oct 2026 @ 05:00 PM (CEST)
What If Email Security Ran Your Security Awareness Program?Tue 20 Oct 2026 @ 04:00 PM (CEST)
EMEA: Beyond the Basics: Designing Identity Awareness for Large-Scale EnvironmentsTue 20 Oct 2026 @ 03:00 PM (EDT)
AMER: Beyond the Basics: Designing Identity Awareness for Large-Scale EnvironmentsThu 29 Oct 2026 @ 11:00 AM (PDT)
Irvine, CA: Secure the Network, the App, and the Workforce: A Hybrid Mesh & SASE BriefingAbout CheckMates
Learn Check Point
Advanced Learning
YOU DESERVE THE BEST SECURITY