- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Agentic Network Orchestration
21 October @ 5pm CET / 11am EDT
AI Security Masters
LGTM: Bypassing an LLM Build Gate
When Prompt Injection Fails
Scaling Check Point Automation with Arodonata
CheckMates Go:
Fun Ding
Hi CP,
Regrading to Threat Prevention log if we not see a few days it's cause from Policy or anything ?
Could be several things probably best reviewed via a remote session rather than guessing.
With that said are you still receiving normal firewall logs from the same Gateways or no?
We got the firewall logs as normal on the same gateway. And just last few days that we did not get threat prevention logs.
Which JHF take is applied to this environment and are the relevant Threat Prevention blades still enabled on the gateway object?
Additionally would anyone have configured fast_accel rules recently?
Again, probably best to contact TAC to review via a remote session.
Threat prevention blades are still enable on the gateway object and as I mention we did not change anything on on that.
Again please provide all the requested info as follows:
- Which Jumbo/JHF version is installed on-top of R81.10?
- Output of command: fw stat -b AMW
- Run CheckME and review logs
If you don't wish to do so here for whatever reason then please consult further with TAC via a remote session to diagnose the problem more efficiently.
May I ask you, Normally threat prevention logs are always detect right?
No they will typically be either Detect or Prevent depending on your configuration/policy and the type of threat encountered.
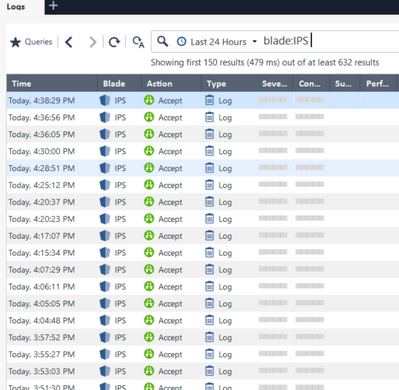
Please review your smartlog filters...
Yes, I concern because it's just last week that I can not see the logs detection and prevention. That I think it may any issue.
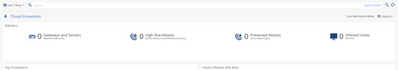
There isn't sufficient information available here to say apart from the obvious categories
Please expand the IPS log card if you need further insight
Might just be that the gateway is not sending logs:
Or some configuration issue.
Did you see TP logs before?
Do you see firewall logs?
Might be that the rule is set not to track?
Can you check the Threat Prevention Policy is installed properly?
Please share the output of fw stat -b AMW on the Security Gateway
We did not change anything on threat prevention policy. And just last few days did not get threat prevention logs.
Please provide output of fw stat -b AMW run on the gateway as requested earlier in the thread.
http://www.cpcheckme.com will light up your Threat Prevention logs and tell you if it is working correctly.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 23 | |
| 12 | |
| 12 | |
| 6 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 3 |
Fri 09 Oct 2026 @ 10:00 AM (CEST)
CheckMates Live Netherlands - Sessie 49: Maak kennis met Check Point R82.20Tue 13 Oct 2026 @ 06:00 PM (IDT)
AI Security Masters: LGTM: Bypassing an LLM Build Gate When Prompt Injection FailsThu 15 Oct 2026 @ 05:00 PM (CEST)
What If Email Security Ran Your Security Awareness Program?Tue 20 Oct 2026 @ 04:00 PM (CEST)
EMEA: Beyond the Basics: Designing Identity Awareness for Large-Scale EnvironmentsFri 09 Oct 2026 @ 10:00 AM (CEST)
CheckMates Live Netherlands - Sessie 49: Maak kennis met Check Point R82.20Thu 15 Oct 2026 @ 05:00 PM (CEST)
What If Email Security Ran Your Security Awareness Program?Tue 20 Oct 2026 @ 04:00 PM (CEST)
EMEA: Beyond the Basics: Designing Identity Awareness for Large-Scale EnvironmentsTue 20 Oct 2026 @ 03:00 PM (EDT)
AMER: Beyond the Basics: Designing Identity Awareness for Large-Scale EnvironmentsThu 29 Oct 2026 @ 11:00 AM (PDT)
Irvine, CA: Secure the Network, the App, and the Workforce: A Hybrid Mesh & SASE BriefingAbout CheckMates
Learn Check Point
Advanced Learning
YOU DESERVE THE BEST SECURITY