- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hi Folks,
I'm fairly new to checkpoint and have got a request to allow the SIP traffic UDP/5060, TCP/5060 and TCP/5061. Firewalls running R81.10 and Take78.
Have gone through this article and it suggests opening the data port manually along with sip_tls_not_inspected (if sip_tls_authentication can't be used)
SIP-Specific services (checkpoint.com)
I'd like to seek your help in understanding how checkpoint processes the SIP traffic as couple of posts suggest using without the protocol handler and exempt from the IPS inspection to avoid one-way call issue.
Is it mandatory to bypass the SIP traffic from both IPS and Inspection settings?
Will the checkpoint not automatically allow the dynamic connections?
If the protocol handler isn’t set, obviously the inspection will not do. If that’s the case, why do we need to config the IPS and inspection settings bypass the SIP traffic?
Whenever possible, use the pre-defined Services including protocol handler to be safe and sure by includong SIP in IPS and TP inspection. See also sk95369: ATRG: VoIP
Those are indeed all very good questions! I recall even in old days of CP, it was tricky to make this work properly, you always had to make either IPS exceptions or change service protocol "mode". I would definitely follow link @G_W_Albrecht provided and if you get stuck, open TAC case and get it fixed.
Thanks for the reply. Can you please help me on this as I'm unable to figure this out based on the resources available.
If the protocol handler isn’t set, obviously the inspection will not do. If that’s the case, why do we need to config the IPS and inspection settings bypass the SIP traffic?
The way I would approach this in the past was always run zdebug if issue was there. So say, just making this up, you have problem with ip 1.2.3.4 and port 5060, you can do something like this from expert mode -> fw ctl zdebug + drop | grep 1.2.3.4 | grep ":5060"
That will most likely tell you where issue might be coming from. By the way, you do NOT need to config anything in IPS to bypass this, UNLESS there is clear proof that IPS is dropping it.
Makes sense?
Hi @the_rock
Thanks mate.
Final one, when you refer to "do NOT need to config anything in IPS to bypass this, UNLESS there is clear proof that IPS is dropping it"
Shall I assume that you're suggesting using the pre-defined services (with protocol handler)?
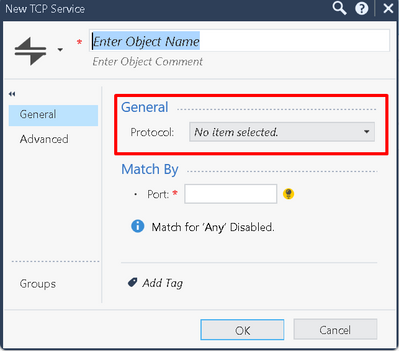
Yes sir, good guess ; - ). technically, if you did below, it would bypass IPS.
The best and most secure is using the pre-defined services (with protocol handler) - any bypass shall only be made if suggested by TAC!
Yes sir Gunther, very good point indeed!!
Andy
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 30 | |
| 8 | |
| 7 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 3 | |
| 3 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION