- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hello,
I recently stood up a standalone R80.40 gateway in a lab environment to perform some testing for policy changes to support Office 365. I'm working through a scenario with a customer who has HTTPS inspection enabled globally, but I'm unable to get inspection working on my lab gateway. I've enabled HTTPS Inspection on the Gateway, have verified the HTTPS Inspection Policy is what I want, and have adjusted the Topology so respective interfaces are configured appropriately.
There's not much to configure here, so I'm beating my head against a wall trying to figure out why this appliance isn't inspecting outbound HTTPS traffic. Any help would be appreciated!
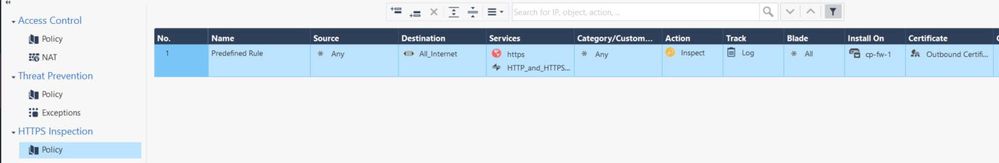
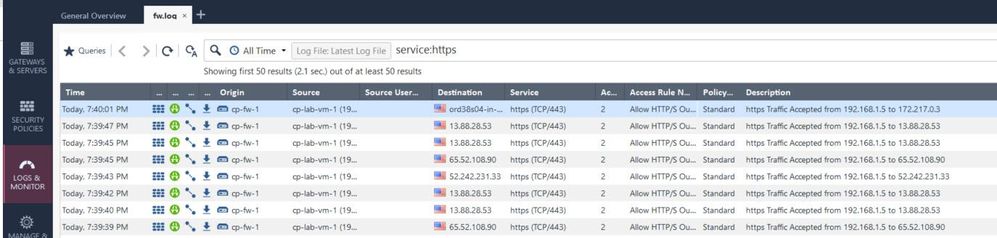
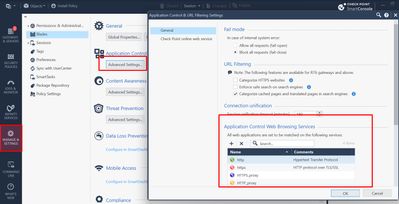
Here are a few screenshots of the configuration and I've followed the guide here when putting this in place.
Hi @DarrenR
A few more tips:
1) Did you import the outbound certificate correctly in the browser?
2) Are there log entries for https inspection? If so, please take a picture.
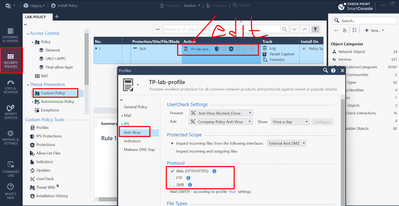
3) Is the https interception enabled in the protocol tab?
4) Set "Internet" instead of "all internet" in the destination:
Boom! I missed the enabling the protocol signature. Thanks!
Are you referring to the protocol setting in the Threat Prevention Profile editor?
Trying to extrapolate from the small screenshot, it looks like the setting that exists for the various Threat Prevention engines.
Indeed, it's possible to specify which protocols will be included in the scanning, but the default value for these profiles is to be "On" for HTTP/HTTPS. Most customers should not encounter this issue or have to touch this setting for HTTPS inspection to work.
Did you deactivate this in the past for your environment?
I'd like to better understand this case to make sure more customers don't encounter it.
Thanks!
Can you tell me where the config is in your step 3 ? Because i couldn't find it. Thank you.
Can somebody tell me, where can I find the protocol tab and setup the protocol signature feature? Is this a must config to work with HTTPS Inspection?
So without this feature the inspection not working? Thanks!
can't find it either. does it still exist in R81?
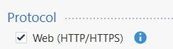
Where do you find that "Protocol" option with the checkbox for "Web (HTTP/HTTPS)"?
Thank you. This I knew for Threat Prevention. I was wondering if there was another similar configuration available under HTTPS shared policies > inspection settings.
Only one I know is this
Andy
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 30 | |
| 8 | |
| 7 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 3 | |
| 3 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaThu 26 Nov 2026 @ 10:00 AM (CET)
The Cloud Architects Series: Cloud Security State in 2026 – Lessons Learned and a Look AheadWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION