- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Identity and Trust?
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hello everyone,
Currently, I'm introducing the Checkpoint FW product to a school.
Every feature is relevant until they want to check out Filtering feature:
- They are using the following website for testing: http://testfiltering.com/
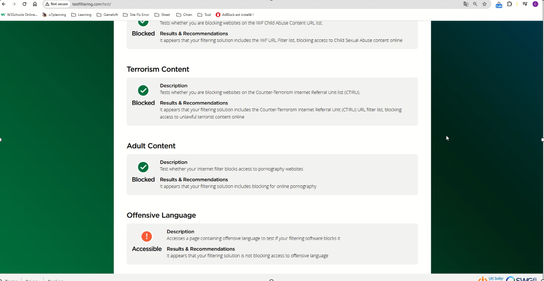
- I have implemented relevant categories, http/https inspection,..., however when performing "run test", the test results still do not prevent access to Offensive Language.
- I will leave the video with the configuration and perform the test below (video in file .pptx):
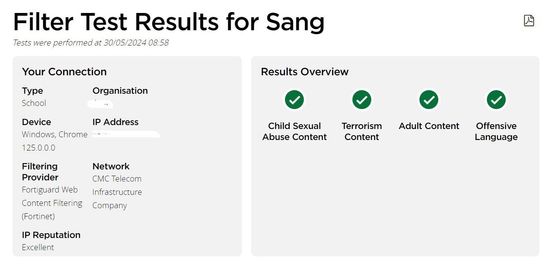
Now competitor Fortinet is also pitching to that school, and they passed the test, pictured below:
If our solution can pass this test, that school will be very likely to buy the solution, because they are more favorable towards Checkpoint than Fortinet.
So please help me, is there any way to configure and pass the test?
Thank you very much, everyone.
Best regards.
What do you configure in the policy to prevent those categories?
Hi _Val_,
You can check configure on the .pptx file attachment.
And what made you think I did not check it before asking a question?
You put there a video of the test. It is virtually impossible to see in the video how you configured your URLF policy.
Hi!
What blades you have enabled to achieve this goal? I assume you want to use URL filtering and application control?
At this moment I am not able to find a URL filtering category related to bad language. Is does also not make sense I think. For example if there is a bad word in a youtube video comment this video then needs to be blocked? Maybe this has education purposes. So I would reconsider to advise against blocking this category.
Also I found the DLP (data leak prevention) blade has an option for blocking bad language. Below screenshots as reference.
Logically, to me anyway, if you can find category that matches offensive language, you can add it to be blocked. I cant recall now what closest one to it would be, but its easy to tell once you hit plus sign to add them. Otherwise, I would confirm with TAC.
Andy
There are plenty, see below
Just logging in now to S1C for one customer, let me see.
Andy
@_Val_ I dont see inappropriate sites by default, I assume you added it yourself? Other ones are there...
Andy
Anyhow, make sure you add these categories to the block rule, and see if it makes any difference.
On top, I hope your HTTPS Inspection is on.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 28 | |
| 9 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 4 | |
| 3 | |
| 3 |
Tue 17 Nov 2026 @ 08:30 AM (EST)
Bogota Breakfast & Hack: IA bajo control y ataques en vivo con Workspace SecurityTue 17 Nov 2026 @ 05:00 PM (CET)
AI Security Masters: Security in the Pace of AI: From Threat to Force MultiplierTue 17 Nov 2026 @ 11:00 AM (EST)
Under the Hood: Check Point SASE | Troubleshooting Like a ProTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaTue 17 Nov 2026 @ 05:00 PM (CET)
AI Security Masters: Security in the Pace of AI: From Threat to Force MultiplierTue 17 Nov 2026 @ 11:00 AM (EST)
Under the Hood: Check Point SASE | Troubleshooting Like a ProTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseTue 17 Nov 2026 @ 08:30 AM (EST)
Bogota Breakfast & Hack: IA bajo control y ataques en vivo con Workspace SecurityAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION