- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hey guys,
Sorry if I posted this in the wrong location. I have an inquiry about content awareness blade. So, the gist of it is this...customer simply wants to block certain people in his network from being able to download any exe files anywhere from the Internet. Now, here is what we tested in my lab.
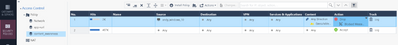
Setup...its all on R81.10 jumbo 61 and windows 10 VM. So, on the gateway (its single fw), I enabled https inspection (works fine), along with content awareness as well. There are 3 ordered layers...network, app/url and content awareness. Now in content awareness blade, we have 2 rules, first one is to block any exe files from my windows 10 machine out to Internet and we also set up block message notification, but never comes up when exe file is blocked. Worse that that, it works very inconsistent, which we also showed to TAC on the call the other day.
Im not sure what is missing here, because all the guides I read, it seems pretty straight forward and rule itself does have 3k hits, so it does work, but as I said, its very inconsistent.
Anyone has any experience with content awareness blade that could help out?
Btw, here is what TAC gave us, but even though this works for google chrome, does not work for other browsers (I can download exe files via mozilla and Edge browsers)
Thanks as always!
Must admit first thing that comes to mind is which browser and is Quic allowed or blocked on the same environment?
When I implemented sk in my windows 10 on chrome, windows and mozilla, exe files ONLY got blocked on google chrome, thats it. Plus, this is not even scalable or acceptable solution or even workaround in my opinion. Say you had company with 10K employees and you want to block 2000 of them downloading exe files off the Internet...there is no way 2000 people would do this process manually : - )
By the way, just tested in my windows lab behind gw on google chrome 4 times and exe download worked every single time just fine.
If you want consistent action for content awareness based on file type, use HTTP/HTTPS in the Services of the rules.
Do not use UserCheck in the same rule unless you are also using UserCheck client on the endpoints: you'll see redirects in the logs instead of the Blocked page. You've seen this before in my old thread:)
https://community.checkpoint.com/t5/Management/Content-Awareness-things-that-do-not-work/m-p/139442
Interesting, thank you @Vladimir . I will try that now and update you.
I think that may had been it, will ask customer to test! Tx a lot Vladimir.
You are quite w:)lcome
K, so that exact lab setup I had did not work for customer, so we left rule as src -any dst-Internet and services http/https/ block exe files, so they will monitor and let me know next week.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 30 | |
| 8 | |
| 7 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 3 | |
| 3 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION