- Products
- Learn
- Local User Groups
- Partners
- More

Scaling Check Point Automation with Arodonata
7 October @ 5pm CET / 11am EDT
AI Security Masters
LGTM: Bypassing an LLM Build Gate
When Prompt Injection Fails
What's New in Check Point SASE
The State of Ransomware Q2 2026:
This Quarter's Trends, and Their Impact on Your Defenses
CheckMates Go:
Half is Not Enough
I installed the client vpn check point mobile and I wish that the internet flows through the vpn
See sk111995: You have to set Hub Mode / Route all traffic to gateway in Global Properties -> Remote Access -> Endpoint Connect -> Route all traffic to gateway -> set to "Yes"
Hello,
Hello,
once "Route all traffic to gateway" is set to YES, is the VPN domain configured in the remote access community checked, or is it treated as if the VPN domain is set to "All Internet"? In other words, if I select this option to YES and the VPN domain for remote access is set to only internal IP addresses, is all traffic still forced through the gateway, without considering the VPN domain setting?
Assuming you don't leave this as a "client decide" option to configure, you are correct.
Yeah. That is correct what Gunther has suggested. It is best way.
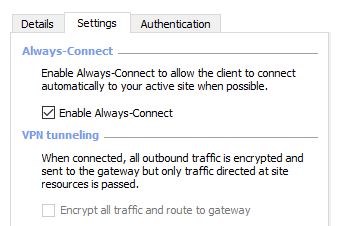
Also you can try with enabling option "VPN Tunneling" on Endpoint client agent itself. but it is manual task.
If you are using SSL VPN with Mobile access blade then follow below procedure to route all traffic to gateway.
https://community.checkpoint.com/message/12386-mobile-access-default-route
Hi,
checkpoint vpn tunneling greyed out ? How do I get this ungreyed out ?
Hi Guys,
can somebody tell me how to change this on the endpoint? we would like to turn on split tunneling only for one endpoint for testing purposes without changing this for everybody via Global Properties.
Thank You,
Basilio Alcantara
Hi Omar,
Did you get any solution? I'm facing same issue in MacOS. For Windows I already saw some workarounds however not applicable for Mac.
Hi,
Yes, you can this. Follow the below step:
Global Properties --> Remote Access --> Endpoint Connect --> Route all traffic to gateway --> set to "Yes"
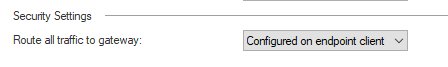
Global Properties - Remote Access End Pont Connect select the following option.
Route All Traffic to GW: Configured on endpoint client
After enabling this, can't access anything outside, only internal. Do we need to enable NAT for the Office Mode subnet, in order to be able access outside?
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 5 | |
| 1 | |
| 1 | |
| 1 | |
| 1 | |
| 1 | |
| 1 |
Thu 01 Oct 2026 @ 05:00 PM (CEST)
Under the Hood: Check Point WAF | Preventing minus-zero-day attacksTue 06 Oct 2026 @ 12:00 PM (ACDT)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus APACThu 01 Oct 2026 @ 05:00 PM (CEST)
Under the Hood: Check Point WAF | Preventing minus-zero-day attacksTue 06 Oct 2026 @ 12:00 PM (ACDT)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus APACTue 06 Oct 2026 @ 03:00 PM (CEST)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus EMEAAbout CheckMates
Learn Check Point
Advanced Learning
YOU DESERVE THE BEST SECURITY