- Products
- Learn
- Local User Groups
- Partners
- More
Scaling Check Point Automation with Arodonata
7 October @ 5pm CET / 11am EDT
What's New in Check Point SASE
The State of Ransomware Q2 2026:
This Quarter's Trends, and Their Impact on Your Defenses
AI Security Masters
Implementing the AI Security Trifecta
CheckMates Go:
Half is Not Enough
Hi Experts,
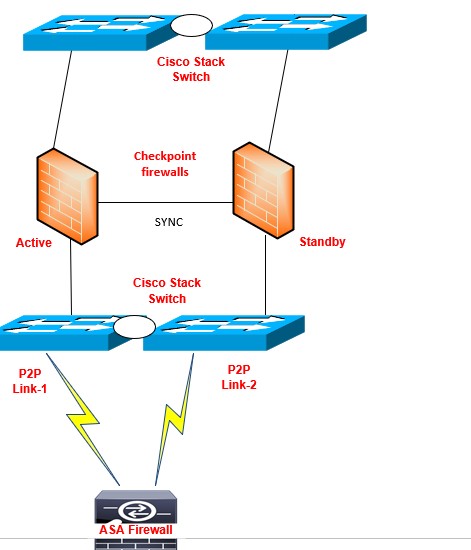
We're planning to replace a Cisco ASA firewall with the Checkpoint firewalls which has P2P link connected. The requirement is that Checkpoint firewalls in HA (Active/Standby) should be able to support the P2P link configuration.
Below is the overview of the architecture. Is this a correct design?
Vendor Firewall (Source) -> P2P link -> Cisco Switches -> Checkpoint firewalls -> Application (Destination)
With regards to the ISP redundancy, I'm unable to find any in R81.X and the last one is related to R80.40 (ISP Redundancy on a Cluster)
1. I believe P2P link configuration is similar to the ISP redundancy. Is my understanding correct?
2. If yes, can you please let me know if the newer versions supports ISP Redundancy on a Cluster?
3. As described in the R80.40 documentation, I don't have any default route towards Internet to monitor the next hop IP. Rather, specific traffic is being allowed towards the core network from the vendor side with the return route. Is it a correct config/design to support ISP redundancy?
Thank you.
We don't support configuring PPPoE with ClusterXL: https://support.checkpoint.com/results/sk/sk101747
Also, ISP Redundancy usually involves multiple Internet connections with a default route.
Hi @PhoneBoy
Thanks for the information. Does it support on a checkpoint over a standalone firewall?
Please note that the links are getting connected to the switch as highlighted.
Thank you.
Personally, I would get an official confirmation from your local SE and TAC.
Do you mean P2P in the context of OSPF configuration or something else?
@Chris_Atkinson wrote:Do you mean P2P in the context of OSPF configuration or something else?
This is P2P link and not related to OSPF
As Phoneboy said, its PPPOE?
Sorry for the confusion. P2P it's a wider term which has been used and it's not a PPPoE. It's a MPLS/Metro-E private link with RJ-45 ports, UTP cables being used.
With the attached design, I believe it'll automatically provide redundancy in the scenarios if any of the link/switch/firewall goes down. I'm happy to be corrected 😊
Ah, point 2 point you mean 🙂
I think the short answer would be that we would recommend an alternate HA solution here, but would need a more complete understanding of the setup to fully settle on how to do it. Probably best to chat to your local sales office about options here.
Why wouldn't you just configure static routes for the relevant network(s) on both gateways in this case?
This would need to be done anyway to ensure that traffic doesn't get lost when a failover occurs on the cluster.
Makes total sense.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 21 | |
| 18 | |
| 15 | |
| 12 | |
| 8 | |
| 8 | |
| 7 | |
| 5 | |
| 5 | |
| 4 |
Mon 28 Sep 2026 @ 03:00 PM (CEST)
La nouvelle réalité des attaques DDoS: autonomie, échelle et avenir de la défenseThu 01 Oct 2026 @ 05:00 PM (CEST)
Under the Hood: Check Point WAF | Preventing minus-zero-day attacksMon 28 Sep 2026 @ 03:00 PM (CEST)
La nouvelle réalité des attaques DDoS: autonomie, échelle et avenir de la défenseThu 01 Oct 2026 @ 05:00 PM (CEST)
Under the Hood: Check Point WAF | Preventing minus-zero-day attacksAbout CheckMates
Learn Check Point
Advanced Learning
YOU DESERVE THE BEST SECURITY