- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hi,
currenty I'm experimenting with Logical Servers.
So far it works fine but there is one point on my list I'm unable to resolve.
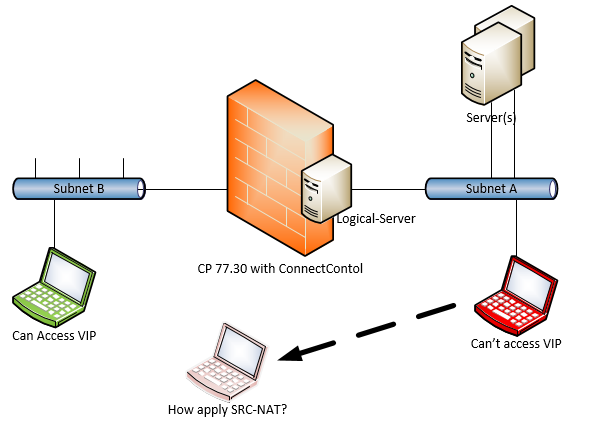
I need to access my logical server from inside the same subnet as the VIP and the real servers.
I managed to set up proxy arp so reqests are forwardet from GW to destination server(s).
Packets are recevived from server(s) but as the src. address is located in the same subnet the replays are send to src directly.
Aswer packets arrive at the client but with real server IP and not VIP -> packets did not pass trough GW so no reverse NAT happend.
To resolve this I think I only have to src-NAT all my connections if they are from same subnet to an IP which is behind Gateway (from servers view)
BUT as ConnectControl is only a more inteligent destination NAT method working as impied rule (0) my src.Nat rules will never match.
Thank you for reading 🙂
/BR
Sascha
Hi,
"Any" in original was the first attempt I made (CISS)
But install aborts: "Invalid <Any> in Source of Address Translation Rule ##. <Any> is valid only it the matching Translated column is <Original>"
But many thanks to you, your reply pushed me back to test with NAT and I found a solution:
Here is the summary what the tasks are to make an logical-server reachable from the same subnet:
Thank you very much for spending your time with my problems.
Best regards,
Sascha
What specific NAT rules have you tried?
I've tried:
ORG-SRC; ORG-DST; ORG-SRV; TRA-SRC; TRA-DST; TRA-SRV
Subnet-of-VIP; VIP; ANY; Subnet-of-VIP-GW-IP(Hide); Original; Original
In log I can see that NAT rule 0 matched (Which is the Logical-Server magic) but my NAT rule did not match.
I think you might have to make Original Source "any" in this context.
Hi,
"Any" in original was the first attempt I made (CISS)
But install aborts: "Invalid <Any> in Source of Address Translation Rule ##. <Any> is valid only it the matching Translated column is <Original>"
But many thanks to you, your reply pushed me back to test with NAT and I found a solution:
Here is the summary what the tasks are to make an logical-server reachable from the same subnet:
Thank you very much for spending your time with my problems.
Best regards,
Sascha
I'm glad you figured it out ![]()
I was actually trying to find how we did this with AWS and ELBs, which also used these objects.
I believe you need to do something similar with NAT rules there.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 10 | |
| 9 | |
| 7 | |
| 6 | |
| 6 | |
| 6 | |
| 4 | |
| 3 | |
| 3 | |
| 3 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaThu 26 Nov 2026 @ 10:00 AM (CET)
The Cloud Architects Series: Cloud Security State in 2026 – Lessons Learned and a Look AheadWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION