- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hello
could you please guide me understanding how rule base checks are done with different layers?
for example i have one policy with 3 layers, 2 layers are shared. when the incoming connection comes will this mean it will first for thru first layer then second and third then get dropped or the first drop rule hit?
thank you
ismar
see this guide for clarity Layers in R80
thank you great help
could you direct me to more detail explanation when defining Ordered layers?
do we only need clean up rule in last layer?
thank you
Please see the following guides for:
Regarding cleanup rules:
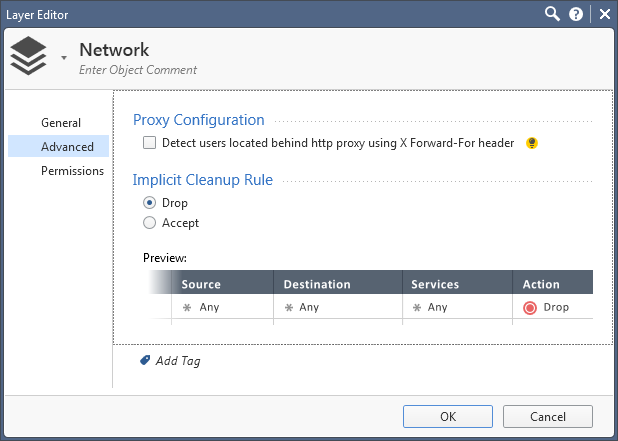
You don't have to define clean up rules explicitly. Each layer has an implicit cleanup rule - either any any accept, or any any drop.
In R7x SmartDashboard we had this generalized - implicit any any drop for the Firewall policy and implicit any any accept for the Application Control policy.
You can control the implicit cleanup rule when you edit a layer and go the the "Advanced" page:

Although it's usually a good best practice to create that cleanup rule explicitly on the rulebase.
And last thing from my on this topic, is it possibly to have 2 Firewall layers in one Policy?
Only for R80.10 GW's and above. Having more than 1 ordered layer for Firewall for pre-R80 GW's will fail policy installation.
Let me know if you have other questions for layers in R80. Other than the discussions that I've linked so far, you can also check the admin guide for general recommendations.
Is this also same for Inline Layer?
When will R80 be available for GW's?
Yes, inline layers have the same editor, and they have the same settings for the implicit cleanup rule.
Using inline layers requires an R80.10 GW, but because R80.10 will be a minor release, the Security Management server and SmartConsole applications are already prepared for designing this type of policies.
For R80.10 release date it is best to follow the Check Point Release Plan.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 28 | |
| 8 | |
| 5 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 4 | |
| 3 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION