- Products
- Learn
- Local User Groups
- Partners
- More

Scaling Check Point Automation with Arodonata
7 October @ 5pm CET / 11am EDT
AI Security Masters
LGTM: Bypassing an LLM Build Gate
When Prompt Injection Fails
What's New in Check Point SASE
The State of Ransomware Q2 2026:
This Quarter's Trends, and Their Impact on Your Defenses
CheckMates Go:
Half is Not Enough
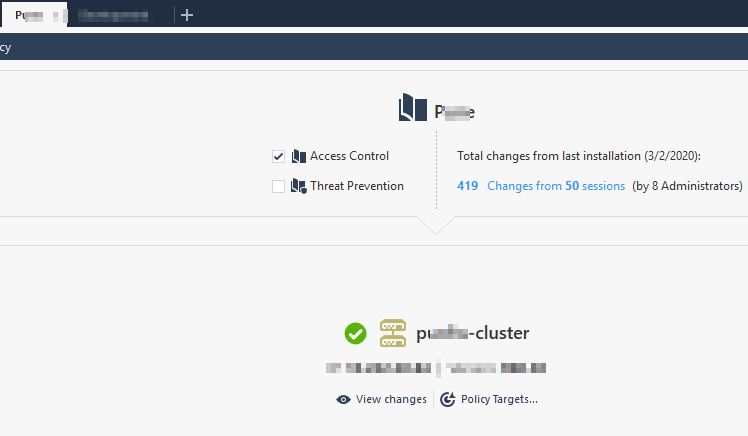
We have Selected 'Policy Targets' as to install on for Cluster. Policy Targets contains the specific gateway cluster.
Now When I install policy on 'Cluster-1' with target set as 'Cluster-1' 0nly in the situation when I do Policy Install on 'Cluster -2' it still shows installed policy changes on Cluster-1 under 'View Chnages'.
I am not sure if I explained it well.
Thanks
Ravi
If you see attached files, Install on is set to 'Policy Targets' which are specific to cluster only. Now When I go to install policy it shows 419 changes which we made on other clusters not on 'P-cluster'. None of the change related to 'P-cluster' but still it shows under changes list while I do install on 'P-cluster'.
Lets assume the following:
This is correct, those changes had not been applied to Cluster_2 yet so they show as not finished, it is the same policy you made changes to.
I have deleted 1 Policy on 'Cluster_1' and its not used on 'Cluster_2' still it shows waiting install on 'Cluster_2'.
We have 15 cluster in our environment. So if I delete 1 policy on 'Cluster_1' it shows pending install on all rest of 14 clusters.
Just not I have deleted rule on another cluster and it shows the changes on 'Cluster_P'.
We have separate policy install package 'Target' used for each clusters. So each clusters are using different policies.
I mean to say Perimeter firewall will not have same policies as inside firewall. Still if I made any changes on Inside firewall its shows on Perim firewall in pending install.
Is this something known or same policy thing?
Regards,
Ravi
If each policy is only related to a specific cluster, do you have the installation target set? - Yes it set to specific cluster target only.
I have observed this thing in scenario where 'Object_X' is used only on 'Cluster_1' and I do changes on 'Object_X' it will set to install for all the clusters.
Though I need to try other possible way to fix.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 32 | |
| 9 | |
| 7 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 4 | |
| 3 |
Tue 06 Oct 2026 @ 12:00 PM (ACDT)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus APACTue 06 Oct 2026 @ 03:00 PM (CEST)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus EMEATue 06 Oct 2026 @ 02:00 PM (EDT)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus AMERTue 06 Oct 2026 @ 12:00 PM (ACDT)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus APACTue 06 Oct 2026 @ 03:00 PM (CEST)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus EMEATue 06 Oct 2026 @ 02:00 PM (EDT)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus AMERThu 08 Oct 2026 @ 11:00 AM (EDT)
Under the Hood: Check Point SASE | Zero Trust Network Access, Step by StepAbout CheckMates
Learn Check Point
Advanced Learning
YOU DESERVE THE BEST SECURITY