- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hi community,
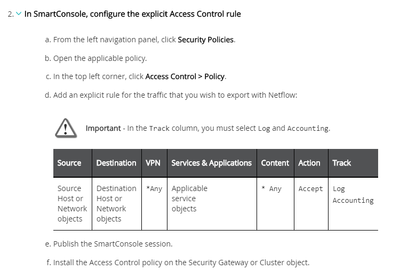
since R80.30 netflow export needs to be additionally configured on each rule via adding the "Accounting" option:
Could someone please share their experience regarding performance when enabling accounting ?
I remember some days in the past that the accounting option was very performance intense ...
And also how are we supposed to manage this with a 1000+ ruleset ?
Thanks and regards
Thomas
Thank you all for the feedback. Understood. In R81, the default behavior will be same as R80.10 and we are working to make a fix available in Jumbo HFs for R80.30/40 as soon as possible. Here is the silver line, now users can selectively choose FW rules for minimal impact on the performance or debugging purpose.
Due to architectural changes in R80.20, we had to make a hard decision regarding Netflow functionality.
The massive performance impact was back in the days before SecureXL, which handles this pretty efficiently.
There is some extra logging traffic, as you might imagine.
Dear Tom, we are suffering the same issues on our site.
Netflow stopped working since we upgraded and now we have to enable the accounting on thousands of rules , something that was not required at all in R80.10. this doesn't make any sense even when they are going to revert back this feature in R81, meaning that the accounting won't be required to get Netflow working.
Checkpoint, before performing these behaviour changes, you should think on the fact that these changes are causing a huge time consuming for your customers and not only this, but also the high performance impact it has on the MLMs.
Thank you all for the feedback. Understood. In R81, the default behavior will be same as R80.10 and we are working to make a fix available in Jumbo HFs for R80.30/40 as soon as possible. Here is the silver line, now users can selectively choose FW rules for minimal impact on the performance or debugging purpose.
Due to architectural changes in R80.20, we had to make a hard decision regarding Netflow functionality.
From R80.40 jumbo take 87 the default behaviour is to export flows for all rules.
With reference to sk102041, flow export per rule (requires accounting to be enabled on the rule) can still be configured.
Warning: the clish message (below example is from R81) is wrong. 0 is the default. As per the sk:
"Note: 1 - generate netflow records only for rules with accounting enabled. 0 - generate netflow records for all firewall rules (applicable only for R80.40 JHF T87 and above)."
fw> set netflow fwrule
fwrule:
1: NetFlow Export for all FW rules (default).
0: NetFlow Export only for specific FW rules that
has Accounting enabled in Smart Console.
fw>
Can someone from R&D look at this incorrect message (and check other versions)?
We have netflow issue post upgradation to R80.40 but it is not related to enabling the Accounting option. We had R80.20 and Netflow is enabled with Loopback IP as Source IP and pushed the netflows in the VPN tunnel to Netflow collector which is at remote office. Upgraded to R80.40 since then the Netflows are not using the Loopback IP address as source rather they are trying to use the outgoing Interface IP address(Public IP in my case) as source IP address. removed and reconfigured but it did not work. tried configuring different collector pointing to the Local LAN with Loopback IP as Source IP still the Netflows using the outgoing Interface IP as source IP only. Any idea ?
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 28 | |
| 8 | |
| 7 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 4 | |
| 3 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION