- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Identity and Trust?
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hello everyone,
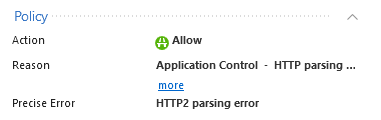
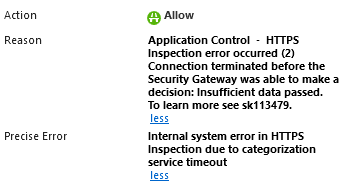
In our network environment, we have two firewalls. We attempted to enable SSL inspection on both firewalls, but encountered an error message: “HTTP parsing error.” Notably, both firewalls utilize the same self-signed certificate for outbound inspection. Surprisingly, when we enable HTTPS inspection on only one of the firewalls, everything functions correctly.
Checkpoint firewall is second device in architecture.
the issue is happened on different sites, for example ssllabs.com, apple.com.
some sites work correctly for example udemy.com with inspection enabled.
What steps should we take to troubleshoot this issue?
Thank you
On the problematic firewall could you check if you can access the internet from this gateway?
https://support.checkpoint.com/results/sk/sk108202
Check:
Also I am not sure if 2 Check Point firewalls in the same traffic flow is good with both HTTPS inspection.
Documentation states: HTTPS Inspection can be enabled on a single Security Gateway at first, and then expanded to additional Security Gateways.
Does not mention if they can be inline, so worth checking. Maybe someone else knows that here.
Hey,
The first fw is not Checkpoint
If I activate ssl decryption on one of them everything works fine, the problems start when on both of them try to opens tls traffic.
All Firewalls have access to the internet
Sorry, no offense meant - but i just read your issue to my tech support collegues and we had a big laugh together 🤣
It is no wonder that this does not work; and what could be achieved by 2 times SSL inspection ? I would suggest to enable SSL inspection on CP GW only.
Firewall vendors may employ a variety of for detecting threats within encrypted traffic, such as signature-based detection, behavior analysis, machine learning algorithms, heuristics, anomaly detection, or sandboxing. Each technique has its strengths and weaknesses, and vendors may prioritize different approaches based on their research, development, and expertise
This is in addition to the constraints that exist in the organization due to a complex topology
In addition, I don't see any problem with ssl decryption by different vendorim, in other environment there are both firewalls, and proxy's, and products for ssl visabilty, which decrypt tls one after the other without any problem.
Double https inspection makes certificate management complex. It is done via MITM and client needs to trust the certificate from gateway. In this case 2. In this case the first firewall will be the client from Check Point point of view. Due that the first gateway sets up the connection on it's own (if inspected).
client <-> first firewall (MITM HTTPS inspection) <-> Check Point (MITM HTTPS inspection) <-> Web server
The Check Point will be inspecting traffic initiated from the first firewall. The first firewall starts the traffic because it is doing MITM for the client. I am getting headache only thinking about this scenario.
Can you give a sketch of the network topology ?
Hey,
In this scenario, client access to the internet through two firewalls. The first one is a LAN firewall (not Checkpoint) that performs LAN segmentation and forwards traffic to the second firewall, which is a WAN firewall that perfom a accses to internet (Checkpoint).
Thank you
Ah first fw is not Check Point that changes is. It still can be config error. Start with the SK's below:
https://support.checkpoint.com/results/sk/sk108202
https://support.checkpoint.com/results/sk/sk65123
https://support.checkpoint.com/results/sk/sk64521
https://support.checkpoint.com/results/sk/sk112214
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 28 | |
| 9 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 4 | |
| 3 | |
| 3 |
Tue 17 Nov 2026 @ 08:30 AM (EST)
Bogota Breakfast & Hack: IA bajo control y ataques en vivo con Workspace SecurityTue 17 Nov 2026 @ 05:00 PM (CET)
AI Security Masters: Security in the Pace of AI: From Threat to Force MultiplierTue 17 Nov 2026 @ 11:00 AM (EST)
Under the Hood: Check Point SASE | Troubleshooting Like a ProTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaTue 17 Nov 2026 @ 05:00 PM (CET)
AI Security Masters: Security in the Pace of AI: From Threat to Force MultiplierTue 17 Nov 2026 @ 11:00 AM (EST)
Under the Hood: Check Point SASE | Troubleshooting Like a ProTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseTue 17 Nov 2026 @ 08:30 AM (EST)
Bogota Breakfast & Hack: IA bajo control y ataques en vivo con Workspace SecurityAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION