- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Identity and Trust?
11 November @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hi all,
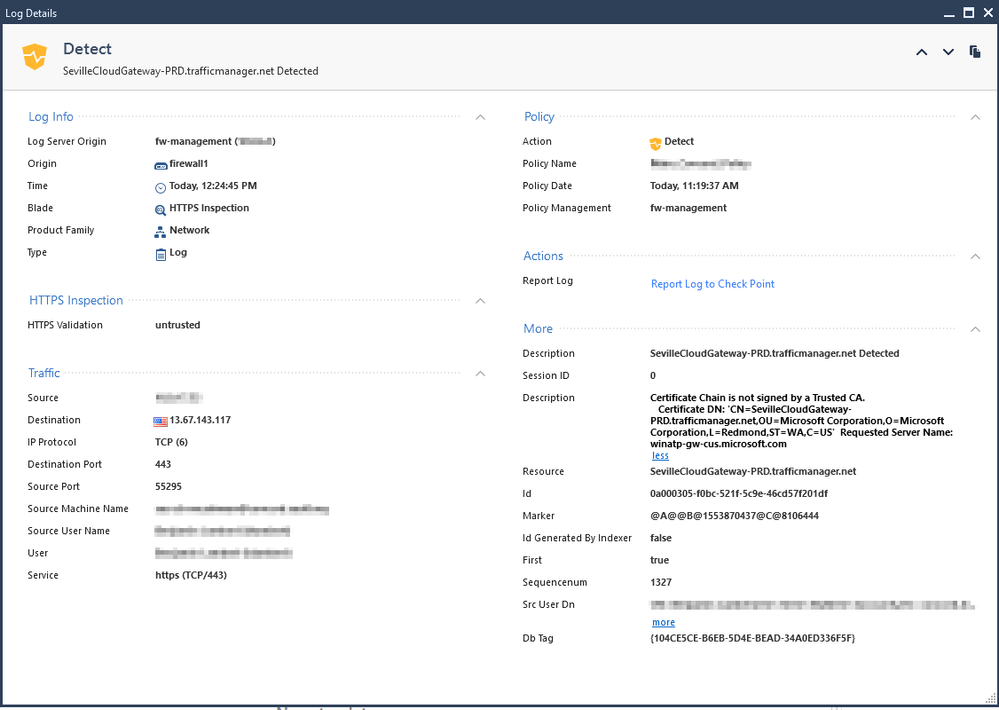
I have a gateway running 80.20 M2 and I recently enabled SSL Inspection for a small group. It is working correctly (I see our cert in the browser and no warnings), but I see some strange errors in the logs and sometimes in the browser about the "certificate chain not signed by a trusted CA".
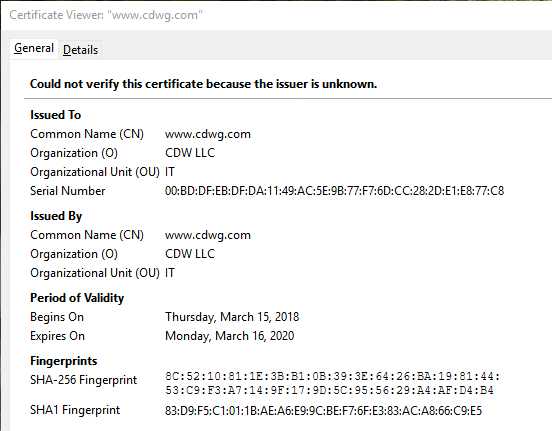
When I look at the certificate, it seems to be missing the original CA and didn't insert our CA/cert.
For example, normal certs look like: DigicertCA-->www.CDWG.com
Inspection working: MYEnterpriseCA-->www.CDWG.com
When I see errors it looks like: www.CDWG.com
Am I missing something?
Thanks!
--Ben
the DigiCert certificate is not in R80.20 root certificate store.
So you get a certificate chain error.
Look at this sk:
sk114679 - HTTPS Bypass (with Site Category) not working for Servers with Self-Signed Certificate
Thank you, this was ultimately the issue. For some reason Check Point did not have Digicert Global Root G2/G3 in the certificate store. I was able to download them from their support site and add them.
Is there a way to ensure that the Check Point cert store is being automatically updated, apart from checking the box?
Thank you very much!
--Ben
It’s impossible for a gateway to be running R80.20.M2 because that’s a Management-only release. What is the gateway actually running here? Also, is this happening consistently for specific sites or at random?
the DigiCert certificate is not in R80.20 root certificate store.
So you get a certificate chain error.
Look at this sk:
sk114679 - HTTPS Bypass (with Site Category) not working for Servers with Self-Signed Certificate
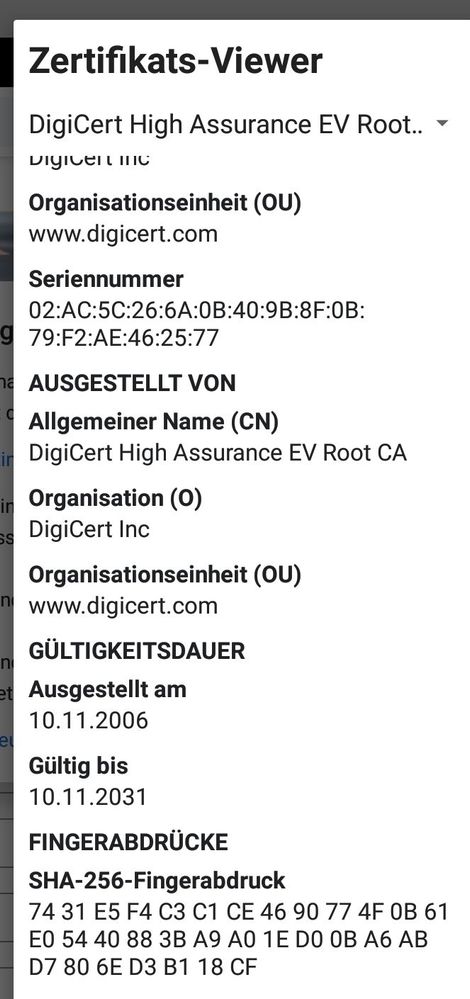
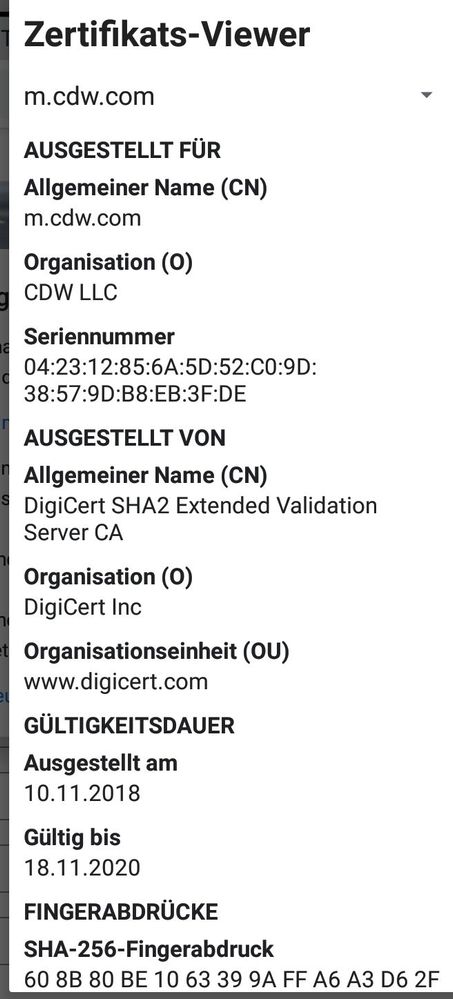
Here the root certificate. This certificate is not in the root certificate store.
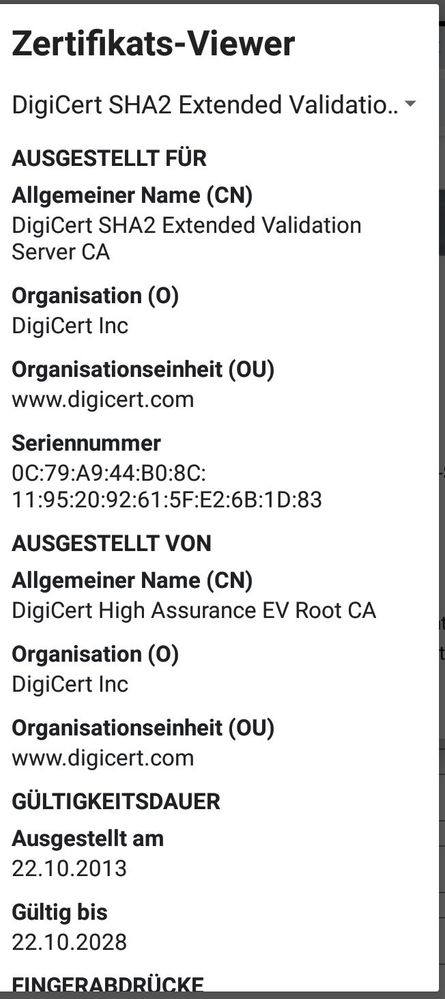
Here the intermediate certificate:
And here the web server certificate:
Sorry for the german names in the pictures. I write on a samsung tab s4 and I cannot change the browser to english.
Thank you, this was ultimately the issue. For some reason Check Point did not have Digicert Global Root G2/G3 in the certificate store. I was able to download them from their support site and add them.
Is there a way to ensure that the Check Point cert store is being automatically updated, apart from checking the box?
Thank you very much!
--Ben
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 29 | |
| 14 | |
| 11 | |
| 7 | |
| 6 | |
| 4 | |
| 4 | |
| 4 | |
| 4 | |
| 3 |
Tue 10 Nov 2026 @ 06:00 PM (IST)
Under the Hood: Introducing Check Point Cloud Firewall as a ServiceTue 10 Nov 2026 @ 08:00 PM (IST)
Check Point Mobile Security | Extending Zero Trust with NetskopeThu 12 Nov 2026 @ 11:00 AM (EST)
Tips and Tricks 2026 #15: Check Point MDR and Incident ResponseTue 10 Nov 2026 @ 06:00 PM (IST)
Under the Hood: Introducing Check Point Cloud Firewall as a ServiceTue 10 Nov 2026 @ 08:00 PM (IST)
Check Point Mobile Security | Extending Zero Trust with NetskopeThu 12 Nov 2026 @ 11:00 AM (EST)
Tips and Tricks 2026 #15: Check Point MDR and Incident ResponseTue 17 Nov 2026 @ 08:30 AM (EST)
Bogota Breakfast & Hack: IA bajo control y ataques en vivo con Workspace SecurityAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION