- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Identity and Trust?
11 November @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hello community,
I would like to know whether there is a way to configure HTTPS Inspection Bypass for a certain domain (e.g. google.com) when using Security Gateway (in our case a virtual system / VSX environment) as HTTPS Proxy (non-transparent)!?
When configuring a bypass rule in HTTPS Inspection Policy with Security Gateway / Virtual System as Destination then it works, but then all relevant traffic will bypass HTTPS Inspection (for traffic from client to Security Gateway / HTTPS Proxy) and that's not desired configuration.
R81.10 JHF Take 79 is installed on the Security Gateways and Management Server.
Thanks in advance for your help!
Best Regards
Nenad
HTTPS Inspection always sees the gateway as the destination when non-transparent proxy mode is used.
As such, the HTTPS Inspection policy will never match another destination.
This is expected behavior.
https://support.checkpoint.com/results/sk/sk108706
I remember testing this back in R77 versions, but not in R80+, so trying to remember how I made it work. I know I had to make some modifications on the gateway settings in smart console...can you send a screenshot of how https proxy tab is configured on gateway object?
Cheers,
Andy
Hi Andy,
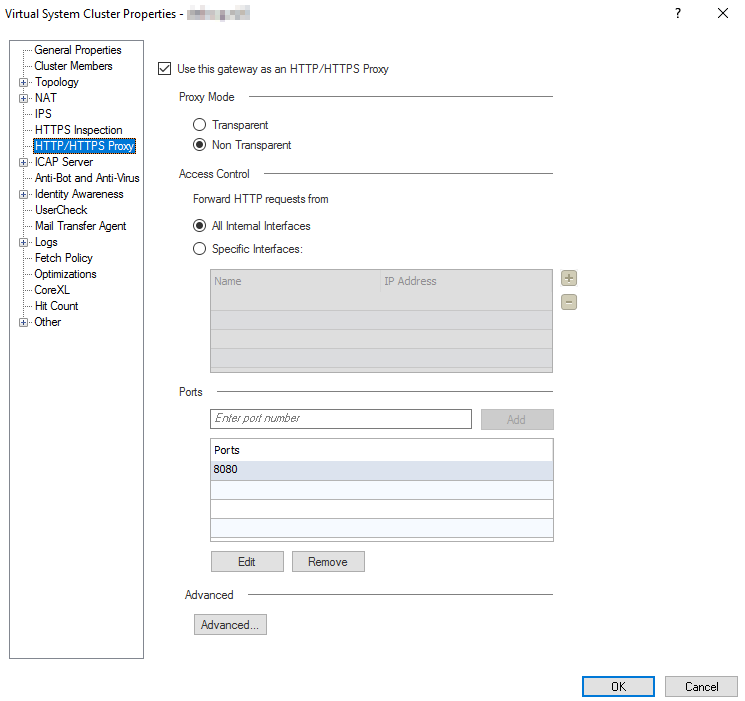
here a screenshot of the HTTP Proxy tab on the Security Gateway / Virtual System object:
Thanks in advance for your help!
Best Regards
Nenad
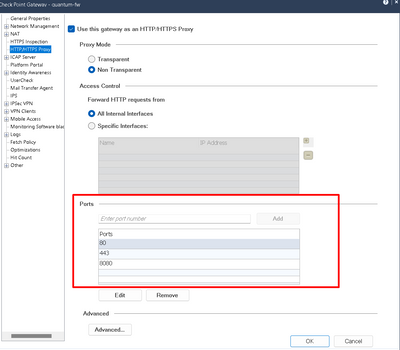
No problem, thank you. I will have to check and see if I had to modify the actual ports at the bottom, so give me some time. Apologies, this was probably more than 7 years ago, so will need to see if I still have details on how I did this.
Ok, just made it work by modifying below:
Hi Andy,
thanks very much for sharing the information.
But I think I didn't get it how that will help to configure certain HTTPS Inspection Bypass rules when using the proxy.
Anything else I need to configure?
Could you please explain?
Thanks in advance!
Best Regards
Nenad
From notes I have, that was the only change I had to make on CP side. Can you send a screenshot of bypass rule(s)?
Hi Andy,
a common bypass rule looks like the following:
I will check whether it works with proxy settings you mentioned.
Thanks!
Best Regards
Nenad
Sounds good, yea, bypass rule looks right to me. If it still does not work, I will dig further and see if there was anything else I had to change.
ANdy
HTTPS Inspection always sees the gateway as the destination when non-transparent proxy mode is used.
As such, the HTTPS Inspection policy will never match another destination.
This is expected behavior.
https://support.checkpoint.com/results/sk/sk108706
Interesting...I tested this today in my R81.20 lab and when gateway is configured as non-transparent proxy, the https bypass rules worked just fine.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 29 | |
| 14 | |
| 11 | |
| 7 | |
| 6 | |
| 4 | |
| 4 | |
| 4 | |
| 4 | |
| 3 |
Tue 10 Nov 2026 @ 06:00 PM (IST)
Under the Hood: Introducing Check Point Cloud Firewall as a ServiceTue 10 Nov 2026 @ 08:00 PM (IST)
Check Point Mobile Security | Extending Zero Trust with NetskopeThu 12 Nov 2026 @ 11:00 AM (EST)
Tips and Tricks 2026 #15: Check Point MDR and Incident ResponseTue 10 Nov 2026 @ 06:00 PM (IST)
Under the Hood: Introducing Check Point Cloud Firewall as a ServiceTue 10 Nov 2026 @ 08:00 PM (IST)
Check Point Mobile Security | Extending Zero Trust with NetskopeThu 12 Nov 2026 @ 11:00 AM (EST)
Tips and Tricks 2026 #15: Check Point MDR and Incident ResponseTue 17 Nov 2026 @ 08:30 AM (EST)
Bogota Breakfast & Hack: IA bajo control y ataques en vivo con Workspace SecurityAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION