- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hello Mates 🙂
I'm testing an OSPF configuration in a CheckPoint Firewall cluster with 2 different routers.
I'm not able to avoid to announce all networks from Area0 (the ones directly connected in the Firewall but also the ones learned by OSPF in Backbone Area "0") to Area 1.
I attached a simple network diagram for better understanding.
My Configuration:
My Goal:
My failed attempts:
My understanding: Open to clarifications 🙂
Thanks in advance for your help !
Bruno Petrónio
Just for the sake of sharing, i ended up creating a different instance with Area 1 and then redistributing what i needed.
Hi Bruno.
Thank you for your detailed post.
Have you configured the ospf areas in cli?
Sometimes I find configuring OSPF is better in CLI.
This way, you can set the redistribution options for OSPF areas and also restrict to apply restrictions to areas.
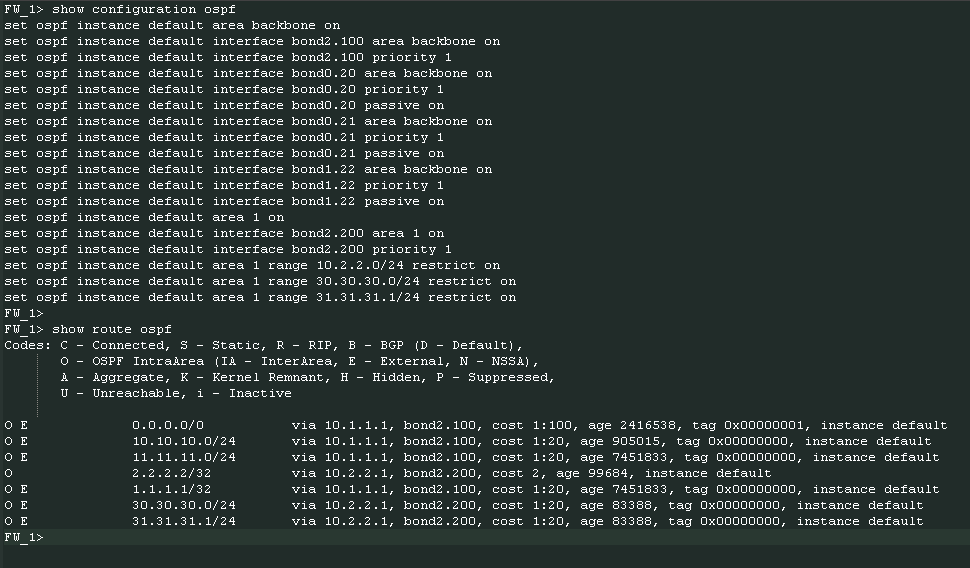
A copy of your OSPF configuration maybe handy here - blanking out any ip addresses if you so wish to.
Please get this from running show configuration on the firewall CLI
Hi Jack,
I've done the config in GUI, but re-done in clish 🙂
I was thinking redistributing was about different protocols and not inside the same protocol (in same instance).
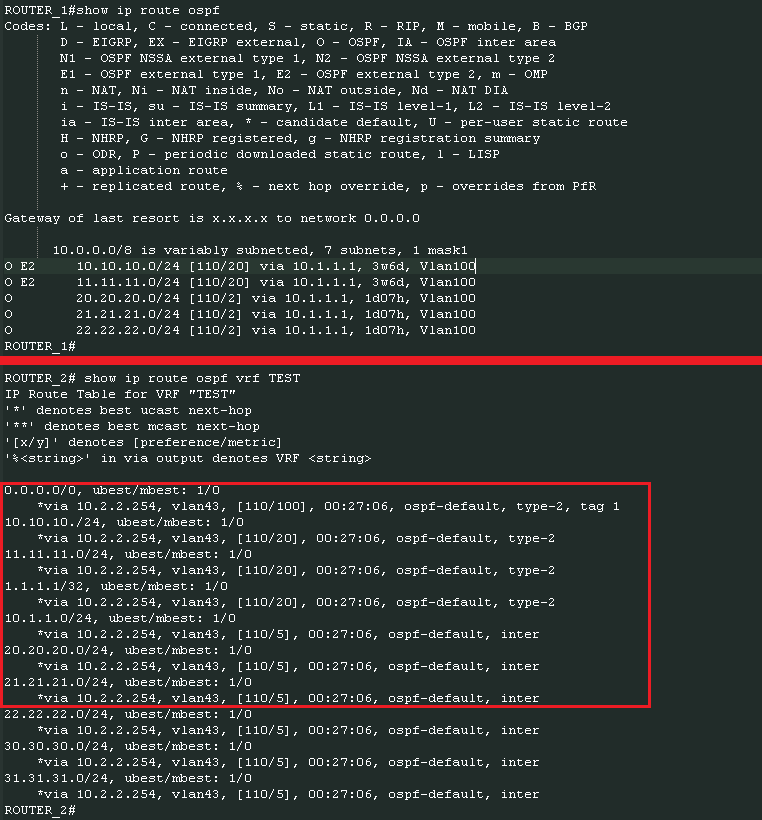
The ospf output config as the show route output
The router outputs:
Thanks in advance!
Hi Bruno,
To advertise the routes to the different area, you need to do a 'set ospf area xxxx range xxx.xxx.xxx.xx on
Then, as you have done above, to restrict routes, you need to do a 'set ospf area xxx range xxx.xx.xxx.xxx restrict on'
Let me know how you get on 🙂
Hi Jack,
Without doing the "set ospf instance default area 0 range xxx.xxx.xxx.xx on", im still getting in Router_2 all the networks belonging from Router_1 and all networks defined in the Firewall as belonging in Area0.
I give it the chance to try, and even if i allow the range 10.0.0.0/7 and then restrict the 11.11.11.0/24, (in area 0 configuration) i still see both (10.10.10.0/24 and 11.11.11.0/24) in my Router_2 learned by OSPF.
What i could see as different was when i did the same for 20.0.0.0/6, without restrict any i got a summarized route instead 3 individual.
Restriction still don't restrict from Area0 to Area 1.
In Admin guide they always mention add and restrict networks from other areas to Backbone... I'm wondering if this is a limitation ?!
😞
Just for the sake of sharing, i ended up creating a different instance with Area 1 and then redistributing what i needed.
One thing I would like to do is:
Ensure the Checkpoint is advertising only a default route into an OSPF area (NSSA), but learns other routes in that area, would the above achieve this?
So on the switch the only route it should pickup is a default route via the Checkpoint.
On the Checkpoint learn any connected routes and advertised routes from the switch.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 30 | |
| 8 | |
| 7 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 3 | |
| 3 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION