- Products
- Learn
- Local User Groups
- Partners
- More

Scaling Check Point Automation with Arodonata
7 October @ 5pm CET / 11am EDT
AI Security Masters
LGTM: Bypassing an LLM Build Gate
When Prompt Injection Fails
What's New in Check Point SASE
The State of Ransomware Q2 2026:
This Quarter's Trends, and Their Impact on Your Defenses
CheckMates Go:
Half is Not Enough
Hi Everybody
I want to set up the SMTP/TLS configuration with a certificate on our Checkpoint cluster under MTA.
I have summarized the certificate in a .p12, as this is the file type Checkpoint wants. At least it can only be uploaded as .p12.
I have executed the following command:
openssl pksc12 -export -out cert.p12 -inkey key.pem -in fullchain.pem
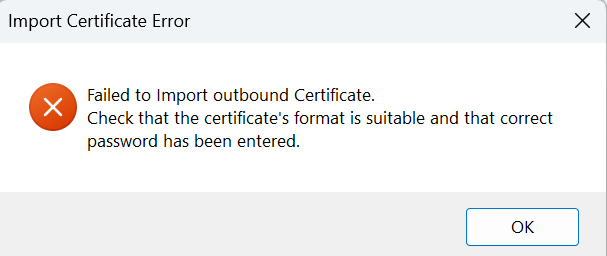
Then the password query appears and I have tried everything. Even with a two-digit password that I have entered correctly, the import always fails with this error message:
Is there something wrong with the format that I need to be aware of?
Thanks for your help!
Marius
Hi @marius_kade
What is the version? R81.20 take ?
Here is an sk: https://support.checkpoint.com/results/sk/sk123237
"Failed to import outbound certificate. Check that the certificate's format is suitable and that the correct password has been entered"
Maybe you are under take 70.
Akos
Hi @marius_kade
Great, but I suggest you to consider the upgrade 🙂
Akos
Looks like this may be the issue: https://support.checkpoint.com/results/sk/sk123237
Upgrade to JHF 152 or above.
Hi @marius_kade
What is the version? R81.20 take ?
Here is an sk: https://support.checkpoint.com/results/sk/sk123237
"Failed to import outbound certificate. Check that the certificate's format is suitable and that the correct password has been entered"
Maybe you are under take 70.
Akos
Hi @AkosBakos ,
thanks for your reply. 🙂
We are currently on R81.10 Take 150
But i can see in Take 152 the problem may be solved. I will check if my certificate is using SHA 256 hashing algorithm tomorrow and maybe do an update to Take 152.
I will come back and report.
Thanks,
Have great day!
Hi @marius_kade
Great, but I suggest you to consider the upgrade 🙂
Akos
The Certificate is in SHA256.
I will do the Update to Take 172 and try again after this.
Thanks for your help! 🙂
Have you verified the .p12 file contains all the relevant information?
It should contain the private key and the entire (public) certificate chain (CA and all intermediates).
Yes, the .p12 contains the certificate, key and fullchain.
Creted with this command:
openssl pksc12 -export -out cert.p12 -inkey key.pem -in fullchain.pem
Inside the fullchain.pem are these certificates in this order:
cert - intermediate1 - intermediate2 - root(CA)
Thanks!
Looks like this may be the issue: https://support.checkpoint.com/results/sk/sk123237
Upgrade to JHF 152 or above.
It's all done and worked after the update.
Many thanks and have nice weekend to both of you! 😄
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 33 | |
| 8 | |
| 7 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 4 | |
| 3 |
Thu 01 Oct 2026 @ 05:00 PM (CEST)
Under the Hood: Check Point WAF | Preventing minus-zero-day attacksTue 06 Oct 2026 @ 12:00 PM (ACDT)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus APACTue 06 Oct 2026 @ 03:00 PM (CEST)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus EMEAThu 01 Oct 2026 @ 05:00 PM (CEST)
Under the Hood: Check Point WAF | Preventing minus-zero-day attacksTue 06 Oct 2026 @ 12:00 PM (ACDT)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus APACTue 06 Oct 2026 @ 03:00 PM (CEST)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus EMEATue 06 Oct 2026 @ 02:00 PM (EDT)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus AMERAbout CheckMates
Learn Check Point
Advanced Learning
YOU DESERVE THE BEST SECURITY