- Products
- Learn
- Local User Groups
- Partners
- More
What’s New in Agentic Network Orchestration
21 October @ 5pm CET / 11am EDT
AI Security Masters
LGTM: Bypassing an LLM Build Gate
When Prompt Injection Fails
Scaling Check Point Automation with Arodonata
CheckMates Go:
Fun Ding
Hello Mates!
I have a case that I would like your help to know what I can do about it...
I have a customer that is a Financial Corporate. They have a GW in their environment with the latest updates (R81.10 T81 (a VM)).
A few days ago a company did some tests (I'm not sure about how this was done) and sent us a sheet with some "vulnerabilities" found in the gateway.
But the part that I was in doubt about was those recommendations below:
How can I "install a server certificate" on gateway? What does it mean exactly?
Thank you for your support!
Implied rules will always allow port 80 and 443 connections to the firewall itself via multiportal, even if there is no feature enabled to actually talk to and exploit. If this is unacceptable you can do the following, but bear in mind this will break any kind of Remote Access VPN access:
1) Create an indefinite SAM rule from the SmartView Monitor or via the fw sam command blocking connections with a destination of the firewall's outside IP on ports 80 and 443
2) See sk165937: How to disable the connection to Security Gateway on TCP Port 80 and on TCP Port 443 to disable the implied rule completely
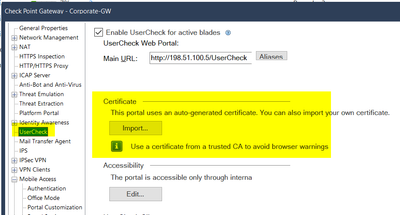
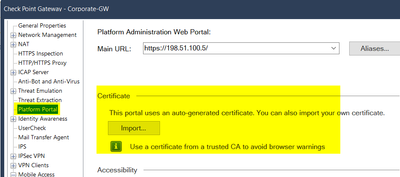
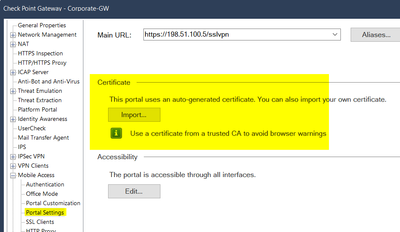
@Bernardes the gateways runs MultiPortal mentioned by @Timothy_Hall. There are several places to replace the default self signed certificates to one trusted by a known CA.
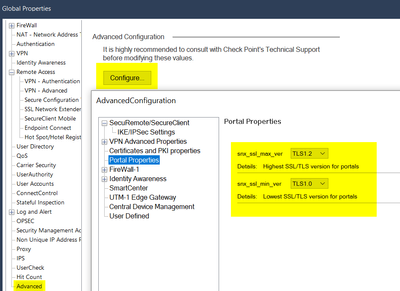
Here you can change the supported TLS version:
@Bernardes from a technical point of view you can use the same certificate for all if it matches the names/ip-addresses. But it's used for different needs. One for MobileAccessPortal, one for GAiA WebUI the platform portal and one for UserCheck webpage. Typically we are using different certificates.
Is customer using https inspection?
Hello @the_rock that feature is disabled on this gateway.
It probably does not like a self-signed certificate on the gaia admin portal. How to create and configure certificate for Gaia Portal (checkpoint.com)
Excellent point indeed.
hello, @Lloyd_Braun there's no certificate to access gaia portal indeed. Can it be the cause for these vulnerabilities found ?
I am pretty sure @Lloyd_Braun got it right, makes perfect sense.
@Bernardes the gateways runs MultiPortal mentioned by @Timothy_Hall. There are several places to replace the default self signed certificates to one trusted by a known CA.
Here you can change the supported TLS version:
@Wolfgang thank you for your advice!
@Wolfgang just a question... All these portals require a different certificate for each one or can it be the same SSL certificate for all?
@Bernardes from a technical point of view you can use the same certificate for all if it matches the names/ip-addresses. But it's used for different needs. One for MobileAccessPortal, one for GAiA WebUI the platform portal and one for UserCheck webpage. Typically we are using different certificates.
@Wolfgang Thank you for all! You help me a lot!
We are here to help...happy new year!!
Agree with @Wolfgang . Yes, you can use same cert, but its probably better practise to use different ones.
Implied rules will always allow port 80 and 443 connections to the firewall itself via multiportal, even if there is no feature enabled to actually talk to and exploit. If this is unacceptable you can do the following, but bear in mind this will break any kind of Remote Access VPN access:
1) Create an indefinite SAM rule from the SmartView Monitor or via the fw sam command blocking connections with a destination of the firewall's outside IP on ports 80 and 443
2) See sk165937: How to disable the connection to Security Gateway on TCP Port 80 and on TCP Port 443 to disable the implied rule completely
@Timothy_Hall thank you very much for the tip!
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 24 | |
| 22 | |
| 14 | |
| 10 | |
| 6 | |
| 4 | |
| 4 | |
| 4 | |
| 4 | |
| 4 |
Thu 15 Oct 2026 @ 05:00 PM (CEST)
What If Email Security Ran Your Security Awareness Program?Tue 20 Oct 2026 @ 05:00 PM (CEST)
EMEA: Beyond the Basics: Designing Identity Awareness for Large-Scale EnvironmentsTue 20 Oct 2026 @ 03:00 PM (EDT)
AMER: Beyond the Basics: Designing Identity Awareness for Large-Scale EnvironmentsThu 22 Oct 2026 @ 11:00 AM (CEST)
The Cloud Architects Series: Cloud Security as a Service – Combining WAFaaS and CFaaSThu 15 Oct 2026 @ 05:00 PM (CEST)
What If Email Security Ran Your Security Awareness Program?Tue 20 Oct 2026 @ 05:00 PM (CEST)
EMEA: Beyond the Basics: Designing Identity Awareness for Large-Scale EnvironmentsTue 20 Oct 2026 @ 03:00 PM (EDT)
AMER: Beyond the Basics: Designing Identity Awareness for Large-Scale EnvironmentsThu 29 Oct 2026 @ 03:00 PM (EDT)
Americas Deep Live: What's New in Check Point Firewall R82.20Thu 29 Oct 2026 @ 11:00 AM (PDT)
Irvine, CA: Secure the Network, the App, and the Workforce: A Hybrid Mesh & SASE BriefingAbout CheckMates
Learn Check Point
Advanced Learning
YOU DESERVE THE BEST SECURITY