- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hi,
I'm currently using the Identity Collector to get AD data. Now I got a use case involving Radius as a source for Identity Awareness. May I avoid activating AD Query for group membership lookups for these users? (I dont need group memberships at all, just user names from radius in checkpoint logs). Any advise?
kind regards,
mp2012
Hi,
you don't need to activate AD querry to use radius accounting. The PDP Gateway will do the LDAP querries torwards your AD for the users and group memberships.
Best regards
Well, in Identity Awareness log I get "failed login" fpr this radius entries. Description says "Group membership of the required account (user or machine) could not be retrieved from the AD. Make sure the account exists in the AD."
So it seems there is no query done to identity Collector.
kind regards
Hi,
this error message indicates, that the PDP Gateway is not able to find the user via ldap in your AD. Your Identity Collector is not doing the LDAP search. This is always done by the PDP Gateway with configured LDAP Server Object.
This can have many diffrent issues. Please check the following SK:
"Group membership of the required account (user or machine) could not be retrieved from the AD" log ...
Best regards
Hi,
I guess scenario 6 fits. At least it shows me this username format in IA log "source user name"column. Checking with "pdp monitor all" at the gateway,I dont see this usernames. Anyway this should be fixed since R80.20 (I'm on 81.10). I still got a configured LDAP account unit for the AD configured.
Hi,
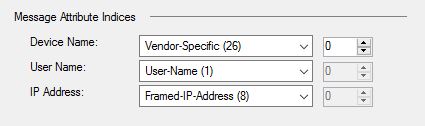
in which format are your users authenticating in your RADIUS Identity Source? I think the format is depending on the device/vendor from where the radius account event is sent.
You have to be sure, that the RADIUS Accounting settings on the receiving PDP Gateways are matching:
For example:
See attached Screenshot.
Please also make sure to verify if the source is sending sAM or UPN format. See the following sk:
Users are not authenticated when an identity source provides the login name in 'User Principal Name'...
RADIUS authentication fails for LDAP users as gateway uses sAMAccountName and not UPN when UPN neede...
Using "User logon name (Pre-Windows 2000)" different then "User logon name" with Identity MUH agent ...
This also could be the issue here.
Best regards
I have AD query disabled under the firewall object in Smart Console and only use ID collectors.
But I still have a LDAP account unit. Please check if you have that for the relevant AD servers.
I think the firewalls still reach out towards the DC's to make sure the collectors information is valid.
It is to remove load for gateways towards collectors.
Hi,
yes, I still got a proper LDAP AD account unit configured.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 28 | |
| 8 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 4 | |
| 3 | |
| 3 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION