- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Identity and Trust?
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hi,
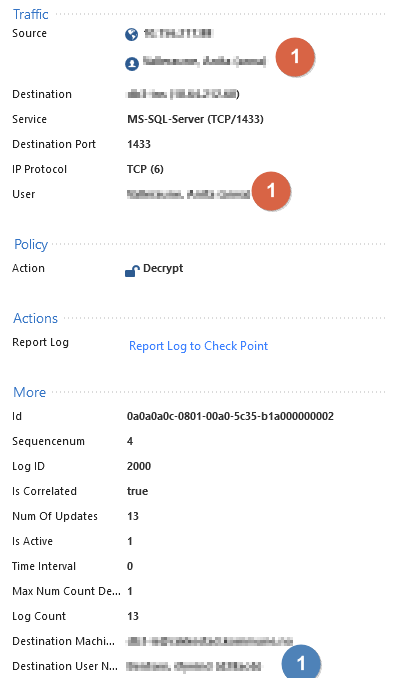
This is a screenshot from an Application log which shows me two different usernames.

Marked with orange and number 1 have the same username. Marked with blue is a different username. Why is destination user name different from the User field?
Because user b logged in to the database server (on the windows system) and the IP of the server was associated with this user.
A session from user a only shows this information as this information was not deleted (has not timed out).
Destination Username is the one associated to destination IP.
Associated in which way? Can you explain more please.
By identity awareness depending on your configuration. I assume ADquery or IDC.
I understand that. But if user a access a MS-SQL database, why is a different user b shown on destination username?
Because user b logged in to the database server (on the windows system) and the IP of the server was associated with this user.
A session from user a only shows this information as this information was not deleted (has not timed out).
Thanks for explaining. Since this was a correlated log showing user a accessing a database I don't see the point in this log of having the information about user b that is associated with that server. Do you?
I wouldn't need this information, but better have an information I don't need, than omitting it 🙂
Btw. if you don't need identity awareness on your servers (as source), you could exclude the server networks generally from IDC or ADquery.
While I usually see omitting data as a bad thing, in this case I was misled by the wording "Destination User Name". In my experience, some logs look like user a is a compromised account that's trying to access the system at the IP that user b is associated to. I'll be updating my team and any others that ask about that feature. Maybe a name change on those fields can be considered? Also "Dst User Dn"
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 28 | |
| 10 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 4 | |
| 3 | |
| 3 |
Tue 17 Nov 2026 @ 08:30 AM (EST)
Bogota Breakfast & Hack: IA bajo control y ataques en vivo con Workspace SecurityTue 17 Nov 2026 @ 05:00 PM (CET)
AI Security Masters: Security in the Pace of AI: From Threat to Force MultiplierTue 17 Nov 2026 @ 11:00 AM (EST)
Under the Hood: Check Point SASE | Troubleshooting Like a ProTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaTue 17 Nov 2026 @ 05:00 PM (CET)
AI Security Masters: Security in the Pace of AI: From Threat to Force MultiplierTue 17 Nov 2026 @ 11:00 AM (EST)
Under the Hood: Check Point SASE | Troubleshooting Like a ProTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseTue 17 Nov 2026 @ 08:30 AM (EST)
Bogota Breakfast & Hack: IA bajo control y ataques en vivo con Workspace SecurityAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION