- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Scenario
Notebook With client Endpoint Security --> Checkpoint Quantum Spark 1530 Appliance
Notebook connect to Checkpoint all fine, he can see the entire LAN network, i used office mode. All fine.
What i need is a bidirectional comunication. Pc on lan network to have access to one port listening on notebook.
It's possible ?
Thank's
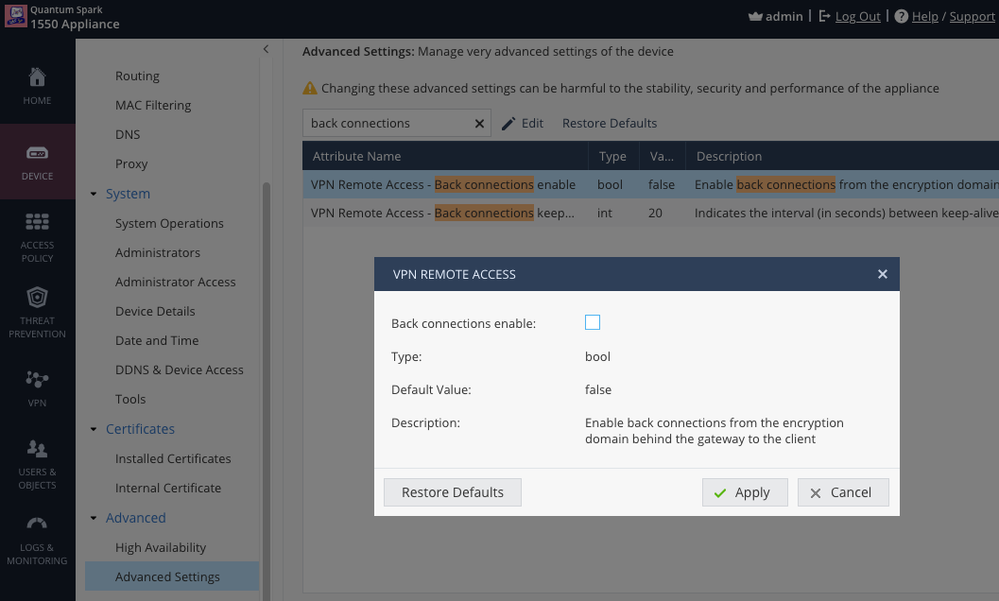
You need to additionally enable Back Connections in Advanced Settings:
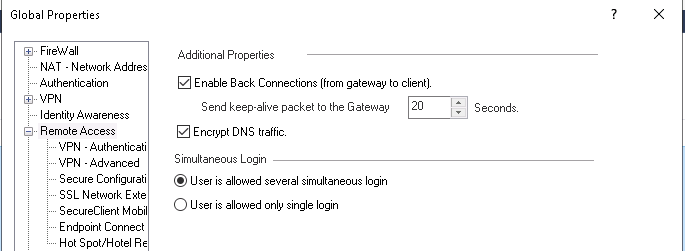
For a centrally managed SMB appliance (or for non-SMB appliances), this is the correct setting in Global Properties to allow connections initiated from the LAN to Remote Access VPN clients:
You can pit Office Mode IP for a specific user, and then yes, you can do what you need
OK i put in office mode, i edited file ipassignement.conf and when i connect i receive correct ip address. Do i need to make something other because still not working.
Sorry for newbie question i'm following the user manual.
You need to additionally enable Back Connections in Advanced Settings:
Hi, first thank for your answer.
Yes i had already create outgoing roule, i attach screenshot. I tried also with Any instead of Lan Networks.
However i don't rebooted checkpoint after put new ipaggnignement,conf
All work fine user always receive the same ip.
Maybe something wrong on file ?
I had put
##############################################################################################
### Gateway Type IP Address User Name ###
### ============= ===== ======================================== =======================###
##############################################################################################
*, 172.16.10.5, tamponi
Thank's i tred to activate but nothing.
1) Office per mode use ok
2) Outgoing roule plicy to allow lan to vpn remote access.
3) Enabled back conneccion
i try to enable anti-spoofing on vpn remote access but nothing.
Can you share the policy rule you've created?
Ok.
In the policy, instead of using the Remote Access object, try to use the Office Mode IP/Network.
OK i solved the issue. My configuration work like screenshot.
I don't know why i can't ping my remote notebook also if windows firewall it's down but for example i can access the shared folder.
The real missing puzzle for me it's what you suggest me and i report like solutions, the allow back connection.
The Remote Access object could not be mapping the network correctly, but I'm glad you've worked it out.
Can we move this to Quantum Spark ?
Why?
If this were posted somewhere else, that's probably where I'd move it.
However, this deals with both topics, so I'm inclined to leave it where it is. 🙂
For a centrally managed SMB appliance (or for non-SMB appliances), this is the correct setting in Global Properties to allow connections initiated from the LAN to Remote Access VPN clients:

Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 1 | |
| 1 | |
| 1 | |
| 1 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaThu 26 Nov 2026 @ 10:00 AM (CET)
The Cloud Architects Series: Cloud Security State in 2026 – Lessons Learned and a Look AheadWed 02 Dec 2026 @ 02:00 PM (CET)
E-Mail-Agent-Hijacking: E-Mail-Sicherheit im Zeitalter der KI neu überdenkenWed 02 Dec 2026 @ 02:00 PM (GMT)
Why Email Agent Hijacking Marks the End of Post-Delivery Email SecurityWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 02:00 PM (CET)
E-Mail-Agent-Hijacking: E-Mail-Sicherheit im Zeitalter der KI neu überdenkenWed 02 Dec 2026 @ 02:00 PM (GMT)
Why Email Agent Hijacking Marks the End of Post-Delivery Email SecurityWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseWed 02 Dec 2026 @ 11:00 AM (PST)
Why Email Agent Hijacking Marks the End of Post-Delivery Email SecurityAbout CheckMates
Learn Check Point
Advanced Learning

WE SECURE YOUR AI TRANSFORMATION