- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hi All,
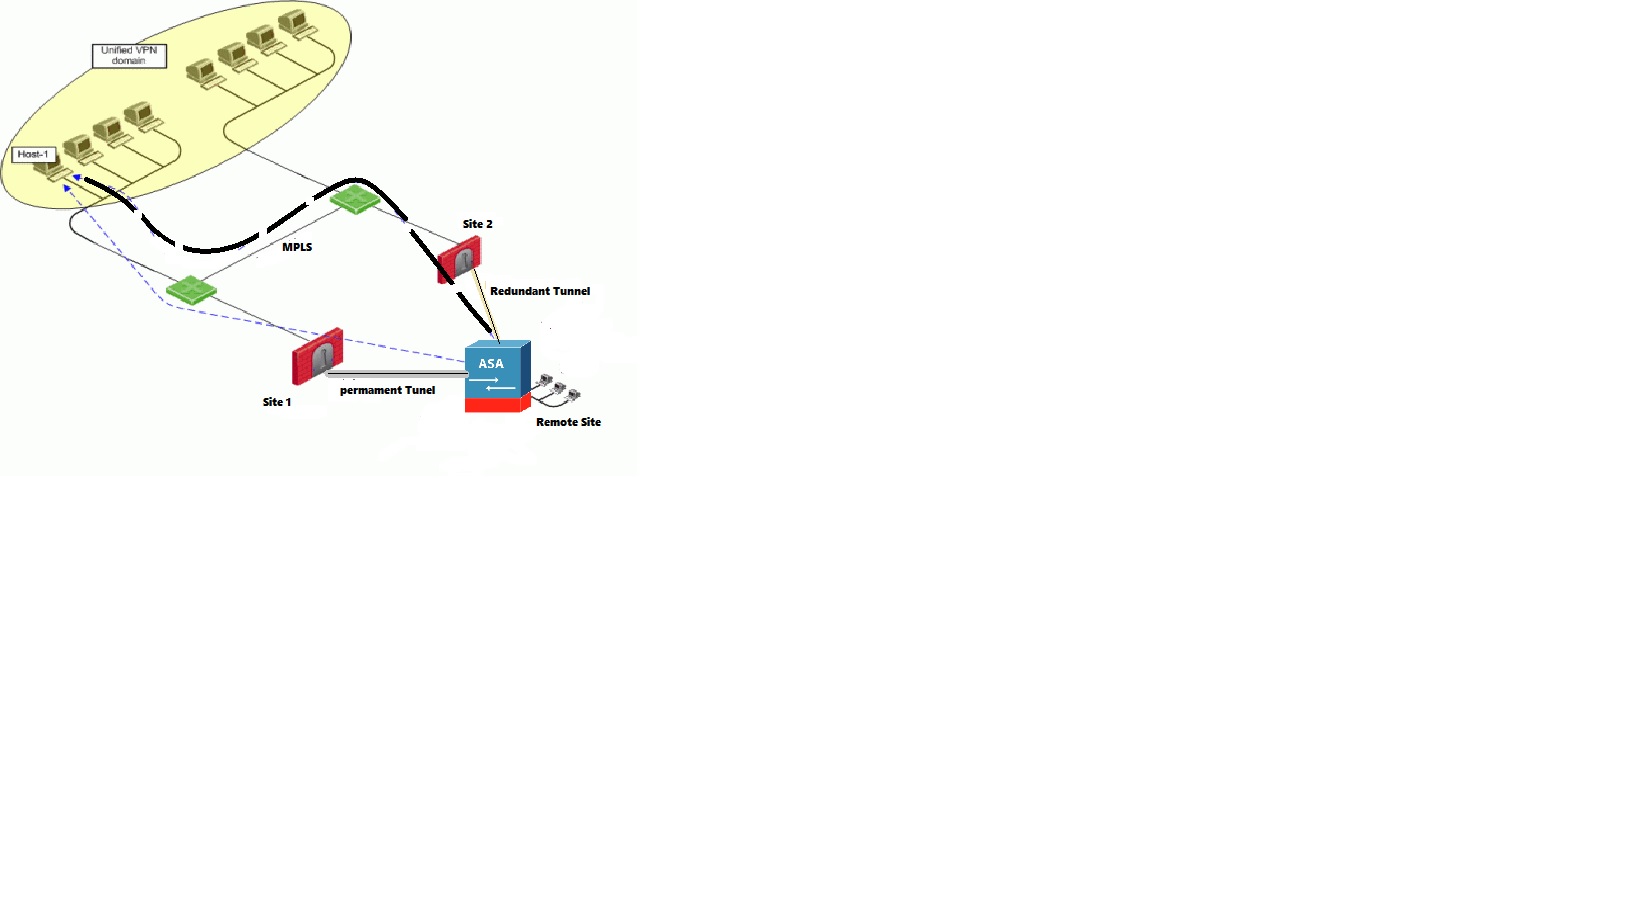
As shown in the diagram, i have a requirement. Site 1 is connected with Remote Site (marked as permanent tunnel) this is working and up. now i need to configure Redundant Tunnel between Site 2 and Remote Site. as per my understanding MEP will work only with checkpoint. what other solution can be provide here and how do i define priority and route.
I just can see a Cisco ASA here - where is which Version/type of CP VPN GW you want a solution for ?
checkpoint at both site is managed by same management
Version
CP -77.30
ASA-9.x
CP -77.30
ASA-9.x
So both CPs have only one VPN tunnel each, but ASA has one main (permanent) and one redundant VPN tunnel - please correct me if i am wrong. So all redundancy configuration must be done on ASA - maybe a Cisco Forum would be more appropriate for this question
.
No,traffic initiator is CP. there is only one VPN tunnel between Site 1 and Remote ASA site. i need to implement a new backup tunnel from site 2 to Remote ASA. in this setup primary tunnel is Site1 to remote ASA. in case of any failure at site 1, the traffic should pass through Site 2 to Remote ASA.
Route Based VPN could be adequate to this scenario, using Numbered VTI. See this discussion:
https://community.checkpoint.com/thread/6641-how-can-i-setup-a-primary-and-backup-s2s-vpn-tunnels
If heading down the route-based VPN path, R80.10 or later on the gateway is strongly recommended. Prior to R80.10 the utilization of the route-based VPN feature required CoreXL to be disabled (i.e. only one Firewall Worker/kernel instance for all traffic processing).
--
Second Edition of my "Max Power" Firewall Book
Now Available at http://www.maxpowerfirewalls.com
if checkpoint gw protecting the same networks and if you don't want to use route based vpn you can try to apply NAT on one of the checkpoint gateways to present different networks for the ASA as encryption domain.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 9 | |
| 9 | |
| 7 | |
| 6 | |
| 6 | |
| 6 | |
| 5 | |
| 4 | |
| 3 | |
| 3 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION