- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Identity and Trust?
11 November @ 5pm CET / 11am EST
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
What’s New in Agentic Network Orchestration
AI Security Masters
LGTM: Bypassing an LLM Build Gate
When Prompt Injection Fails
CheckMates Go:
Fun Ding
I have a near term deployment of new firewalls and management system, so I was wondering when R80.40 GA might be available. Any news?
We closed the release but as we release by quality and not by date, therefore the release may still take more days (pending more EA feedback).
i would certainly hope to have it released in the next days but as said, if we find blockers we may delays
important reminder,...:
In the new process of releasing frequent releases (started in r80.30) when we do release, we recommend it for those that need the new features now, We then take few more weeks to gain confidence (after more deployments), usually release also a jumbo ... and then we recommend it for wider/default use.
So ... If you do not plan to leverage new content of r80.40 in day one, use r80.30 as its safe and widely used. If you do plan to leverage the new capabilities of r80.40 immediately, you can wait a bit more.
We closed the release but as we release by quality and not by date, therefore the release may still take more days (pending more EA feedback).
i would certainly hope to have it released in the next days but as said, if we find blockers we may delays
important reminder,...:
In the new process of releasing frequent releases (started in r80.30) when we do release, we recommend it for those that need the new features now, We then take few more weeks to gain confidence (after more deployments), usually release also a jumbo ... and then we recommend it for wider/default use.
So ... If you do not plan to leverage new content of r80.40 in day one, use r80.30 as its safe and widely used. If you do plan to leverage the new capabilities of r80.40 immediately, you can wait a bit more.
Release notes:
"SCP and SFTP file transfers can be scanned using SSH Deep Packet Inspection."
don't see anything regarding this in the SmartConsole.
Any hints?
best regards
Vincent
@VincentBacher - In order to enable SSH inspection you need to follow Threat Prevention R80.40 Administration guide,
under "SSH Deep Packet Inspection" section.
|
cpssh_config ion |
|
fw fetch local |
You meant section in the admin guide, correct?
In SmartConsole there's nothing to see?
Correct in the admin guide, not in smart console.
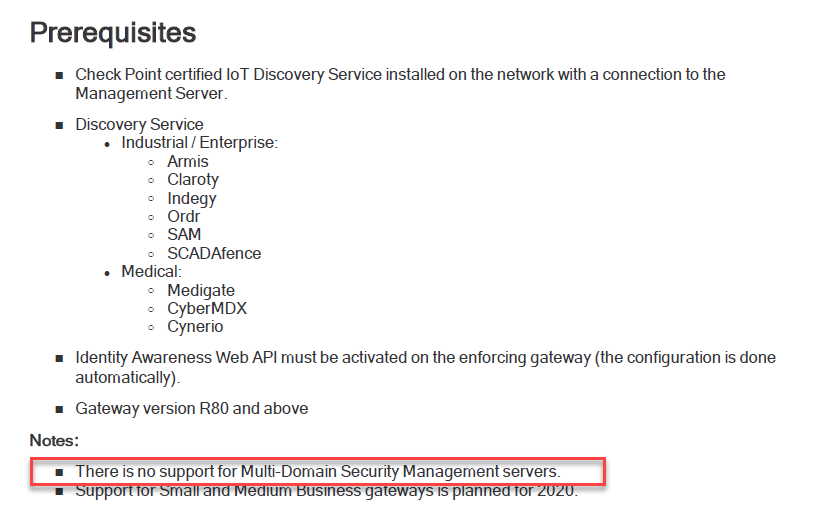
@Ilya_Yusupov , Question relating to IoT support in R80.40:
right now it says MDM is not supported:
any rough idea then it will be published for MDM too?
Thanks! K
Hi,
Indeed, IoT controller is not supported with MDM.
This is planned to be fixed down the road,
We are looking for relevant opportunities, IoT controller and MDM, and if there are such, we will promote the fix
Amir
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 32 | |
| 10 | |
| 9 | |
| 9 | |
| 7 | |
| 5 | |
| 4 | |
| 4 | |
| 3 | |
| 3 |
Tue 03 Nov 2026 @ 06:00 PM (CET)
Under the Hood: How to Secure Agentic AI on AWS with Check PointTue 10 Nov 2026 @ 06:00 PM (IST)
Under the Hood: Introducing Check Point Cloud Firewall as a ServiceTue 10 Nov 2026 @ 08:00 PM (IST)
Check Point Mobile Security | Extending Zero Trust with NetskopeTue 03 Nov 2026 @ 06:00 PM (CET)
Under the Hood: How to Secure Agentic AI on AWS with Check PointTue 10 Nov 2026 @ 06:00 PM (IST)
Under the Hood: Introducing Check Point Cloud Firewall as a ServiceTue 10 Nov 2026 @ 08:00 PM (IST)
Check Point Mobile Security | Extending Zero Trust with NetskopeAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION