- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Tenable Scan will dynamically open up various ports "SMTP Server Non-standard Port Detection" only on 2 out of the 16 gateways in our production environment. So far it has only happened on the secondaries.
It does this everytime even after a fresh reboot of the gateway.
All GW's are running R77.30 Jumbo 286. Anyone ever heard of this. We had a case opened a few months back but got no where. Any advice would be greatly appreciated.
Thanks -pat
Check Point gateways have userpsace processes that listen on random high ports.
The primary reason for this is to fold specific types of traffic into the processes that perform different types of content inspection.
It's entirely possible that, if you haven't implemented a stealth rule in your rulebase properly, that something like a Tenable may pick up one of these random high ports.
Thanks I appreciate the explanation and replies. We would like to implement an over scan rule / tighten up our stealth rule by not allowing any scans such as implementing SK110873 but so far We have been not successful in getting that change passed.
thanks again
-pat
Dameon,
How doe the stealth rule works in situations when GW has to be directly accessible by internal hosts, (i.e. captive portal, user check portal, platform portal, etc.)?
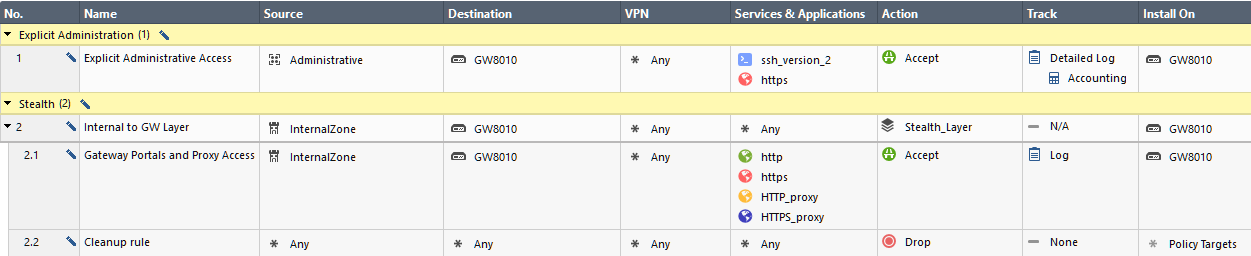
You would create the various required access rules prior to the Stealth Rule.
In fact, this may be a situation where a Policy Layer might be useful in R80.10+.
Something like this?

Yeah like that
Hi , I also had this particular findings after a nessus (tenable) scan. Di you already find out the solution to eliminate the findings? thank you very much
Hi,
Got the same behaviour on R80.20 gateway (with Management and gw on the same hardware). The question is why do they have those SMTP ports opened?
Even if "The primary reason for this is to fold specific types of traffic into the processes that perform different types of content inspection." I don't understand why those ports are open.
Of course a Stealth Rules will mitigate the impact... but from a Security point of view, those are still open
Open port does not represent a security risk. The answer is already given: in case of content inspection, the traffic should be folded for inspection
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 9 | |
| 9 | |
| 7 | |
| 6 | |
| 6 | |
| 6 | |
| 5 | |
| 4 | |
| 3 | |
| 3 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION