- Products
- Learn
- Local User Groups
- Partners
- More

Scaling Check Point Automation with Arodonata
7 October @ 5pm CET / 11am EDT
What's New in Check Point SASE
The State of Ransomware Q2 2026:
This Quarter's Trends, and Their Impact on Your Defenses
AI Security Masters
Implementing the AI Security Trifecta
CheckMates Go:
Half is Not Enough
Hi,
We have firewall enabled with identity awareness blade. It collects identity from identity collector, which it makes communication to our internal domain controllers for fetching identities and forward to gateway.
We got requirement from user to add specific rule where user can access vendor link from any network (corporate IP only), any user but from particular server.
We created access rule for this requirement. However, its not working. If you suggest any troubleshooting steps, it would be much appreciated.
Could see traffic getting dropped in firewall when user tries to telnet to vendor portal from the allowed particular server/machine.
Let’s start with exactly what you created in the rulebase versus what got logged when the user tried to access.
Might help to know version/JHF level as well.
Also maybe check in the CLI of the gateway if it’s associating the right roles using pdp monitor user username.
I have created access role in source column like below
Network - Any
Users - Any
Machine - Specific Security Group created in AD (This group contains machines/servers not any user ID's)
Destination - Vendor Website IP address
Gateway version is R80.40/ JHF Accumulator take 91
When i run pdp monitor user username, I am not getting this access role but getting other access roles. Working fine If I create access role with any network, specific users and any machine (Not for this scenario for others i am saying).
Why with specific machine is not working?
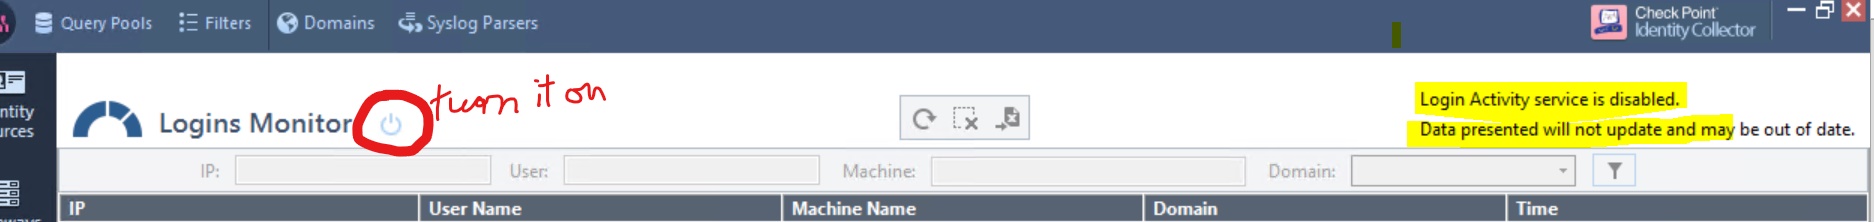
Also, please let me know how can i make this service in running state and see logs in Login Monitor section of Identity collectors. Please see attached screenshot for details.
Logins Monitor might be this: https://supportcenter.checkpoint.com/supportcenter/portal?eventSubmit_doGoviewsolutiondetails=&solut...
We have added Domain Controller as identity source manually but still having same issues. 'Is Forwarded Log Event Collector' was already in disabled state. This sk166076 doesn't resolve my issue. Do you know that we need to start any windows services for this to work?
I don't think I quite understand the requirement here.
Do you mean that the "vendor link"is a URL and accessed via browser?
In that case is it safe to assume that the "particular server"is a proxy?
So users would connect to proxy and proxy would make connection to the vendor?
How the users connect to this particular server RDP/SSH? Why don't you just create a rule with this server as IP, not by access role?
Important is the status in the "Identity Sources" tab, is your configured AD server listed green?
And if you see a higher number than 0 in column "Total Events Received" you are receiving events 🙂
On the identity collector you have great log file "C:\Windows\Temp\ia.log"
To have the events in the UI, you need to turn on the "Loging Monitor".
Please click on the small grey "power button" behind the "Loging Monitor" text and you will see the monitoring events.
Your screenshot is showing that the "Logins Monitor" is disabled.
By the way i think the question from Martin Tzvetanov is a valid one.
If any user should have access and you want to allow the system itself as source,
why not creating a simple rule for allowing "YourServerIP" to vendors Website IP?
But sometimes the destination IP of a website could change,
so you could think about using FQDN object as destination instead of IP.
Important is the status in the "Identity Sources" tab, is your configured AD server listed green?
And if you see a higher number than 0 in column "Total Events Received" you are receiving events 🙂
On the identity collector you have great log file "C:\Windows\Temp\ia.log"
To have the events in the UI, you need to turn on the "Loging Monitor".
Please click on the small grey "power button" behind the "Loging Monitor" text and you will see the monitoring events.
Your screenshot is showing that the "Logins Monitor" is disabled.
By the way i think the question from Martin Tzvetanov is a valid one.
If any user should have access and you want to allow the system itself as source,
why not creating a simple rule for allowing "YourServerIP" to vendors Website IP?
But sometimes the destination IP of a website could change,
so you could think about using FQDN object as destination instead of IP.
Important is the status in the "Identity Sources" tab, is your configured AD server listed green?
And if you see a higher number than 0 in column "Total Events Received" you are receiving events 🙂
On the identity collector you have great log file "C:\Windows\Temp\ia.log"
To have the events in the UI, you need to turn on the "Loging Monitor".
Please click on the small grey "power button" behind the "Loging Monitor" text and you will see the monitoring events.
Your screenshot is showing that the "Logins Monitor" is disabled.
By the way i think the question from Martin Tzvetanov is a valid one.
If any user should have access and you want to allow the system itself as source,
why not creating a simple rule for allowing "YourServerIP" to vendors Website IP?
But sometimes the destination IP of a website could change,
so you could think about using FQDN object as destination instead of IP.