- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Dear Team,
In preset we have multiple LDAP account Unit and we want delete it and create single unit with multiple AD sever with setting of " User Directory" .
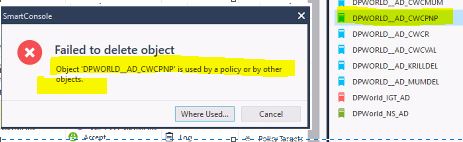
We have Achieved it but unable to delete old LDAP account unit. it is showing Error" Object is Used by policy or by other object". Please find attached error screen shot.
Where as we removed it from all other object and policy. we have check with it "View Details" noting is showing.
How can i delete this LDAP account unit?
Check Point Manager : R81 take 23
Gateway: R81 take 13
Hello Tobias_Moritz,
Thank You...!
It worked. I have checked in GuiDBedit Database and that object "ad_group_IT_Users" was there. I have verify & delete this object.
After this object deletion, i am able to delete LDAP account unit that belongs to this object.
@surajshinde right click on the LDAP-AccountUnit and use „where used“. Then you know from where to have to remove the object.
As the messages states, objectors in use in another configuration. There it should be removed before deleting.
I guess you have an Access Role in your database which still references to this AD group object while this AD group object references to the LDAP Account Unit you want to delete. Use CPMI (GuiDBedit for example) to search for this object (ad_group_IT_Users).
When you found the Access Role(s) which use(s) this ad group object, remove the ad group from this Access Role object(s) using SmartConsole. After that (at least after publish and install database), try to remove the LDAP Account unit again.
If it is still saying it is in use, then use GuiDBedit to search for other references for the LDAP Account Unit, SmartConsole is not able to find with its where-used feature.
The main problem here it, that SmartConsoles where-used feature cannot display all references of all objects. CPMI usually can.
Hello Tobias_Moritz,
Thank You...!
It worked. I have checked in GuiDBedit Database and that object "ad_group_IT_Users" was there. I have verify & delete this object.
After this object deletion, i am able to delete LDAP account unit that belongs to this object.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 28 | |
| 8 | |
| 5 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 4 | |
| 3 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION