- Products
- Learn
- Local User Groups
- Partners
- More

Scaling Check Point Automation with Arodonata
7 October @ 5pm CET / 11am EDT
AI Security Masters
LGTM: Bypassing an LLM Build Gate
When Prompt Injection Fails
What's New in Check Point SASE
The State of Ransomware Q2 2026:
This Quarter's Trends, and Their Impact on Your Defenses
CheckMates Go:
Half is Not Enough
Hi guys,
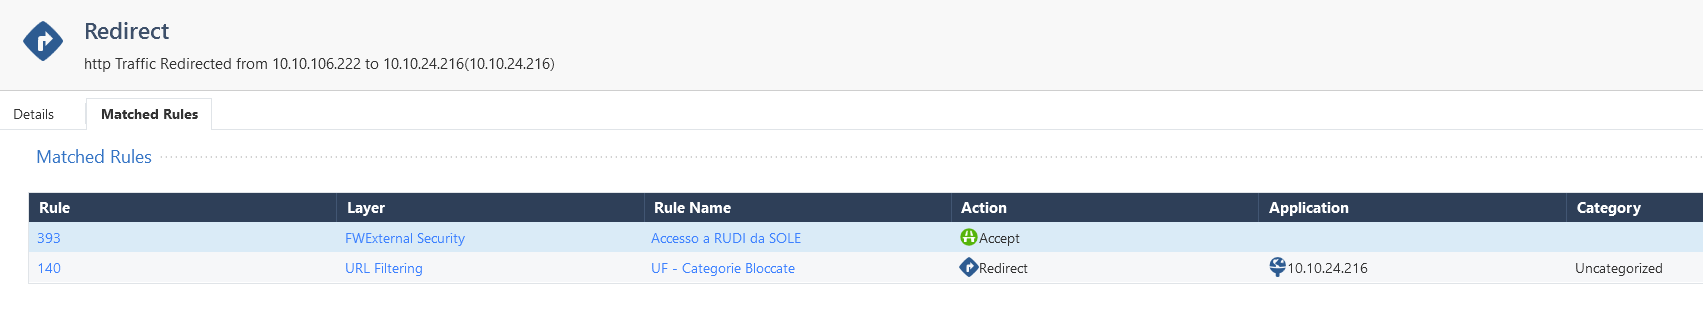
specific traffic with a private ip as destination, is matching a rule with the "Internet" object in destination field. This traffic don't pass trough External/DMZ interfaces.
Do you have any ideas?
Thanks and best regards
Francesco
Version/JHF level?
What is the precise rule (screenshot helpful)?
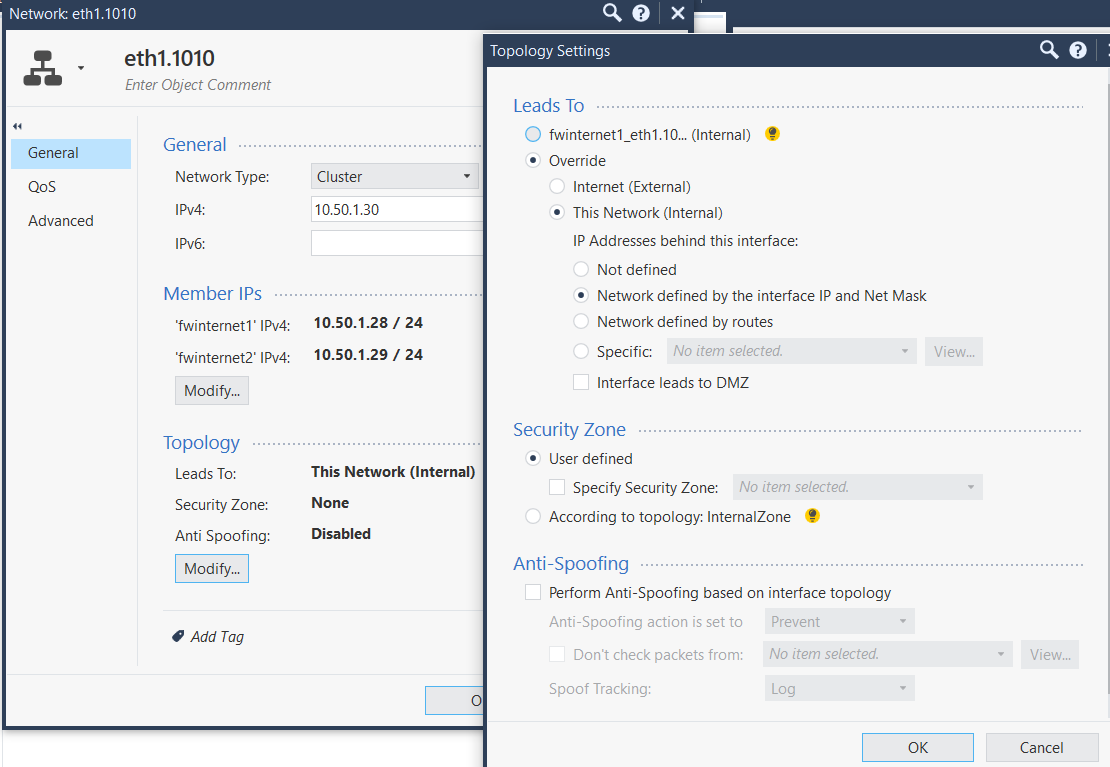
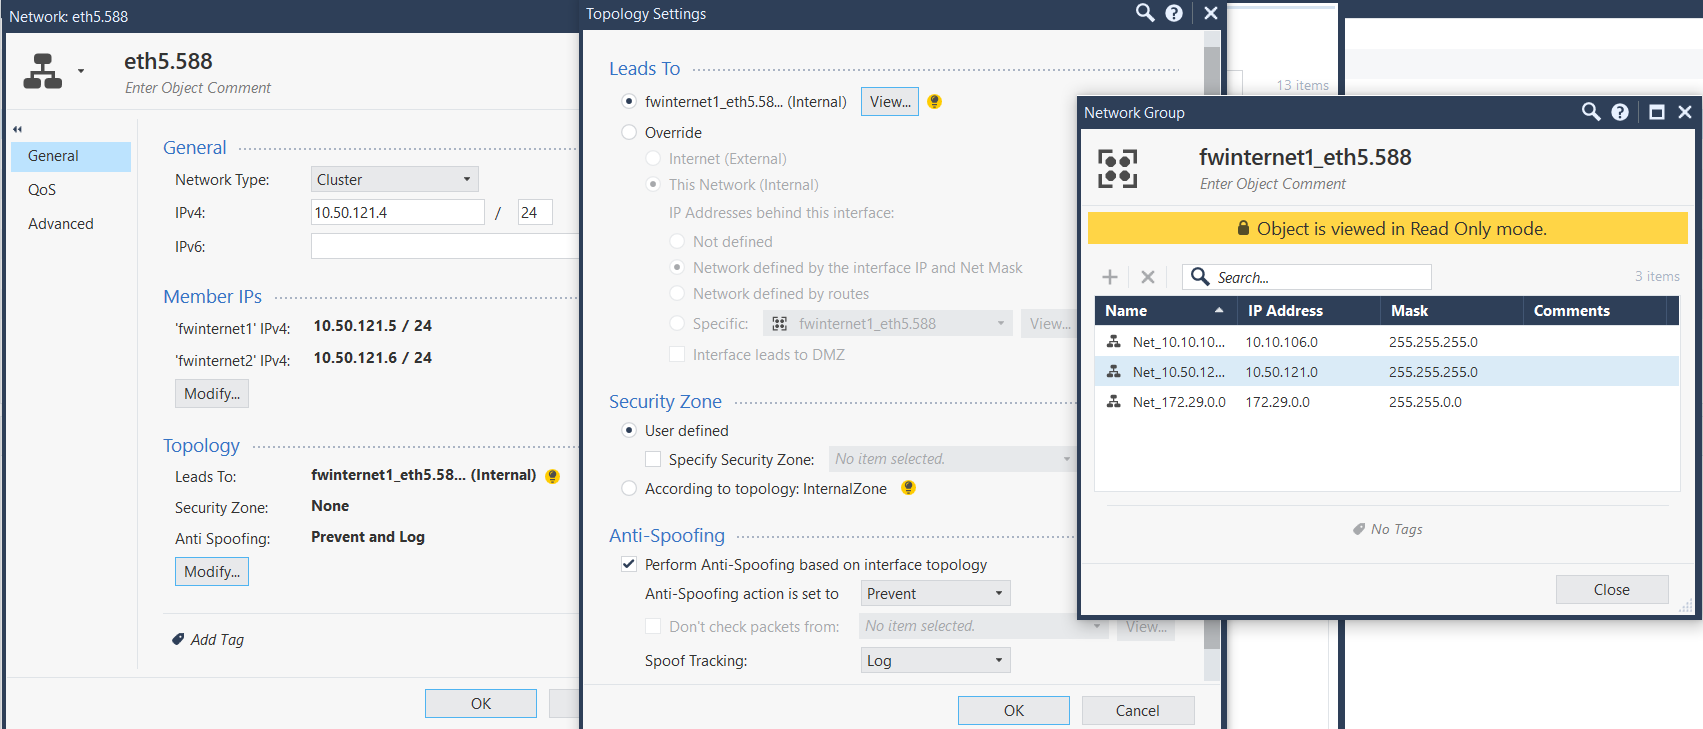
What interfaces does the traffic pass through and how is the topology defined on the relevant interfaces?
Quoting from sk64543:
"Internet" means "include all traffic directed to External or DMZ according to gateway topology".
Internet object, unlike many people expect, do not represent all routable Internet addresses. Instead, it is a sum if all networks that GW does not have defined as internal.
Check your internal networks in question are defined in GW topology. If this is not the case, system is working as designed.
Hi,
Traffic is passing through interfaces defined as "This network" or internal.
So, this traffic should not match policies configured with Internet object in destination field.
Thanks
Francesco
We cannot establish that, since you did not post your GW topology. If you are 100% positive that is the case, raise a TAC support request.
Already said above, open a service request.
Yeah, give us some more info. For example if it is a private IP but in a peer VPN domain it will be considered external (Internet).
It's not a VPN traffic.
I attached screenshots in the previous reply.
Thanks and Best Regards
Francesco
Hi @FWNinja ,
according to log detail screen shot you matched on Rule 140 but you put screen shot of rule 142.
can you share rule 140?
Thanks,
Ilya
Hi,
the rule is the same. The customer added 2 rules before and the rule 140 become 142.
Thanks
Francesco
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 34 | |
| 8 | |
| 6 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 4 | |
| 3 |
Thu 01 Oct 2026 @ 05:00 PM (CEST)
Under the Hood: Check Point WAF | Preventing minus-zero-day attacksTue 06 Oct 2026 @ 12:00 PM (ACDT)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus APACTue 06 Oct 2026 @ 03:00 PM (CEST)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus EMEAThu 01 Oct 2026 @ 05:00 PM (CEST)
Under the Hood: Check Point WAF | Preventing minus-zero-day attacksTue 06 Oct 2026 @ 12:00 PM (ACDT)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus APACTue 06 Oct 2026 @ 03:00 PM (CEST)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus EMEATue 06 Oct 2026 @ 02:00 PM (EDT)
Rethinking Network Security for the AI Era : Session 2 - From User, to Branch and Campus AMERAbout CheckMates
Learn Check Point
Advanced Learning
YOU DESERVE THE BEST SECURITY