- Products
- Learn
- Local User Groups
- Partners
- More

Scaling Check Point Automation with Arodonata
7 October @ 5pm CET / 11am EDT
What's New in Check Point SASE
The State of Ransomware Q2 2026:
This Quarter's Trends, and Their Impact on Your Defenses
AI Security Masters
Implementing the AI Security Trifecta
CheckMates Go:
Half is Not Enough
Hello all,
I'm happy to inform you that we added a new feature to the log exporter - the ability to filter logs.
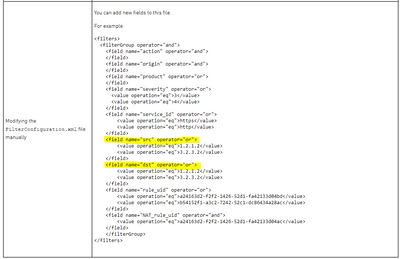
Starting today, you will be able to configure which logs will exported, based on fields and values, including complex statements.
More information, including basic and advanced filtering instructions, can be found in SK122323.
If you have any question or comment, let me know.
Thanks!
Dan.
What format are you using as part of Log Exporter configuration?
target-port: 12010
protocol: tcp
format: splunk
read-mode: semi-unified
export-link: false
export-attachment-link: false
export-attachment-ids: Found
Please send my your FilterConfiguration.xml file to my email and we will take it offline from there.
Hi,
I know this is an old topic, but does anything changed in that matter? Can you write filter based on subnets?
Greetings,
Mariusz
According to the SK it looks to be supported:
The issue, I believe, is that you would have to list each IP address in the subnet.
Or it is possible to reference an entire subnet or range of addresses, but the syntax for doing so is not documented.
Unfortunnatly you're right. I've opened SR Question with TAC and received answer:
"It can not cover a range and it needs to be a value from log, not without putting a new line for every ip in that range we can do this"
The case is I'd like to filter out several /16 networks. If I put just one net like that it makse 65k records and CPU cores on log server associated with log exporter are 100%, and very little logs are exported.
I would work with your local Check Point office on an RFE for this.
Hello friends,
I have a 1450 appliance Version R77.20.85 (990172755)
How can I get the configuracion log exporter for this appliance? I see that sk 122323 is for R77.30 and above.
Thanks
to be clear:
Log exporter is running on the log server/management and it is agnostic to which GW generated the data.
Ok, thanks a lot.
Nice day.
Thanks a lot.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 31 | |
| 6 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 4 | |
| 3 | |
| 3 |
Wed 23 Sep 2026 @ 06:00 PM (EDT)
Santo Domingo: Workspace Security and SASE Live: Protección Total del Usuario Email, Endpoint y SASEMon 28 Sep 2026 @ 03:00 PM (CEST)
La nouvelle réalité des attaques DDoS: autonomie, échelle et avenir de la défenseThu 01 Oct 2026 @ 05:00 PM (CEST)
Under the Hood: Check Point WAF | Preventing minus-zero-day attacksMon 28 Sep 2026 @ 03:00 PM (CEST)
La nouvelle réalité des attaques DDoS: autonomie, échelle et avenir de la défenseThu 01 Oct 2026 @ 05:00 PM (CEST)
Under the Hood: Check Point WAF | Preventing minus-zero-day attacksWed 23 Sep 2026 @ 06:00 PM (EDT)
Santo Domingo: Workspace Security and SASE Live: Protección Total del Usuario Email, Endpoint y SASEAbout CheckMates
Learn Check Point
Advanced Learning
YOU DESERVE THE BEST SECURITY