- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hi guys,
I know that in theory, R80.20 should support traditional VPN mode but that it doesn't support the option to convert traditional to simplified.
However, after exporting the database to R80.20 with the instructions outlined in this link (Installation and Upgrade Guide R80.20.M1 ), I am then getting the following output:
Title: Firewall policies with Traditional VPN mode
-----
* Description:
Traditional mode refers to legacy VPN policy, which was replaced by Simplified VPN (first introduced at 2002 in version NG FP3). Please change the below policies by using one of the methods:
If you have a specific case in which you have to use Traditional VPN mode, please contact Check Point support.
Could anybody be able to provide an explanation for this please?
Many thanks.
Traditional VPN mode is not supported anymore.
Just curious, but why would you like to use traditional mode VPN? I don't remember having seen that in years...
We have one customer with around 70-80 VPN with all kinds of third parties that are setup as Tradintional a long time ago. This is very hard to convert to simplified mode. Most of these VPN's are used for EDI traffic and have a high need for uptime. If we were to replace this environment, it would be a per VPN migration, a lot of work and a lot of risks.
To add a little color:
Hi Richard,
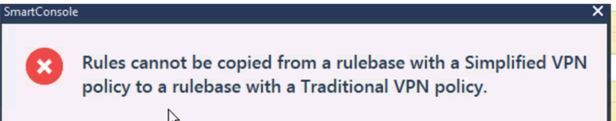
... and your are right 🙂 Just today having a customer trying to copy the rules from traditional to a new simplified policy, and got an error
and this under actual JHF and R80.20 so seems to be a bug here, because the mentioned copy direction is wrong too
I think this will end in a case 🙂
And sory for the late reply too. But I think it's ok for All who searching in the threads to find ideas 🙂
Hey Gera,
an did you find a solution to copy rules from one to the other ?
Thank you all very much.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 28 | |
| 8 | |
| 7 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 4 | |
| 3 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION