- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Identity and Trust?
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hello experts,
I'm using checkpoint R81 with https inspection blade.
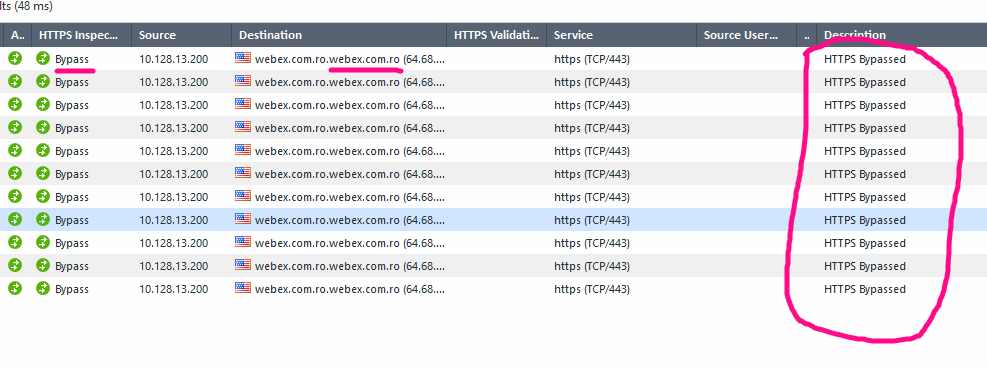
I have a host , and I want bypass when it access site webex.com. I made a rule for it, and below logs is saying that it is bypassed.
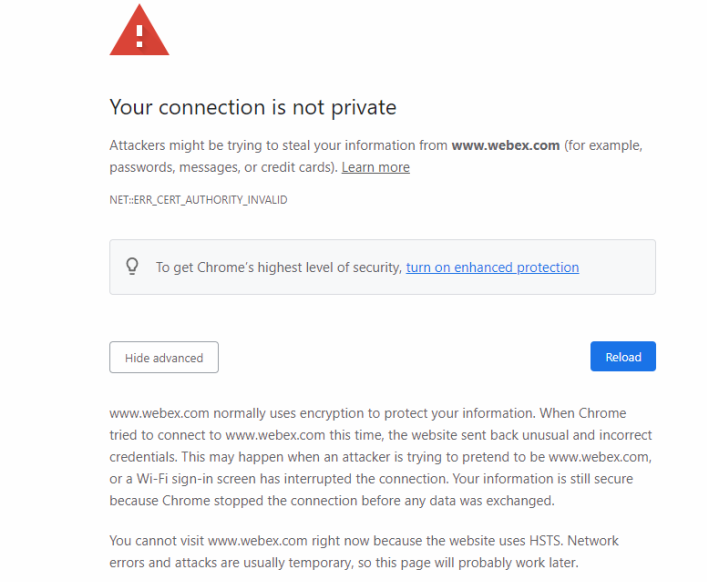
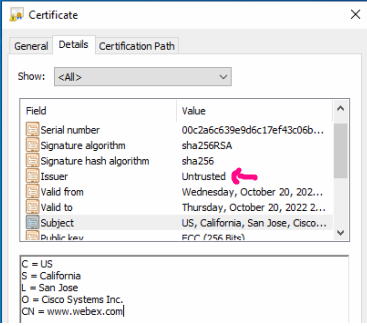
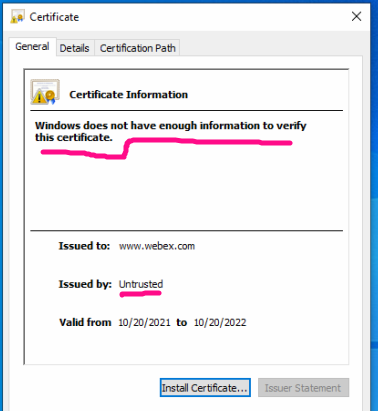
But when this host goes to webex.com by chrome or Edge, it says that connection is not secure and certificate is showing wrong like this:
Please help me, thanks you!!!
sk106996: "HTTP Strict Transport Security" (HSTS) header handling in HTTPS Inspection
Can you please show how your bypass rule looks like?
Hi Mr _val_,
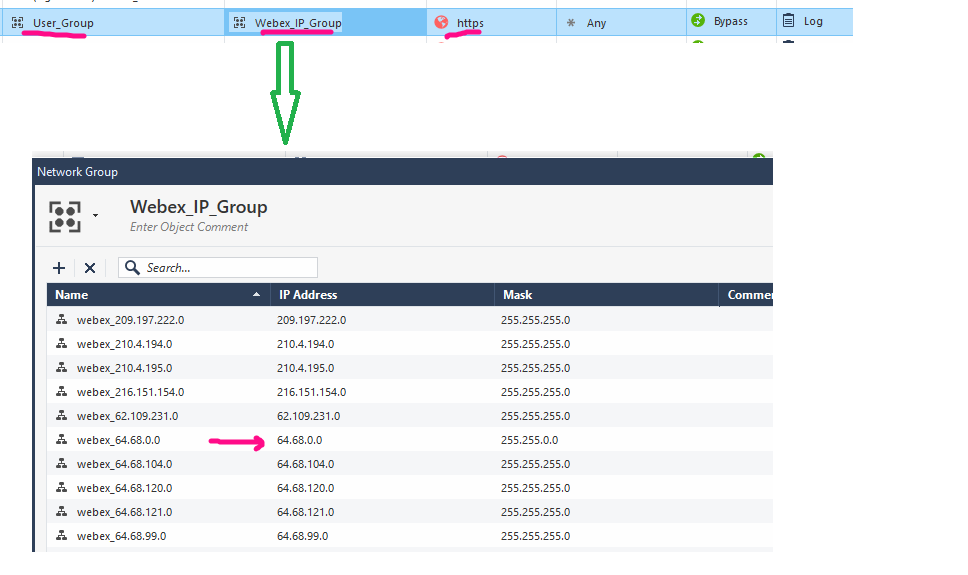
Here is my rule (I bypass by using IP-range of webex
Also, why a user group as a source?
Hey,
Did you checked the certificate you get for that page from outside your network, I see the same error considering that the SSL certificate is not covering the https://webex.com.ro.webex.com.ro (see below)
Thank you,
Hi mr Sorin,
On my host, I type only https://webex.com, dont know why checkpoint log say webex.com.ro.webex.com.ro
I doubt maybe firewall still has intervention even I set bybass for webex-ip.
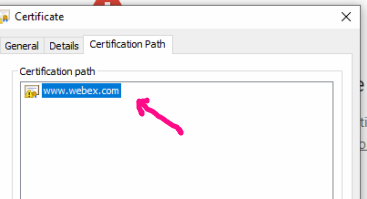
Here is cert of webex.com , which my host is seeing:
So you can see that the cert that is presented is not trusted , therefore where is the CheckPoint HTTPS Inspection culprit ?!?!?!
As for the WebEx.com, it might do some redirects and will get to the 64.68.121.205 (that is webex.com.ro.webex.com.ro ) , you should run some HTTP network traces ( in Chrome do an F12 and choose Network Tab [mark Preserve Log] and you should see the 3xx redirects if there are any) .
Still I'm not getting your question, you state that you have HTTPS Inspection on the GW and on webex.com you get some browser SSL errors/alerts - where is CheckPoint part involved in all this ?
You have a bypass rule that it happens - is clearly showed/logged - and if the HTTPS would Inspect, you should see your internal Certificate generated on-the-fly from the GW .
So I didn't catch your CKP problem except the HSTS error - and that is not tight to CKP in my opinion.
Thank you,
Were you able to solve the issue? I'm having the same problem.
Not a good rule. Use a Webex Updatable object instead, please
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 29 | |
| 14 | |
| 7 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 3 | |
| 3 | |
| 3 |
Tue 17 Nov 2026 @ 08:30 AM (EST)
Bogota Breakfast & Hack: IA bajo control y ataques en vivo con Workspace SecurityTue 17 Nov 2026 @ 05:00 PM (CET)
AI Security Masters: Security in the Pace of AI: From Threat to Force MultiplierTue 17 Nov 2026 @ 11:00 AM (EST)
Under the Hood: Check Point SASE | Troubleshooting Like a ProTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaTue 17 Nov 2026 @ 05:00 PM (CET)
AI Security Masters: Security in the Pace of AI: From Threat to Force MultiplierTue 17 Nov 2026 @ 11:00 AM (EST)
Under the Hood: Check Point SASE | Troubleshooting Like a ProTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseTue 17 Nov 2026 @ 08:30 AM (EST)
Bogota Breakfast & Hack: IA bajo control y ataques en vivo con Workspace SecurityAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION