- Products
- Learn
- Local User Groups
- Partners
- More
What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hi all,
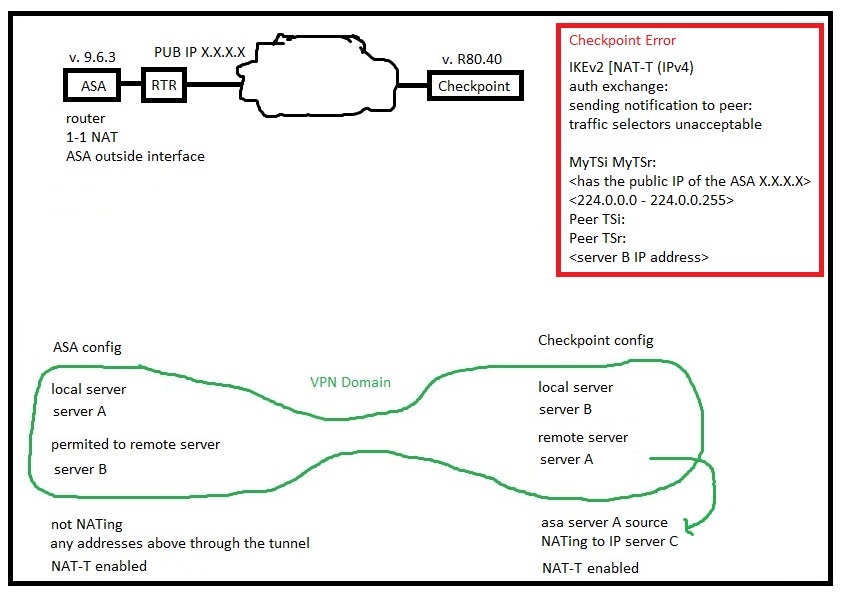
Have a 5800 R80.40 to a ASA 9.6 VPN trying to get up.
Scenario is,
ASA LAN server A to Checkpoint LAN server B
On the checkpoint, ASA LAN server A source is being translated to server C IP. server B gets no nat/original.
Since this is transparent to the ASA, on the ASA the no nat rule says server A and B get no nat.
When initiating traffic on the Cisco side, the ASA debugs makes it seem Phase 1 is ok as far as the crypto and PSK.
On the Cisco debug shows that the correct DH group has been negotiated, NAT-T is in use 4500, PSK has been sent and ESP encapsulation is going on,
Then the ASA sends the traffic selector for the correct source ( server A ) to destination ( server B ) and resends a few times and times out.
On the Checkpoint side, it shows as UP Phase 1, but shows this error.
IKEv2 [NAT-T (IPv4)
auth exchange: sending notification to peer: traffic selectors unacceptable
MyTSi MyTSr:
<has the public IP of the ASA>
<224.0.0.0 - 224.0.0.255>
Peer TSi:
Peer TSr:
<server B IP address>
Do not why the Checkpoint is picking the " public outside " interface IP of the ASA firewall.
Does anyone have any ideas?
See sk108600: VPN Site-to-Site with 3rd party and sk157473: Site to Site using IKEv2 fails with "None of the traffic selectors match the conection"
Hey, G_W_Albrecht, thank you, it helped me.
I've just changed the Tunnel Mode of the VPN Community from"One Tunnel Per Subnet Pair" to "One Tunnel Per Gateway Pair" and all worked, thank you again for posting the sk157473
Best.
See sk108600: VPN Site-to-Site with 3rd party and sk157473: Site to Site using IKEv2 fails with "None of the traffic selectors match the conection"
Thanks for the links. I had read them before, but didn't see anything exact to my scenario, but will try a few of the things in them.
I had read an article a while that mentioned the traffic selection on the Checkpoint side, being the ASA firewalls interface rather than the IP of the server in the VPN domain, but cannot find that article again.
On the ASA side, I see the traffic selector correct, Server A IP permit any to server B IP.
But on the checkpoint this error, where instead of IP of server A, it is the IP of the ASA interface and 224.0.0.0-224.0.0.255
What does 224.0.0.0-224.0.0.255 mean ?
IKEv2 [NAT-T (IPv4)
auth exchange: sending notification to peer: traffic selectors unacceptable
MyTSi MyTSr:
<has the public IP of the ASA>
<224.0.0.0 - 224.0.0.255>
Peer TSi:
Peer TSr:
<server B IP address>
Hey, G_W_Albrecht, thank you, it helped me.
I've just changed the Tunnel Mode of the VPN Community from"One Tunnel Per Subnet Pair" to "One Tunnel Per Gateway Pair" and all worked, thank you again for posting the sk157473
Best.
Thanks!
That helped me configuring a site-to-site VPN with a Fortigate on the peer side with the same errors in the log!
Christian
This has just helped me out too. Same error message in the logs and same mod to the VPN community did the trick. Thanks. Much appreciated 👍
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 28 | |
| 8 | |
| 5 | |
| 5 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 4 | |
| 3 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION