- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Identity and Trust?
11 November @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Like I said, you need to limit either the destinations, the services, or both.
This advice applies to one or more of 8, 17, 20, 24.
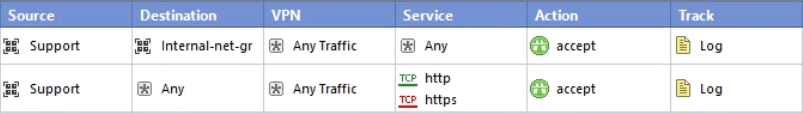
Each one of these rules could easily be two rules.
One example:
Replace http/https with the precise services that are actually required for Internet access and nothing more.
This is by far the most performant approach.
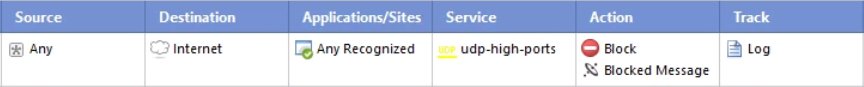
Another option would be to put a rule near the bottom of your App Control rulebase like the following:
To get the Service column to show up in your App Control rulebase, right click on the title bar and check Service.
If you don't want to outright block the traffic, you can instead use the action "Limit" and specify whatever sort of limit you wish to place on this traffic.
Note the limit applies for anything matching this rule and should be below more specific rules.
Please share some additional information if you would like assistance e.g.
- Version & JHF?
- SSL / HTTPS inspection? Y/N
- Classification (hold) mode Y/N
- What alternate rule in the policy is matching the traffic?
yes both FW and Application control rules.
I suspect you're allowing UDP high ports to random places on the Internet, which is generally not best practice. - How do i stop this??
Sorry i am not having much knowledge of firewalls doing just some RnD. Support is not available trying to do it myself.
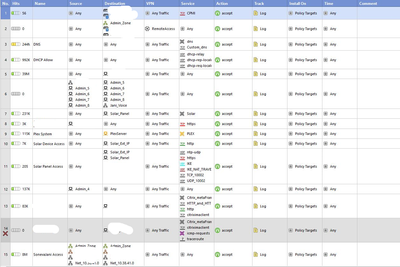
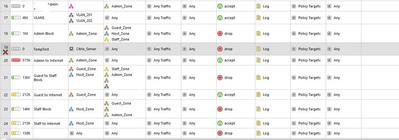
We have some firewall rules which state from any to any. please find the SS attached.
For an effective strategy you will need to limit (reduce) the number of such rules and get more detailed with the permitted services and destinations.
Hi,
i will make sure of that during the installation of latest firewall. for time being i am looking for the solution to block torrent or limit the download speeds(only for torrent not whole interface).
Thanks,
Prashant.
Like I said, you need to limit either the destinations, the services, or both.
This advice applies to one or more of 8, 17, 20, 24.
Each one of these rules could easily be two rules.
One example:
Replace http/https with the precise services that are actually required for Internet access and nothing more.
This is by far the most performant approach.
Another option would be to put a rule near the bottom of your App Control rulebase like the following:
To get the Service column to show up in your App Control rulebase, right click on the title bar and check Service.
If you don't want to outright block the traffic, you can instead use the action "Limit" and specify whatever sort of limit you wish to place on this traffic.
Note the limit applies for anything matching this rule and should be below more specific rules.
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 30 | |
| 15 | |
| 11 | |
| 7 | |
| 5 | |
| 4 | |
| 4 | |
| 4 | |
| 4 | |
| 4 |
Tue 10 Nov 2026 @ 06:00 PM (IST)
Under the Hood: Introducing Check Point Cloud Firewall as a ServiceTue 10 Nov 2026 @ 08:00 PM (IST)
Check Point Mobile Security | Extending Zero Trust with NetskopeThu 12 Nov 2026 @ 11:00 AM (EST)
Tips and Tricks 2026 #15: Check Point MDR and Incident ResponseTue 10 Nov 2026 @ 06:00 PM (IST)
Under the Hood: Introducing Check Point Cloud Firewall as a ServiceTue 10 Nov 2026 @ 08:00 PM (IST)
Check Point Mobile Security | Extending Zero Trust with NetskopeThu 12 Nov 2026 @ 11:00 AM (EST)
Tips and Tricks 2026 #15: Check Point MDR and Incident ResponseTue 17 Nov 2026 @ 08:30 AM (EST)
Bogota Breakfast & Hack: IA bajo control y ataques en vivo con Workspace SecurityAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION