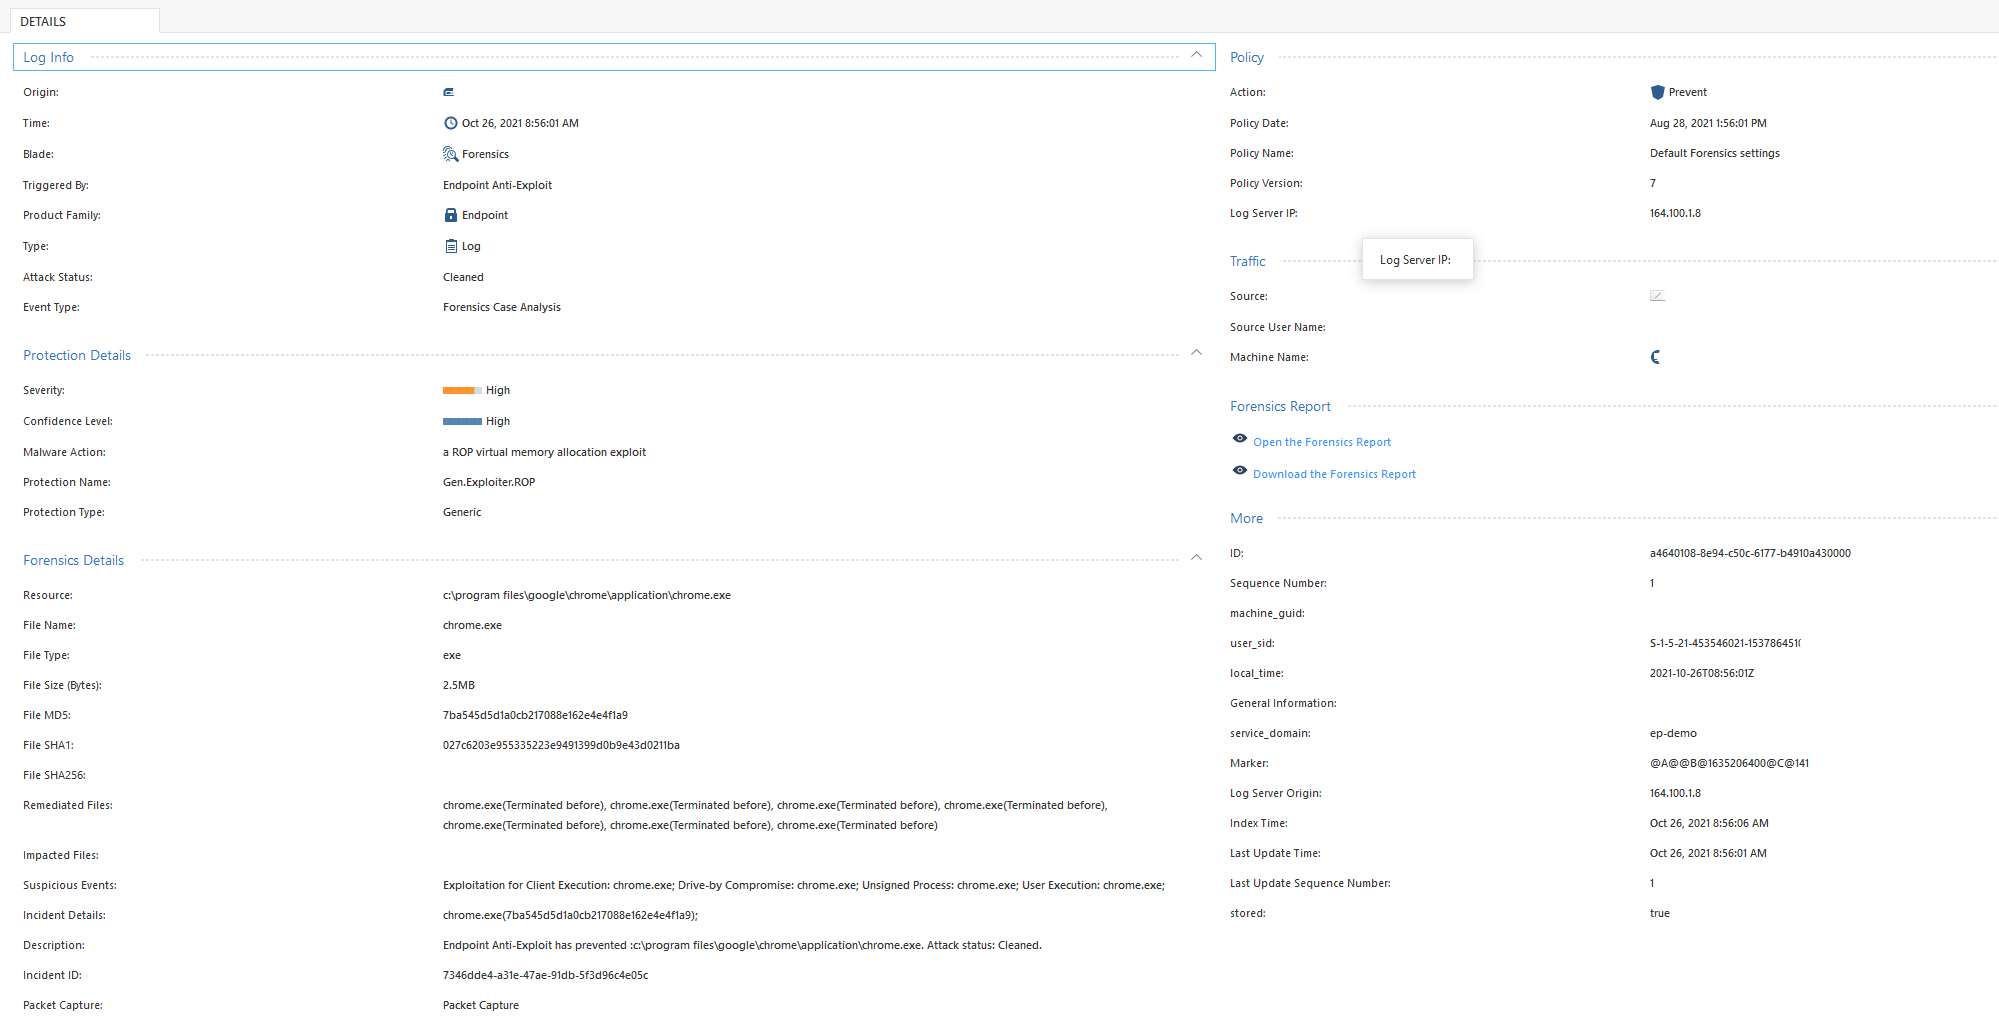
Same for us:
Chrome yesterday for some users, Edge today.
Id: c20e8565-81a0-5410-6177-efad27a60000
Sequencenum: 1
Product Family: Endpoint
Event Type: Forensics Case Analysis
Severity: High
Description: To exclude: Open the Harmony Endpoint Management -> policy -> Threat Prevention -> EXCLUSION CENTER -> Exclusion Settings -> Web and Files Protection -> Threat Emulation... -> + -> SHA1 -> paste this: d3d8253e-3bd458aa-19968b0c-312c774d-26baef79 Attack status: Cleaned.
Client Name: Check Point Endpoint Security Client
Product Version: 85.40.2076
Installed Blades: Firewall; Application Control; Anti-Malware; VPN; Anti-Bot; Forensics; Threat Emulation
Forensics Analysis: 457ab508-d779-4aa7-8720-89b8c60b407a
Triggered By: Endpoint Anti-Exploit
Attack Status: Cleaned
Protection Name: Gen.Exploiter.ROP
Protection Type: Generic
Malware Action: a ROP virtual memory allocation exploit
File Name: msedge.exe
File MD5: fda107354688b32939d7f3e4e286c069
File Type: exe
File Size: 8631461295071690752
File SHA-1: d3d8253e3bd458aa19968b0c312c774d26baef79
File SHA-256:
Confidence Level: High
Policy Name: Default Forensics settings
Policy Date: 2021-09-24T08:32:23Z
Policy Version: 18
Remediated Files: msedge.exe(Terminated before), msedge.exe(Terminated before), (Terminated before), msedge.exe(Terminated before), msedge.exe(Terminated before), msedge.exe(Terminated before), msedge.exe(Terminated before), (Terminated before)
Impacted Files:
Suspicious Events: Exploitation for Client Execution: msedge.exe; Drive-by Compromise: msedge.exe; User Execution: msedge.exe;
Incident Details: msedge.exe(fda107354688b32939d7f3e4e286c069);
General Information:
Service Domain: ep-demo
Action: Prevent
Packet Capture: Packet Capture
Type: Log
Blade: Forensics
Lastupdatetime: 1635250093000
Lastupdateseqnum: 1
Stored: true
Description: To exclude: Open the Harmony Endpoint Management -> policy -> Threat Prevention -> EXCLUSION CENTER -> Exclusion Settings -> Web and Files Protection -> Threat Emulation... -> + -> SHA1 -> paste this: xxxxxxxxxxxxxxxxxxxxxxxxx Attack status: Cleaned.