- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hello,
I want to host a web server which is located behind a aws chexkpoint cluster but i am unable to figure outbhow the traffic from internet will hit the firewall vpc..i have elastic ip in that account which i have mapped with the web server via firewall nat.. But when i try to access it from internet there is no traffic on firewall
Any advice on what i am missing here.
Thanks
Hi @LostBoY,
1) Add a AWS route table to the cluster with the internal networks
2) Add default route to the internet on the gateway.
3) Create a NAT rule:
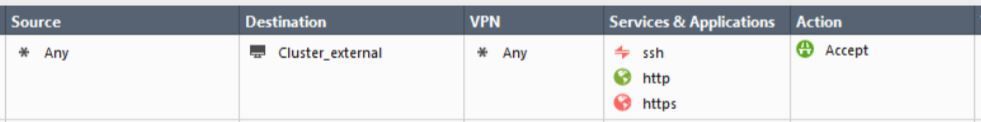
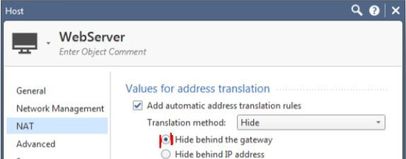
4) Creat a access rule5) Hide NAT for Web Server
6) Check AWS security groups (NACL) for the Elastic IP. Traffic must be allowed from the internet to Check Point firewall (cluster).
Hi @LostBoY,
1) Add a AWS route table to the cluster with the internal networks
2) Add default route to the internet on the gateway.
3) Create a NAT rule:
4) Creat a access rule5) Hide NAT for Web Server
6) Check AWS security groups (NACL) for the Elastic IP. Traffic must be allowed from the internet to Check Point firewall (cluster).
What i cant figure out is .. if i have an EIP by which i want to access the web server via Firewall ..then how do i associate that EIP with Firewall. i mean the routing part ..how will the internet know that for this particular EIP it has to reach this Firewall
If you still need help with this.
ASS now allows you to assign routing tables to the internet gateway in your VPC. So what you do is create a new route table with destination of your internal networks and make the firewalls external interface the hop for these. You then assign the route to the internet gateway. Assign elastic ips like you normally would to the internal hosts. When packets come into your VPC the internet gateway will know to route to the FW instead of directly to your internal host since you created that ingress route table.
Hi, how do I have to add the Elastic IP?
I have multiple subnets attached via network interface to the checkpoint firewall. I got an Elastic IP associated to the network interface that connects the firewall and the subnet where my app server is.
In the checkpoint firewall I added the public IP as an Alias to the interface, and then I made all the steps you described. I also added an entry in the server SG for all traffic from de checkpoint SG (just for testing purposes) and did not worked.
Where should EIP configured for Web server? on CheckPoint VM or another load balancer needs to be configured?
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 3 | |
| 1 | |
| 1 | |
| 1 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaThu 26 Nov 2026 @ 10:00 AM (CET)
The Cloud Architects Series: Cloud Security State in 2026 – Lessons Learned and a Look AheadWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseThu 03 Dec 2026 @ 11:00 AM (EST)
Under the Hood: Check Point Cloud Firewall for Nutanix - How to Secure your AI WorkloadsAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION