- Products
- Learn
- Local User Groups
- Partners
- More

What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hi forum!
My management server has been integrated with azure (I set up the data centre server).
I can read all the objects in Azure. (I'm running R80.10 gateway and mgt)
I have set up Identity Awareness too.
My gateways are not enforcing the rules I have created with datacentre objects! ![]()
Everything looks perfect on the management server, I can even see the IP addresses dynamically associated with the tags!!
I need some help figuring out why the gateways are not enforcing the rules.
I have looked all over for this - and I have a case raised, but TAC have gone a bit quiet!
Anyone help me with locating the documentation for this? I have looked everywhere.
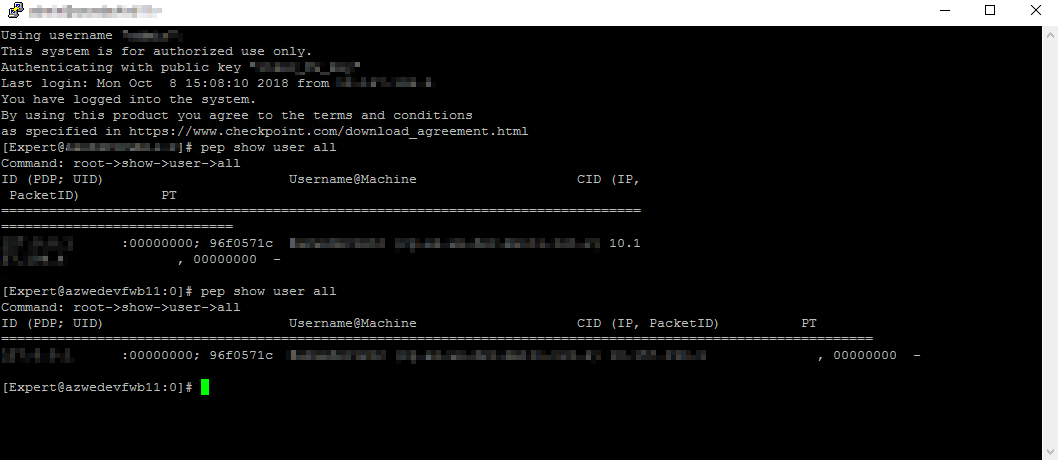
When I do a "pep show user all" (not sure if this shows output on azure integration) i get nothing on the gateway - whcih makes sense.
Are there any logfiles? I have checked /var/log/messages - nothing!
Thanks! ![]()
I think: TAC will know better ![]()
GW side:
"$FWDIR/log/azure_had.elg*" log files.
"$FWDIR/conf/azure-ha.json" log file.
"$FWDIR/log/cloud_proxy.elg" log file.
+
How to troubleshoot Updatable Objects in R80.20 (and higher)
Azure portal reports read and/or write limits, throttling API resources
I'll post up root cause and corrective action when I am done - share the wealth - I suspect it's something I have overlooked!!
Dynamic enforcement enabled!!!!
So I missed out the bold bits
HTH anyone who has the same issue as me ![]()
validate with pep show user all

Data Center objects works also with on-prem GW.
Top response ofirsea040d26-f1f2-3b12-9fc6-5c89debaf56c! I was thinking about getting R80.20 and just blowing away my cirrent install.
Thanks again mate - much appreciated
Hello,
I have problems with that data center objetcs on an VMSS gateway in Azure.
I have enabled the Identity Awareness blade with the autoprov CLI feature. The VMSS gateway has an active Identity Awareness blade, the Remote Web API is checked, and one autogenerated host with IP 127.0.0.1 is added.
I have added the data center object for Azure, and everything is fine, I can seach all objects in my Azure inventory.
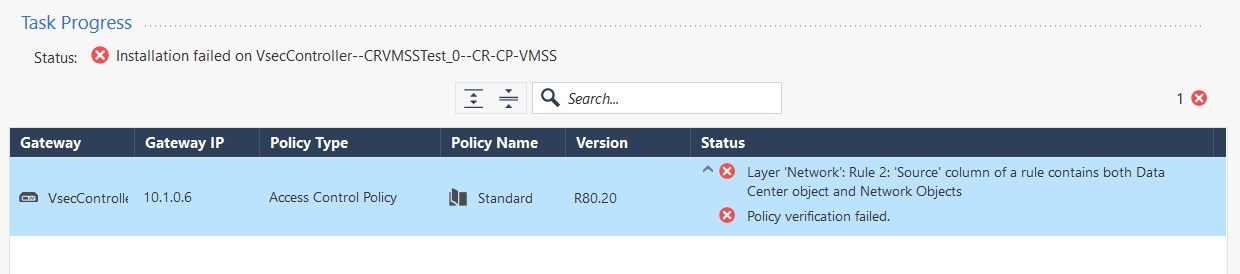
But when I would like to install the policy with one virtual machine from that Azure inventory, I receive an error.
If you have any good advise, because I'm normally familar with that data center objects for on-prem vCenter environments. In my opinion, it should the nearly "the same" for Azure objects...
Management and VMSS gateway is running on R80.20.
Best Regards,
Carsten
Hi Carsten,
Dont panic!
All thats happened it is you must have combined regular objects, and objects learned from Azure in the same source field in the rule
Easiest thing I expect is to duplicate the rule, and in one rule leave the normal objects, and in the other rule put the objects in that are learned from azure
HTH
Upps, life can be so easy when you only read the error message 🙂
You're right Nicholas, that was the problem, it is working now - thanks a lot!
Leaderboard
Epsum factorial non deposit quid pro quo hic escorol.
| User | Count |
|---|---|
| 3 | |
| 1 | |
| 1 | |
| 1 |
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaThu 26 Nov 2026 @ 10:00 AM (CET)
The Cloud Architects Series: Cloud Security State in 2026 – Lessons Learned and a Look AheadWed 02 Dec 2026 @ 02:00 PM (CET)
E-Mail-Agent-Hijacking: E-Mail-Sicherheit im Zeitalter der KI neu überdenkenWed 02 Dec 2026 @ 02:00 PM (GMT)
Why Email Agent Hijacking Marks the End of Post-Delivery Email SecurityWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 02:00 PM (CET)
E-Mail-Agent-Hijacking: E-Mail-Sicherheit im Zeitalter der KI neu überdenkenWed 02 Dec 2026 @ 02:00 PM (GMT)
Why Email Agent Hijacking Marks the End of Post-Delivery Email SecurityWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseWed 02 Dec 2026 @ 11:00 AM (PST)
Why Email Agent Hijacking Marks the End of Post-Delivery Email SecurityAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION