- Products
- Learn
- Local User Groups
- Partners
- More

Scaling Check Point Automation with Arodonata
7 October @ 5pm CET / 11am EDT
What's New in Check Point SASE
The State of Ransomware Q2 2026:
This Quarter's Trends, and Their Impact on Your Defenses
AI Security Masters
Implementing the AI Security Trifecta
CheckMates Go:
Half is Not Enough
Hi All,
Please we have a Site-to-Site VPN between a Head office with Meastro SMO (R81 T44) with VPN defined domain of 192.168.1.0/24 and an assigned LAN interface of 192.168.1.1/24 on the Maestro SMO object / Firewall object.
The remote site is an SMB appliance 1570R with R80.20, its VPN Domain is 172.16.204.0/24 and an assigned LAN interface of 172.16.204.1/24.
The VPN connection is up but we are only able to ping up to the the Local LAN interfaces of the firewalls but not to any LAN connected devices that are directly plugged into the devices. e.g. A device at the Head Office with IP 192.168.1.67/24 can only ping 172.16.204.1/24, but not say 172.16.204.2/24 which directly plugged into the 1570R.
The same reverse situation with pinging from say a device at Head Office with an IP of 192.168.1.67/24 can ping 172.16.204.1/24 but not 172.16.204.2/24 which is directly connected.
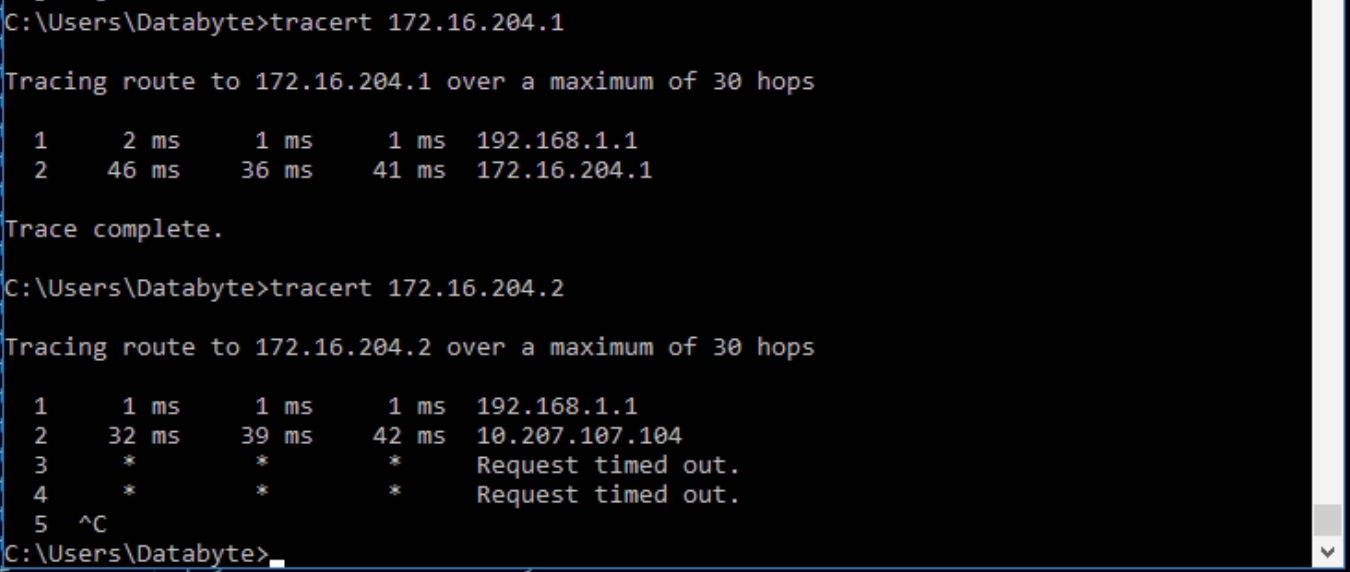
On doing traceroute from the devices I realise that only pings to the LAN interfaces e.g. 172.16.204.1/24 go through the tunnel, although the full subnets are defined correctly in the VPN domain.
Any guidance is much appreciated. Thanks.
Hi All,
Please we have a Site-to-Site VPN between a Head office with Meastro SMO (R81 T44) with VPN defined domain of 192.168.1.0/24 and an assigned LAN interface of 192.168.1.1/24 on the Maestro SMO object / Firewall object.
The remote site is an SMB appliance 1570R with R80.20, its VPN Domain is 172.16.204.0/24 and an assigned LAN interface of 172.16.204.1/24.
The VPN connection is up but we are only able to ping up to the the Local LAN interfaces of the firewalls but not to any LAN connected devices that are directly plugged into the devices. e.g. A device at the Head Office with IP 192.168.1.67/24 can only ping 172.16.204.1/24, but not say 172.16.204.2/24 which directly plugged into the 1570R.
The same reverse situation with pinging from say a device at Head Office with an IP of 192.168.1.67/24 can ping 172.16.204.1/24 but not 172.16.204.2/24 which is directly connected.
On doing traceroute from the devices I realise that only pings to the LAN interfaces e.g. 172.16.204.1/24 go through the tunnel, although the full subnets are defined correctly in the VPN domain.
Any guidance is much appreciated. Thanks.
Hi All,
Please we have a Site-to-Site VPN between a Head office with Meastro SMO (R81 T44) with VPN defined domain of 192.168.1.0/24 and an assigned LAN interface of 192.168.1.1/24 on the Maestro SMO object / Firewall object.
The remote site is an SMB appliance 1570R with R80.20, its VPN Domain is 172.16.204.0/24 and an assigned LAN interface of 172.16.204.1/24.
The VPN connection is up but we are only able to ping up to the the Local LAN interfaces of the firewalls but not to any LAN connected devices that are directly plugged into the devices. e.g. A device at the Head Office with IP 192.168.1.67/24 can only ping 172.16.204.1/24, but not say 172.16.204.2/24 which directly plugged into the 1570R.
The same reverse situation with pinging from say a device at Head Office with an IP of 192.168.1.67/24 can ping 172.16.204.1/24 but not 172.16.204.2/24 which is directly connected.
On doing traceroute from the devices I realise that only pings to the LAN interfaces e.g. 172.16.204.1/24 go through the tunnel, although the full subnets are defined correctly in the VPN domain.
Any guidance is much appreciated. Thanks.