- Products
- Learn
- Local User Groups
- Partners
- More
What’s New in Device Diagnostics?
Dec 2nd @ 5pm CET / 11am EST
AI Security Masters
Security in the Pace of AI:
From Threat to Force Multiplier
CPX is Back!
Join us in Las Vegas, Vienna, and/or Bangkok!
Check Point Named a Leader
The Forrester Wave:
Enterprise Firewall Solutions, Q4 2026
What’s New in Agentic Network Orchestration
CheckMates Go:
Fun Ding
Hello, I'm trying to use the "EventForwarding" configuration to send the logs to my siem, but I'm having problems with the certificate. I entered my company's .crt and .pem certificates, but last step it always complains that the CA is invalid. What could I be doing wrong or what's missing? Thanks!
Could you please share the actual error and more details about the SIEM in use?
Hi , Thanks for your interaction.
Actually I'm trying to send the logs to my current syslog server, it's not a siem. I tried to follow the step by step of the link https://sc1.checkpoint.com/documents/Infinity_Portal/WebAdminGuides/EN/Infinity-Portal-Admin-Guide/C...
But I'm having difficulties in step 3, I tried to insert my company's certificate, but when it goes to CA validate it says it's not valid. It is not very clear in this link the step by step. Could you help me in a more didactic way?
Thanks!!!
Is your CA key a root or is it a sub-CA signed by a different CA?
In that case, I suspect you will need to include all the intermediate certificates to ensure we can validate the entire trust chain.
@PhoneBoy thanks!!
Where do I process the request to download client certificate? I have to sue on my third party. like for example godday, thawte? Or should I do it on my local machine?
Hi,
Please send me the details of you Infinity account to [email protected], and I will have someone take a look and get back to you.
Lior
We're talking about the CA key, right?
That comes from whoever the Certificate Authority is, which should be able to provide you the public key along with all the intermediate public certificates you need.
From what we understand with the command below, the "Private Key" of the CA is needed and we don't have it.
We do have the Public Key as you said, but we haven't identified how to get a Private Key from a CA.
Can we run the command in another way?
openssl x509 -req -in PORTAL.CSR -CA CA.PEM -CAkey CAPRIVATEKEY.key -CAcreateserial -out CERTOUT.CRT -days 825 -sha256
Validation of a Certificate Authority does not require private keys.
However, it does require the public keys of any other CA that has signed your CA certificate.
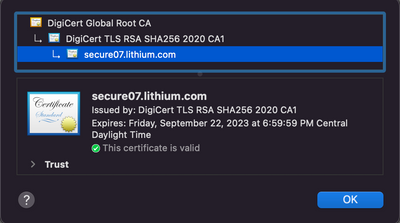
Refer to the following example from this very website you're interacting with me on 🙂
To validate any certificate signed by DigiCert TLS RSA SHA256 2020 CA1, you also need the public key of DigiCert Global Root CA.
Unless your CA is a root, then we need all the public CAs in the certificate chain.
Tue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaThu 26 Nov 2026 @ 10:00 AM (CET)
The Cloud Architects Series: Cloud Security State in 2026 – Lessons Learned and a Look AheadWed 02 Dec 2026 @ 02:00 PM (CET)
E-Mail-Agent-Hijacking: E-Mail-Sicherheit im Zeitalter der KI neu überdenkenWed 02 Dec 2026 @ 02:00 PM (GMT)
Why Email Agent Hijacking Marks the End of Post-Delivery Email SecurityWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseTue 24 Nov 2026 @ 01:30 PM (GMT)
La nueva realidad de los ataques DDoS: autonomía, escala y el futuro de la defensaWed 02 Dec 2026 @ 02:00 PM (CET)
E-Mail-Agent-Hijacking: E-Mail-Sicherheit im Zeitalter der KI neu überdenkenWed 02 Dec 2026 @ 02:00 PM (GMT)
Why Email Agent Hijacking Marks the End of Post-Delivery Email SecurityWed 02 Dec 2026 @ 03:30 PM (GMT)
The New DDoS Reality: Autonomy, Scale, and the Future of DefenseWed 02 Dec 2026 @ 11:00 AM (PST)
Why Email Agent Hijacking Marks the End of Post-Delivery Email SecurityAbout CheckMates
Learn Check Point
Advanced Learning
WE SECURE YOUR AI TRANSFORMATION